HIPAA Compliance Checklist for 2025

Finding employees using ChatGPT, Claude, Gemini, or other unapproved AI tools is a good start. But discovering these applications doesn't tell IT what to do about them.
An employee might use an AI assistant to summarize meeting notes. Another might upload confidential company documents. Both activities involve Shadow AI, but they don't carry the same level of risk.
Simply blocking every unapproved tool isn't the answer either. Employees will find alternatives, often without informing IT. IT teams need to understand which tools employees use and determine which ones are worth keeping.
Here's what IT should do after discovering Shadow AI across the organization.
1. Why Is Finding Shadow AI Only the First Step for IT?
Visibility alone doesn't establish control over shadow AI applications. An employee starts using an AI writing assistant. IT discovers the application through browser activity. But several questions remain:
- Does the employee use it for personal productivity or company work?
- What information does the employee share with the application?
- Does the application retain prompts or use submitted data for model training?
- Are employees already paying for individual subscriptions?
- Does the organization have an approved alternative?
Without these answers, IT cannot make informed decisions about the application.
Discovery also doesn't address what happens next. Employees may continue using the same tools, new applications may appear, and existing usage may expand across departments.

2. What Should IT Do After Finding Shadow AI?
Once IT has identified Shadow AI applications, the next step is to understand their usage and decide how each application should be handled.
A. How Should IT Sort Shadow AI Tools by Risk?
Not every unapproved AI application deserves the same response. IT should evaluate applications based on how employees use them, what data they handle, and whether they serve a legitimate business need.
So here are three categories IT should follow to group discovered applications:
These categories are starting points. IT should evaluate each application against a few practical criteria:
- Data handling: Does the application store prompts, retain uploaded files, or use customer inputs for training?
- Business usage: Which teams use it, and what work does it support?
- Account ownership: Are employees using personal accounts or organization-managed accounts?
- Existing alternatives: Does the company already provide an approved tool with similar capabilities?
- Vendor transparency: Does the provider clearly explain its data retention and administrative controls?
This assessment helps IT prioritize applications that need immediate attention instead of treating every discovery as an emergency.
B. How Should IT Decide to Approve, Restrict or Retire a Tool?
After evaluating an application, IT needs to decide whether employees can continue using it. There are three practical outcomes:
1. Approve the application
Approve tools that support legitimate business needs and offer acceptable data handling practices. Where possible, move employees to organization-managed accounts with centralized administration.
2. Restrict its usage
Some applications may be useful but unsuitable for unrestricted access. IT can limit their use to specific departments, user groups, or approved workflows.
For example, an AI assistant might be acceptable for public information but restricted from processing customer records or proprietary code.
3. Retire the application
Remove applications that offer little business value, duplicate existing capabilities, or lack acceptable controls.
Before removing access, identify employees who depend on the application. Provide an approved alternative so their workflows don't break.
The goal isn't to eliminate AI usage. It's to ensure employees use applications that IT can support and manage.
C. How Do You Talk to Employees Already Using Unapproved AI?
Employees rarely adopt unauthorized AI tools without a reason. They might be trying to reduce repetitive work, finish tasks faster, or overcome limitations in existing software.
IT should understand that motivation before introducing restrictions.
Instead of sending a blanket warning, approach employees and department leads with specific questions:
- What tasks are you using this AI application for?
- What makes it more useful than the tools already provided?
- What type of company information do you enter?
- Would you switch to an approved alternative if it offered similar functionality?
This conversation can uncover legitimate business requirements that existing IT tools don't address. It also helps IT identify employees who could become internal advocates for approved AI applications.
When employees understand why certain tools are restricted and know which alternatives they can use, they're more likely to follow the process.
3. How Can IT Set Up an AI Approval Process People Will Use?
Managing existing Shadow AI is only part of the challenge. IT also needs a repeatable way to evaluate new applications before employees start using them.
A complicated approval process creates another problem. Employees may avoid it because waiting several weeks for an application approval defeats the purpose of adopting AI.
A practical approval process should be accessible, predictable, and easy to follow.
A. What Should an AI Tool Review Checklist Include?
IT can introduce a standardized checklist that employees or department leads complete when requesting a new AI application. The checklist should capture the information needed to make an informed decision.
Once employees submit a request, IT can review the application and determine whether it meets the organization's requirements.
B. How Do You Control AI Tool Access After Approval?
Approving an AI application doesn't mean every employee should automatically receive access. IT should manage access based on business requirements and employee responsibilities.
A few practices help maintain control:
- Use organization-managed accounts: Avoid fragmented subscriptions and unmanaged personal accounts.
- Assign access by department: Give applications to teams that have a defined business requirement.
- Use role-based permissions: Limit access to features and data relevant to each employee's responsibilities.
- Review access periodically: Identify employees who no longer need an application or have changed roles.
- Remove access during offboarding: Revoke application access when employees leave the organization.
IT should also maintain an updated inventory of approved AI applications, their owners, assigned users, and renewal dates.
4. How Does CloudEagle.ai Help IT Teams Govern Shadow AI?
Employees adopt AI tools faster than IT can review them, through free assistants, personal accounts, browser tools, and AI features built into existing apps.
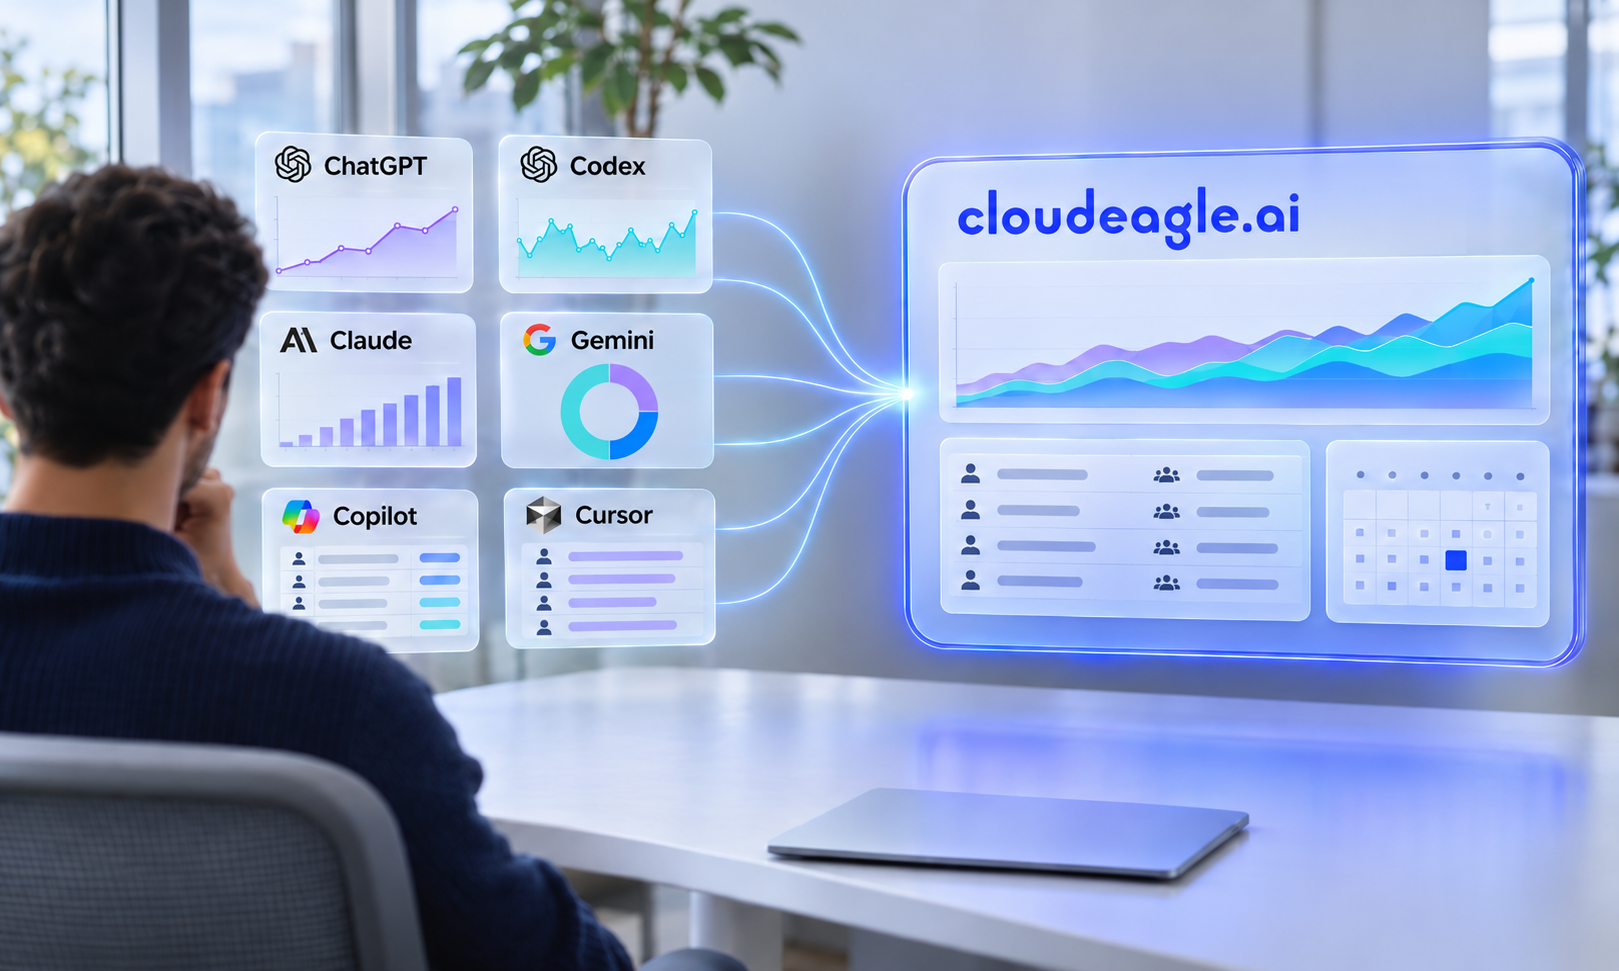
CloudEagle.ai, a unified platform for AI governance, SaaS security, identity governance, and shadow AI detection, helps IT teams stay in control without blocking the people who want to use AI.
- See everything: Seven layers of discovery combine signals from SSO, browser activity, finance systems, and security tools, so you find AI tools that SSO alone misses.
- Focus on real risk: Risk scores based on security posture, data residency, training data use, and compliance alignment show which tools need approval, restrictions, or blocking.
- Redirect, don’t just block: Secure Browsing sends employees from unapproved tools to an approved alternative, and logs each redirect for audit.
- Protect sensitive data: DLP checks prompts for PII, PHI, financial data, and source code before they reach the AI model.
- Keep AI spend in check: Track usage by user, department, and model, set budgets with alerts, and spot unused AI licenses.
- Govern AI agents: Inventory supported AI agents and non-human identities, then review their owners and permissions.
The result: employees keep using approved AI tools, while IT keeps visibility into risk, data exposure, access, and cost.
Know Every AI Tool. Control Every Risk.


5. Conclusion
Finding Shadow AI gives IT the visibility needed to understand how employees adopt AI applications. But discovery is only useful when it leads to informed decisions.
IT teams should evaluate discovered tools, understand employee requirements, approve applications through a straightforward process, and manage access continuously.
The objective isn't to stop employees from using AI. It's to make AI adoption manageable without creating unnecessary friction for the people using it.
When IT provides clear alternatives and an accessible approval process, employees have fewer reasons to work around established technology policies.
6. FAQs
1. What should IT do after discovering Shadow AI?
IT should evaluate discovered applications, assess their business usage, approve or restrict access, and establish an ongoing AI application management process.
2. Should IT block all unapproved AI tools?
No. IT should evaluate each application based on its business value, data handling practices, and available alternatives before deciding whether to approve, restrict, or block it.
3. Who should manage Shadow AI in an organization?
IT should lead Shadow AI management by maintaining application visibility, evaluating employee requirements, managing access, and establishing an AI approval process.
4. How can employees request approval for new AI tools?
Employees should submit an application request explaining its business purpose, intended users, data requirements, and expected benefits. IT can then evaluate the application against a standardized checklist.
Don't Let Shadow AI Run Your Enterprise.