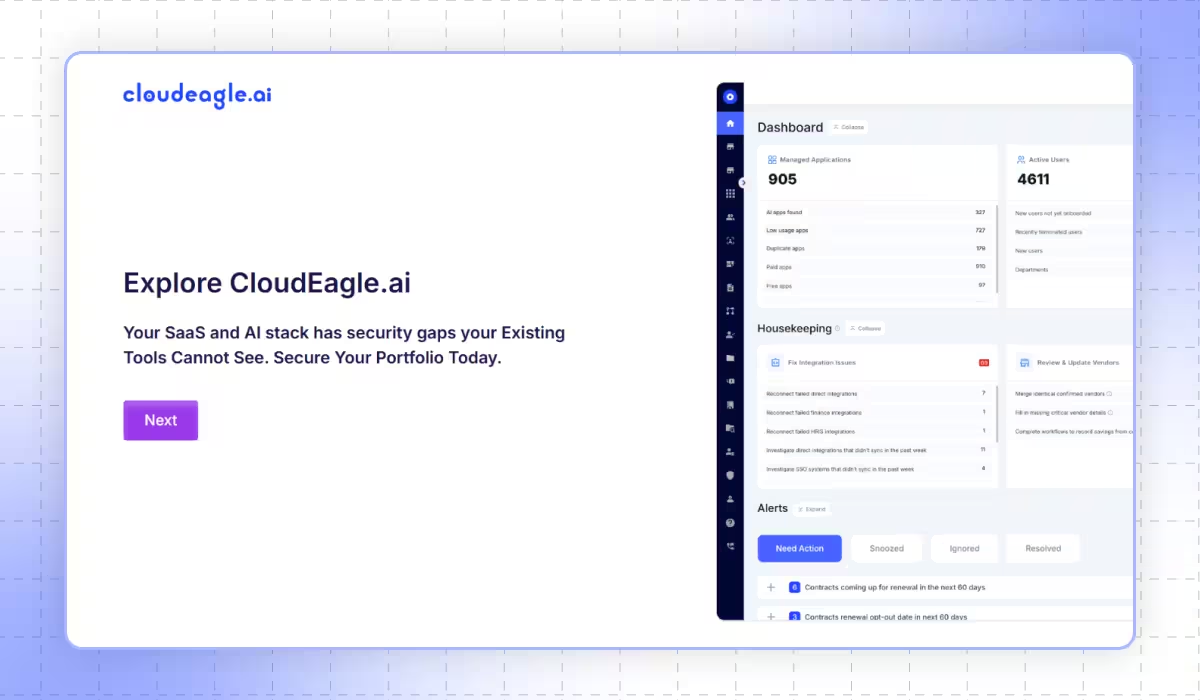
Secure every SaaS app, AI tool, identity, and machine credential in your environment from a single platform.
CloudEagle.ai For Security Teams
Every Risk Visible. Every Identity Governed. Every Audit, Ready.
Shadow AI on personal accounts. Orphaned service accounts with standing access. SaaS apps nobody approved. Find every risk across your environment and shut it down, before an auditor or an attacker does.

Trusted by High-growth Enterprise to Secure their Tech Stack




Testimonials
What Security Teams Find
"Every SOC 2 cycle we spent two weeks pulling access evidence manually, exporting lists, chasing managers for sign-offs, and reconciling spreadsheets. CloudEagle automated the reviews and produced the evidence packets in a day. Our last audit had zero access-related findings. That had never happened before."

Pedro Sors
Chief Operating Officer

“As our environment scaled, reviewing privileged access across applications became increasingly difficult and risky. CloudEagle helped us bring structure and focus to privileged access reviews, so our teams could concentrate on high-risk access with confidence.”
Barnaby Go
IT Manager
"CloudEagle.ai gave us visibility into service accounts, API tokens, and AI agents, helping increase NHI visibility, remediate unmanaged identities, and reduce overprivileges, helping us govern NHI, the same way we did for people."
Karthik Swarnam
Chief Security and Trust Officer

“We had 287 approved SaaS vendors. CloudEagle showed us that 63 had quietly become GenAI platforms, and 11 were training on our data by default. We switched AI training off in 8 of them in a single afternoon. The other 3 went straight into access lockdown while we worked out the rest.”
Vineet Gopal
Head of Technology,
Secure AI and SaaS Without Blindspots
Govern and Secure AI With Confidence
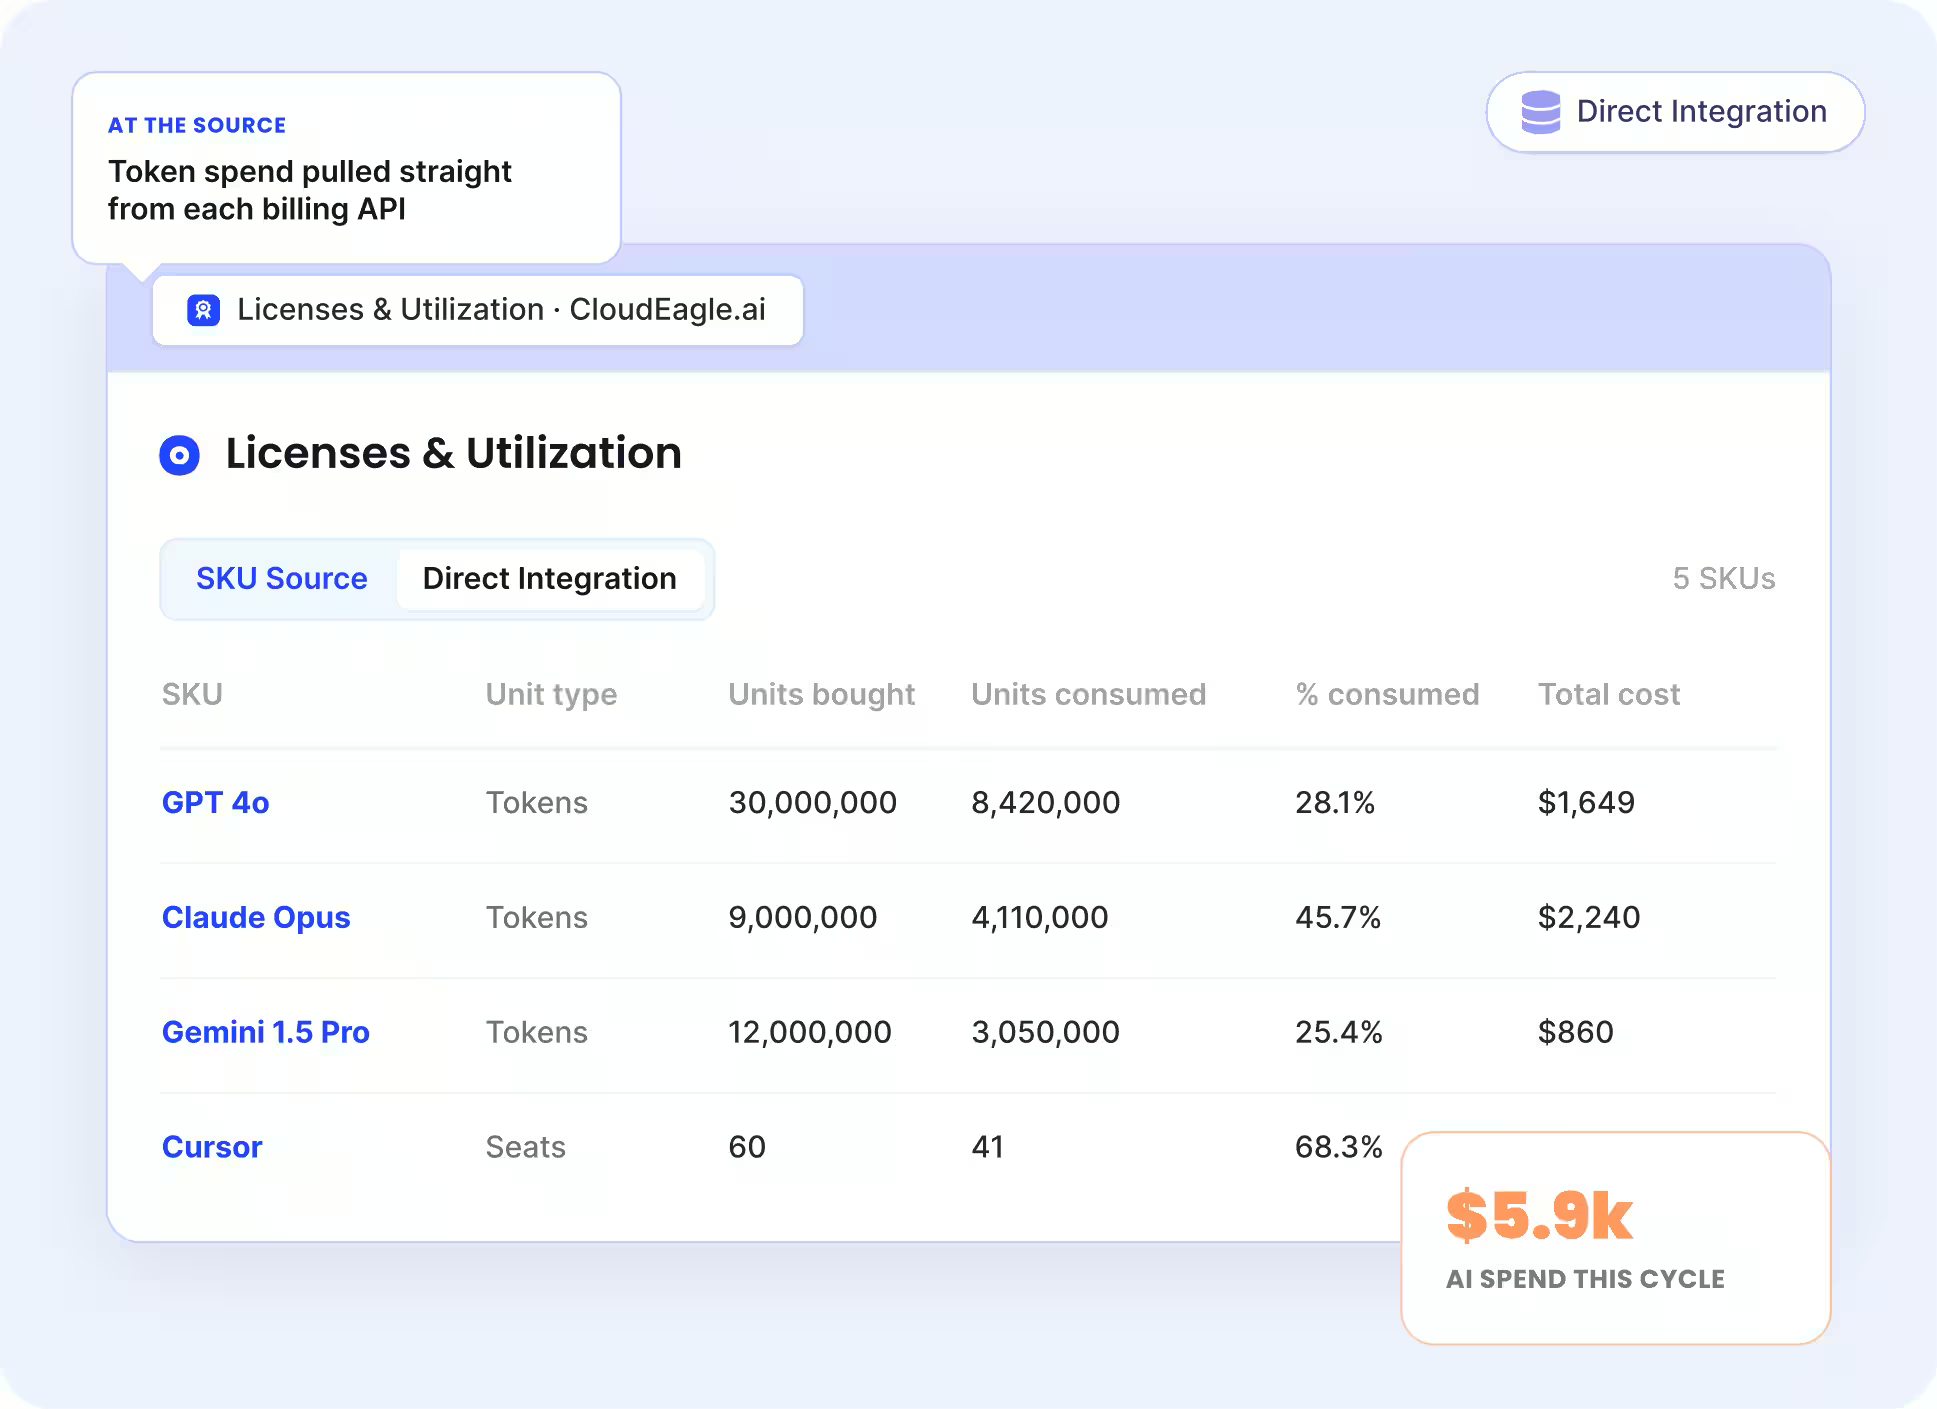
Stop guessing where AI is being used. Continuously discover every AI tool in use, flag shadow AI, and risk-score every application so you know which vendors to review first.
Discover every approved, shadow, and unsanctioned AI app
Catch orphaned accounts and unreviewed API tokens before they're a risk
Block sensitive data uploads, redirect users off unsanctioned tools
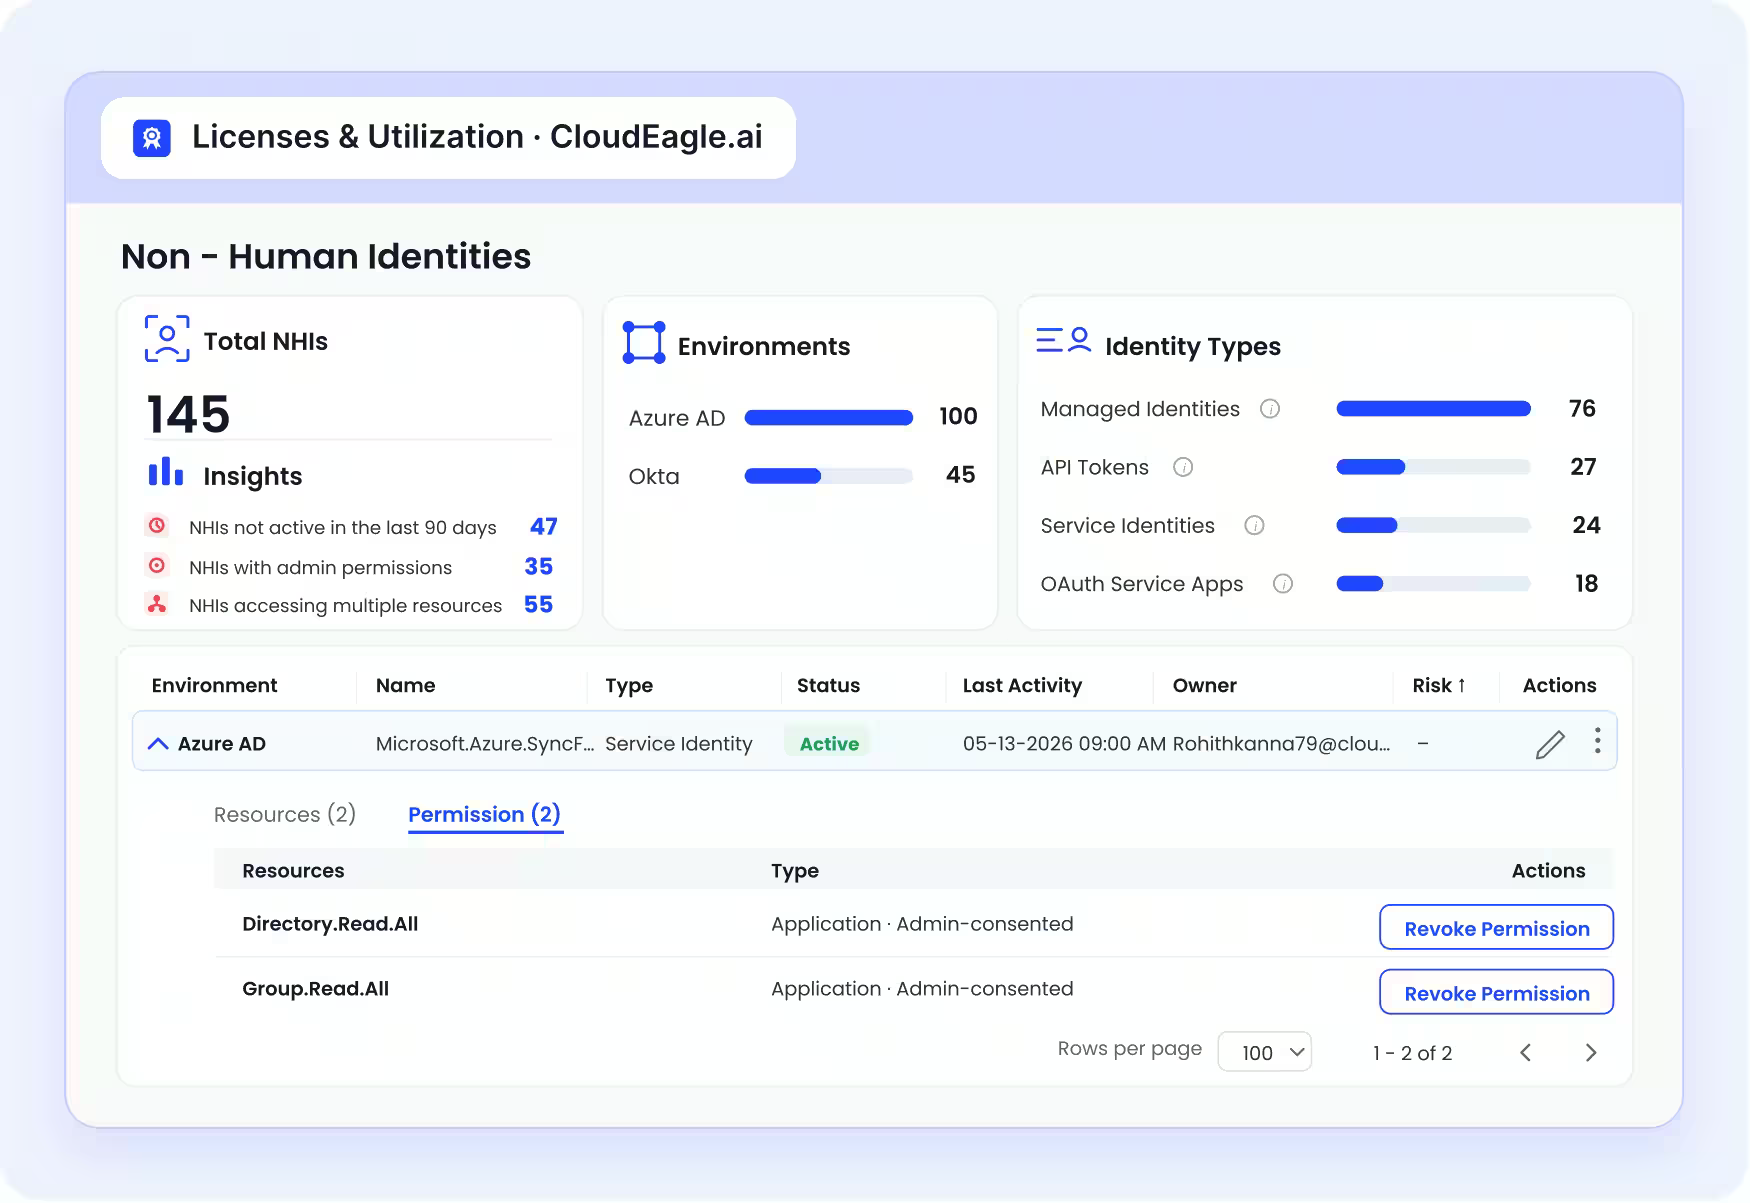
Close the Gaps Machine Identities Gaps
Govern non-human identities with the same rigor as human users. Discover every machine identity, see what it can access, and revoke standing access the moment it's orphaned or unowned.
Every service account, API key, bot, and AI agent, correlated from Okta, Entra, and other IdPs
See current status, owner, and permissions for every non-human identity
Revoke standing access from orphaned or unowned identities before they become a breach
Access Reviews That Don't Slow Security Down
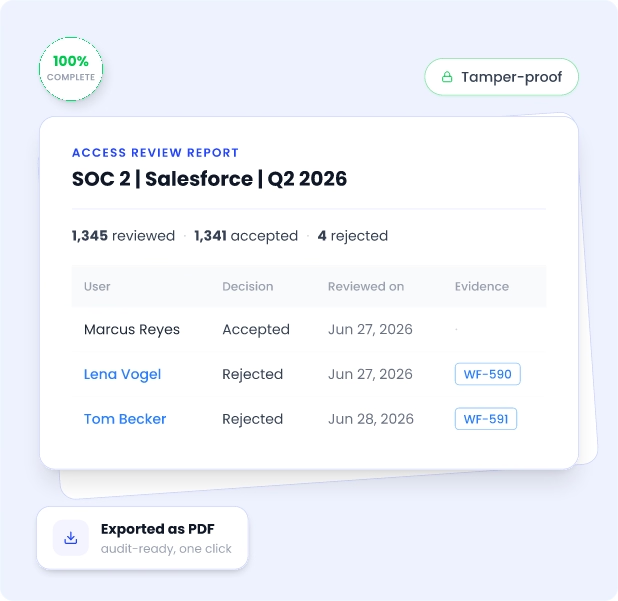
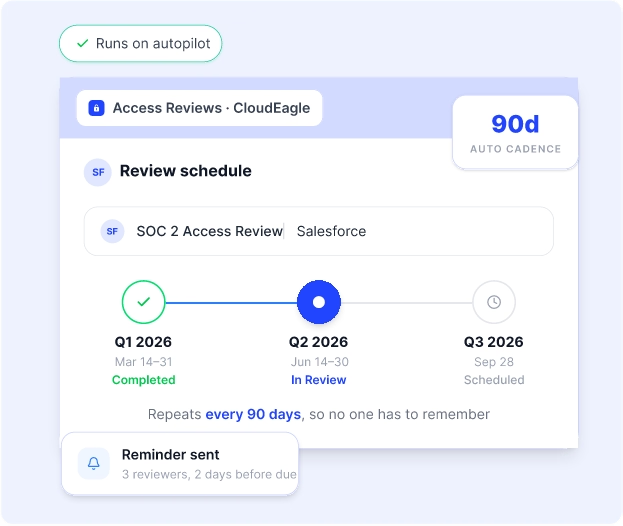
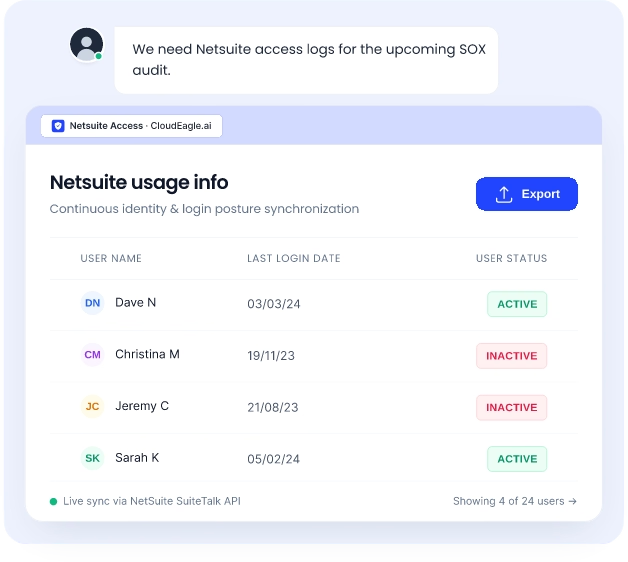
Stop chasing managers for approvals. High-risk users and excessive privileges are flagged automatically, and when access is revoked, deprovisioning and audit evidence happen in the same step.
Continuous access reviews across all connected apps, not a quarterly fire drill
High-risk users, excessive privileges, and ex-employees flagged automatically
Deprovisioning and audit evidence captured in the same step, no manual follow-up
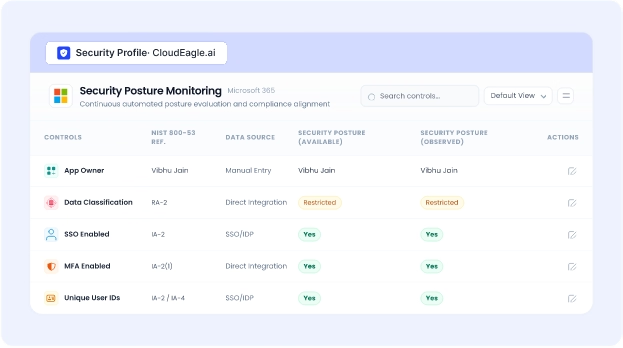
Replace Point-in-Time Audits with Continuous Posture
Get a single, always-current view of MFA enforcement, SSO coverage, and security posture across every app, mapped against frameworks like NIST 800.
Security posture tracked continuously across the entire SaaS stack, not checked app by app
Pass/fail compliance status per app, measured against NIST 800 and other frameworks
Board-ready and auditor-ready on demand, not assembled under pressure
Eliminate Excessive Privileges Before They Become a Risk
See every privileged and admin user across every connected app, with full context on role, activity, and whether that level of access is still appropriate.
Full visibility into privileged and admin users, and non-human identities
Over-provisioned access flagged continuously, not just at review time
Downgrade or revoke excessive privileges and implement least-privileges
Centralized Vendor Risk and Compliance Intelligence
Every vendor's security documentation, risk score, and compliance status in one place. When a tool is up for renewal or a new vendor is being evaluated, the security review is already done.
Vendor security profiles with SOC 2, ISO 27001, HIPAA, and DPA documentation centralized
Risk scores for every SaaS and AI vendor, including AI-specific factors like training data use and data residency
Vendors whose security posture has changed since your last review surfaced automatically
See Your SaaS Security Blind Spots Before Attackers Do
Frequently Asked Question
Can't find the answer you're looking for? Contact us, and our team will be happy to help.
Contact Us1. Does CloudEagle.ai replace our CASB?
No. CASBs cover traffic at the network layer. CloudEagle.ai works at the app and identity layer, picking up AI tools on personal accounts, apps on personal devices, and anything outside your perimeter. Most customers run both. CloudEagle.ai ingests signals from your existing security tools and adds app-layer governance, identity controls, and spend attribution on top.
2. How does it handle access reviews for apps outside our IDP?
CloudEagle.ai connects directly to apps via API, including tools that aren't SCIM-compatible, and pulls user access data from every connected system. Reviews cover the full app estate, not just what's behind Okta or Entra. When access is revoked, deprovisioning runs through the same connection and evidence is captured automatically.
3. What are non-human identities and how does CloudEagle.ai govern them?
Service accounts, API keys, bots, and AI agents, anything that accesses your systems without being a person. CloudEagle.ai surfaces every one of them, shows you owner, permissions, and connected resources, and brings them into the same lifecycle controls you already use for employees.
4. How does AI policy enforcement work, is it a hard block?
The default is a soft redirect. When an employee tries to access an unapproved AI tool, they're redirected to the approved alternative before anything is submitted. Hard blocking is available, but most customers start with soft enforcement because hard blocks create workarounds fast. The redirect enforces the policy while giving employees a clear path to the right tool.
5. How quickly can we see our full SaaS and AI footprint?
Most teams see their complete app and AI inventory within the first session. Average onboarding is 30 minutes.
6. We already run access reviews manually. What's different?
Manual reviews run quarterly, rely on exports, and get rubber-stamped because reviewers don't have enough context. CloudEagle.ai makes reviews continuous, surfaces full user context automatically, and flags high-risk users before a reviewer has to find them. Deprovisioning and evidence collection happen inside the review, not after it.
7. How does security posture tracking work?
CloudEagle.ai pulls MFA and SSO status directly from your identity provider, pulls compliance data via API where available, and fills gaps with broader risk scoring. Everything rolls up into one dashboard showing pass/fail status per app, updated continuously.
8. Can it help us prepare for a SOC 2 or ISO 27001 audit?
Yes. Every access change is logged, every deprovisioning is documented, and every access review is tracked with completion status. When an auditor asks for evidence, it's already there.
Read More
How security teams run on CloudEagle.ai
The capabilities behind an accurate spend picture, and the thinking behind it, across the platform.
EXPLORE THE PLATFORM

SaaS Security and Compliance
Secure your AI and SaaS ecosystem


Shadow AI & Shadow IT
Discover unsanctioned AI and SaaS apps

Privileged User Management
Enforce least-privilege access across organization

Access Reviews
Run automates user access reviews

AI Governance
Govern AI apps and control token consumption
AI Policy Enforcement
Cut overlapping tools with usage and spend data
GO DEEPER
AI security guide: risks & best practices for 2026
The real AI risks, data exposure, and the controls that stop them
Why every non-human identity needs an owner
Unowned NHIs are one of the fastest-growing risks in enterprise SaaS

Domo got usage and spend visibility into Claude, Gemini, and Cursor
Found 34% of AI licenses inactive, saved $1.2M in one quarter
The AI-powered future of IGA
How AI is reshaping identity governance

Managing SaaS risk and compliance
Rethinking compliance posture when 60% of SaaS and AI runs outside IT visibility

Shadow AI risk assessment calculator
10 questions to uncover your exposure score