CloudEagle.ai For IT Teams
One Governance Layer for Every App, Identity, and AI Tools
Govern every AI tools, SaaS, and NHIs the moment it enters your stack. Shut down shadow AI, close compliance gaps, and walk into every budget review with hard proof of ROI, without adding headcount.

Trusted by IT Teams in High-growth Companies




What IT Teams Find



The Unified IT Command Center for AI, SaaS and NHI
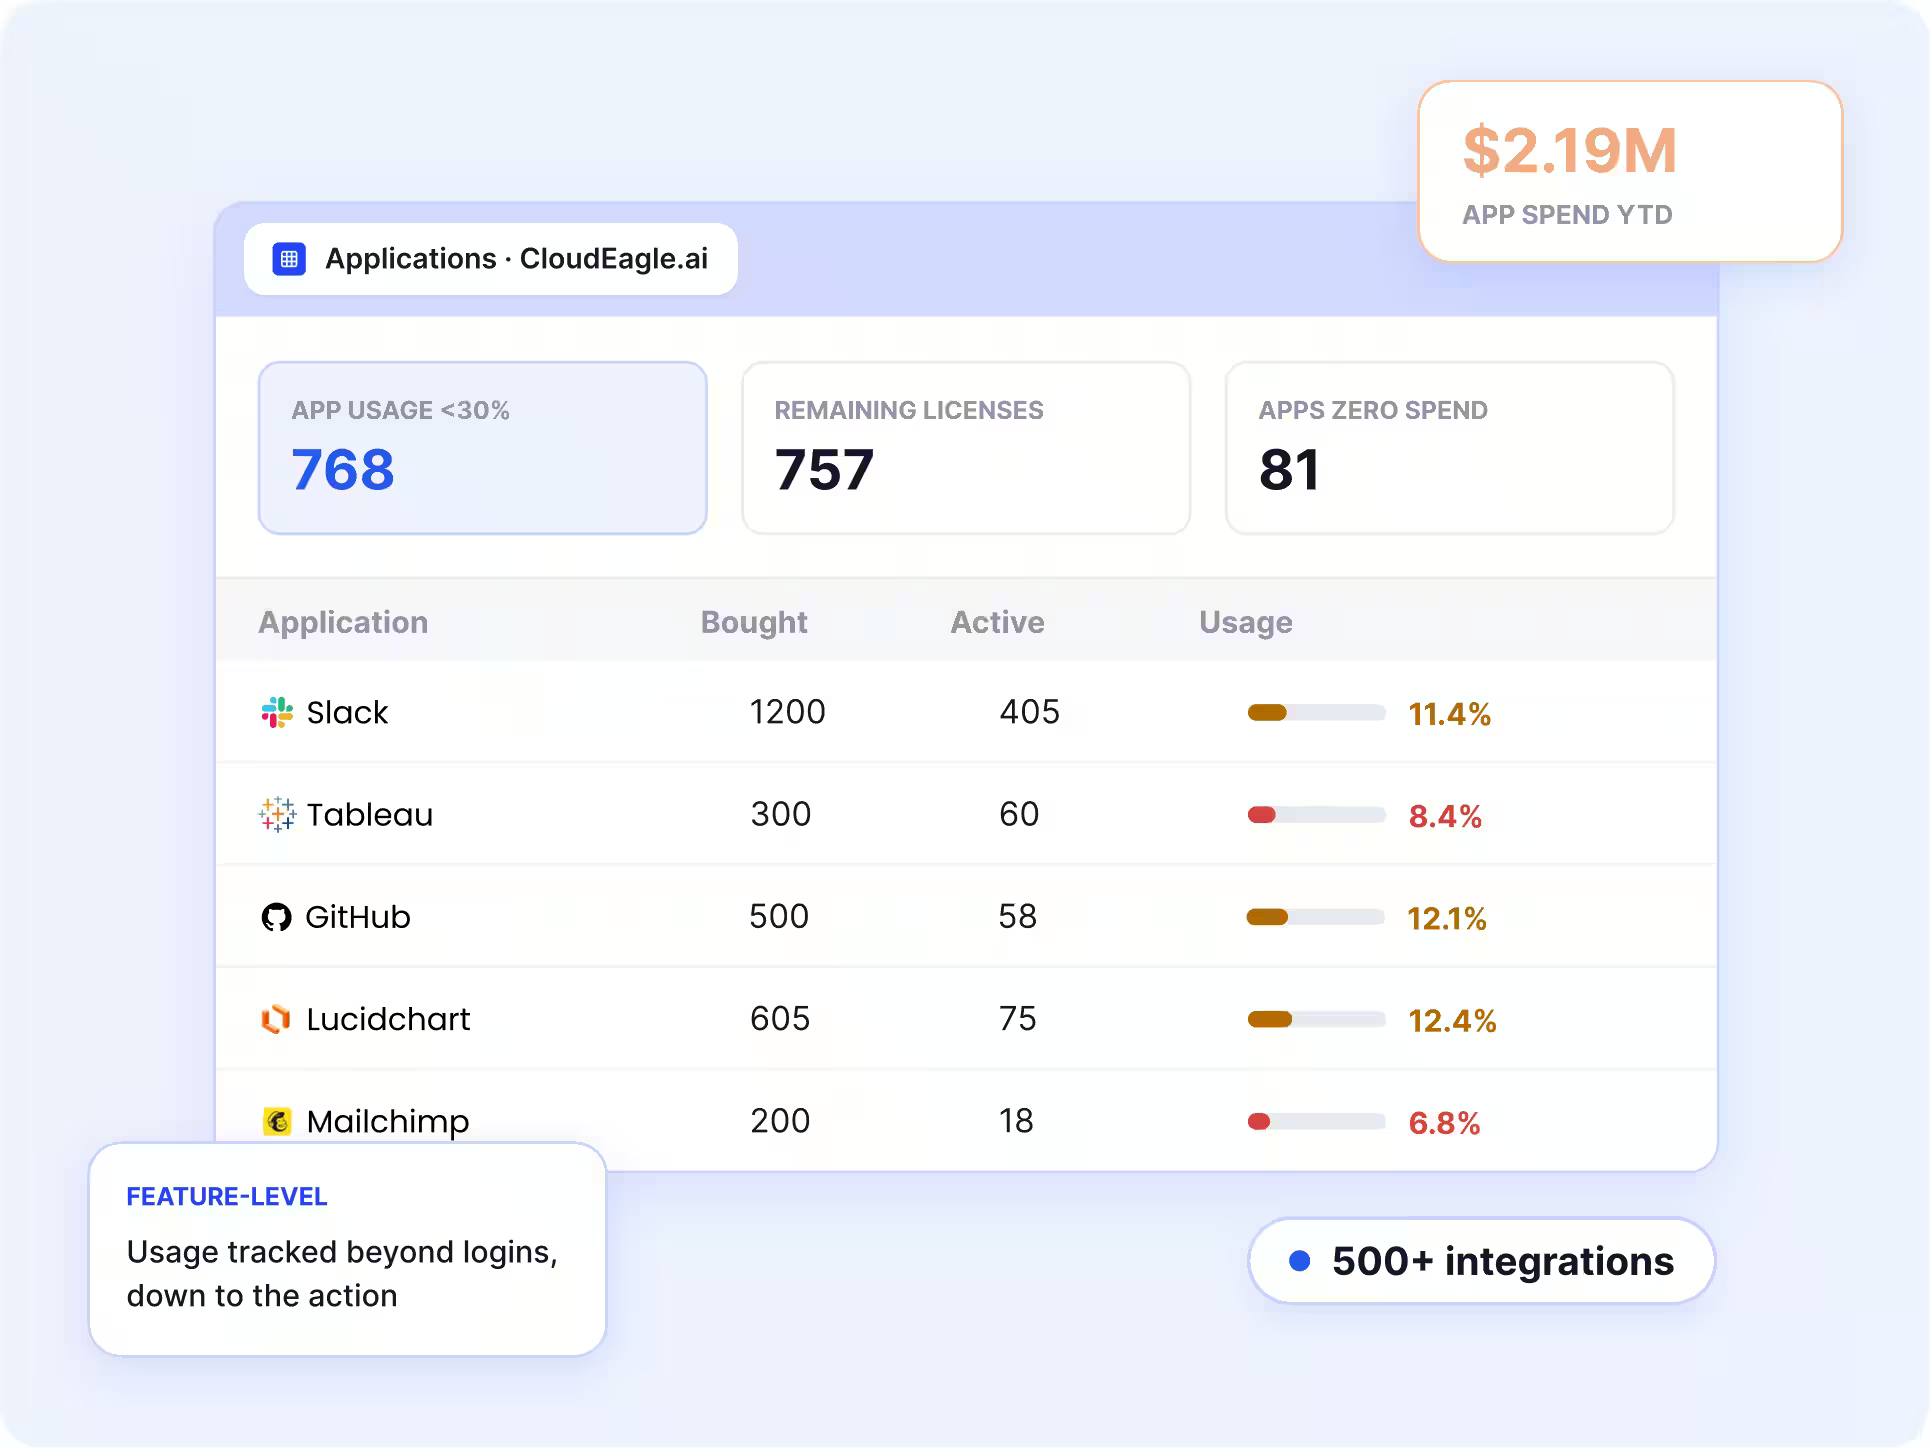
Employees are signing up for AI tools you don't know about.
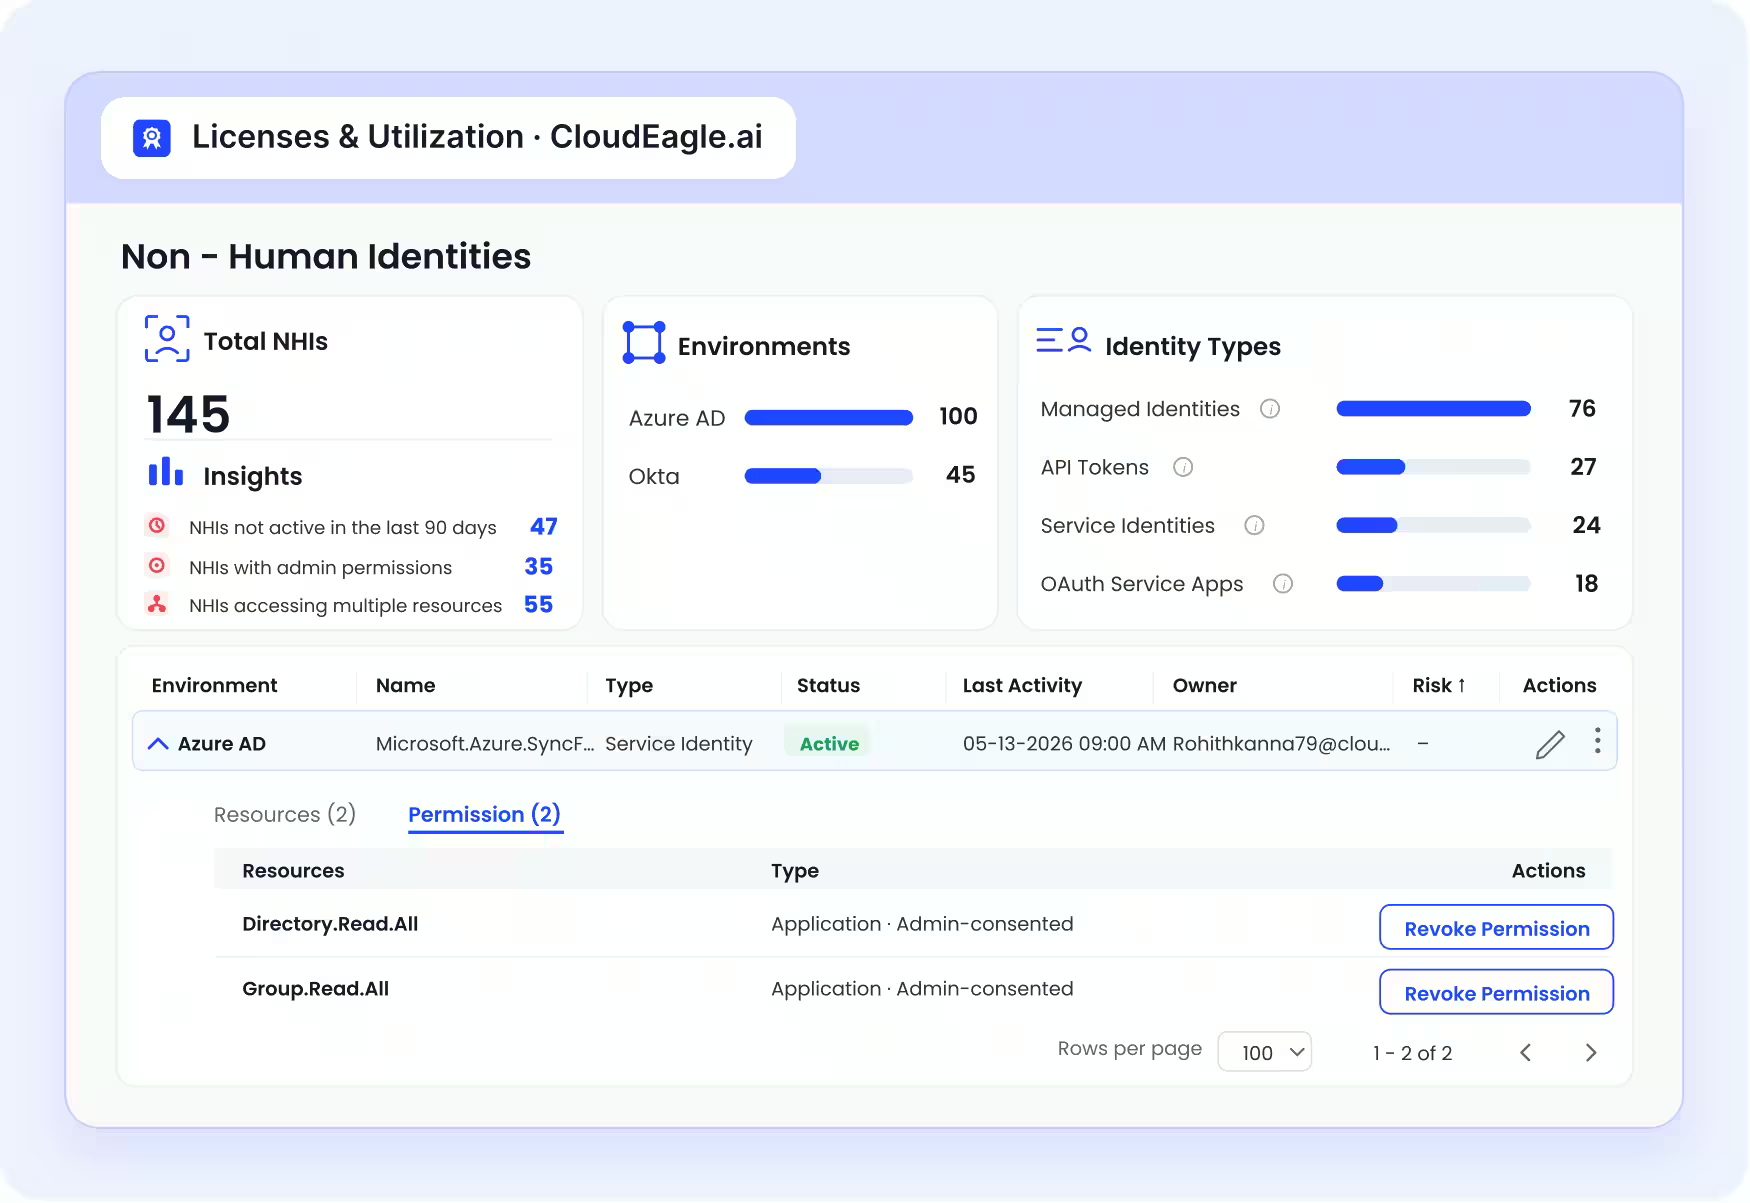
Govern Every Non-Human Identity from One Place
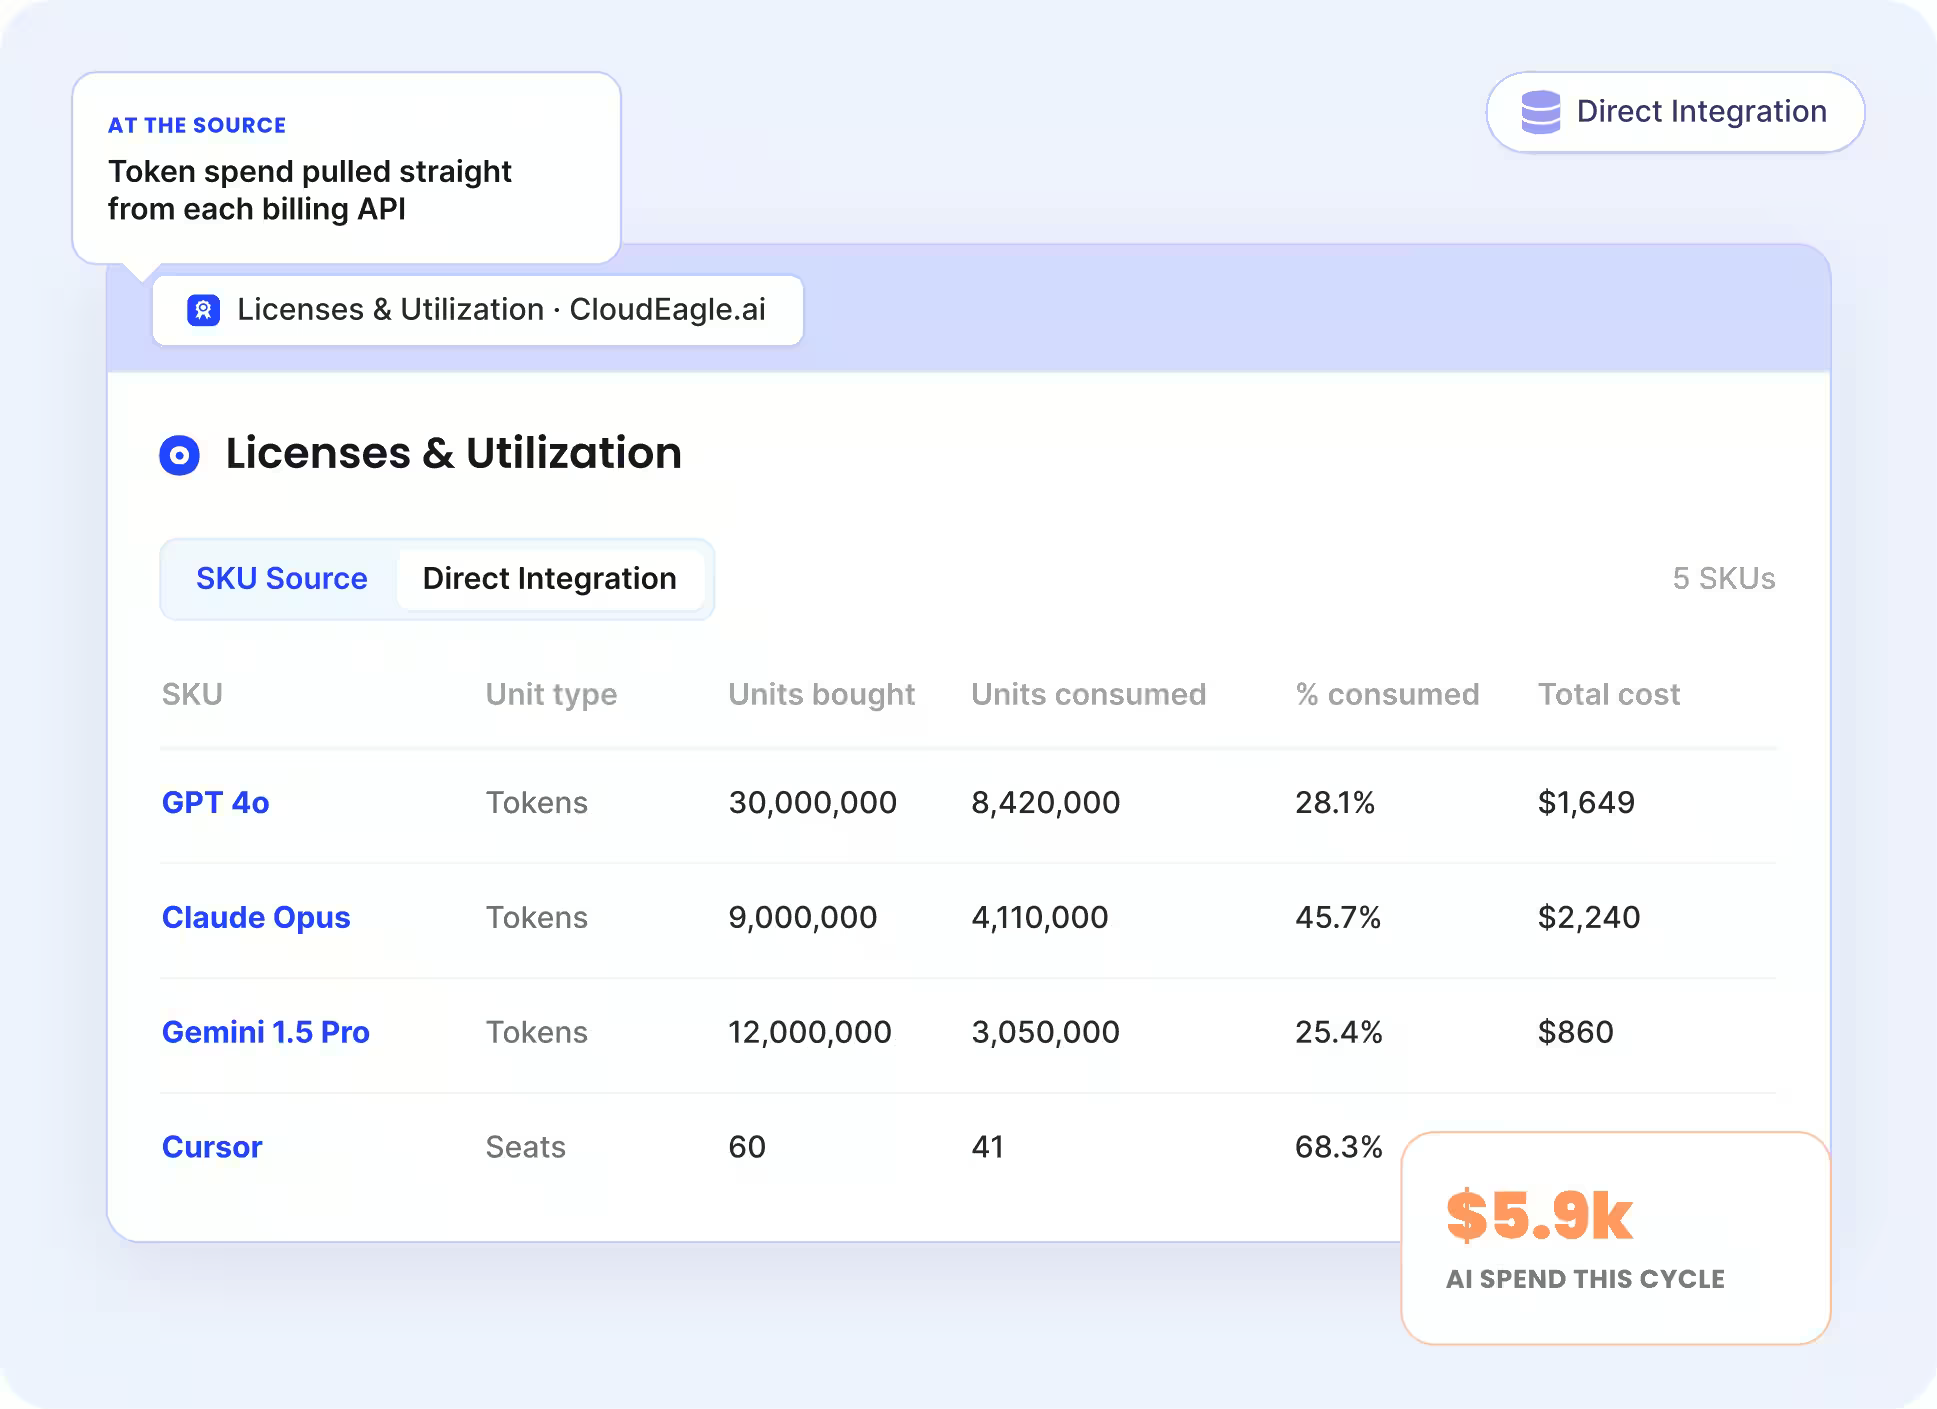
License management without the spreadsheet
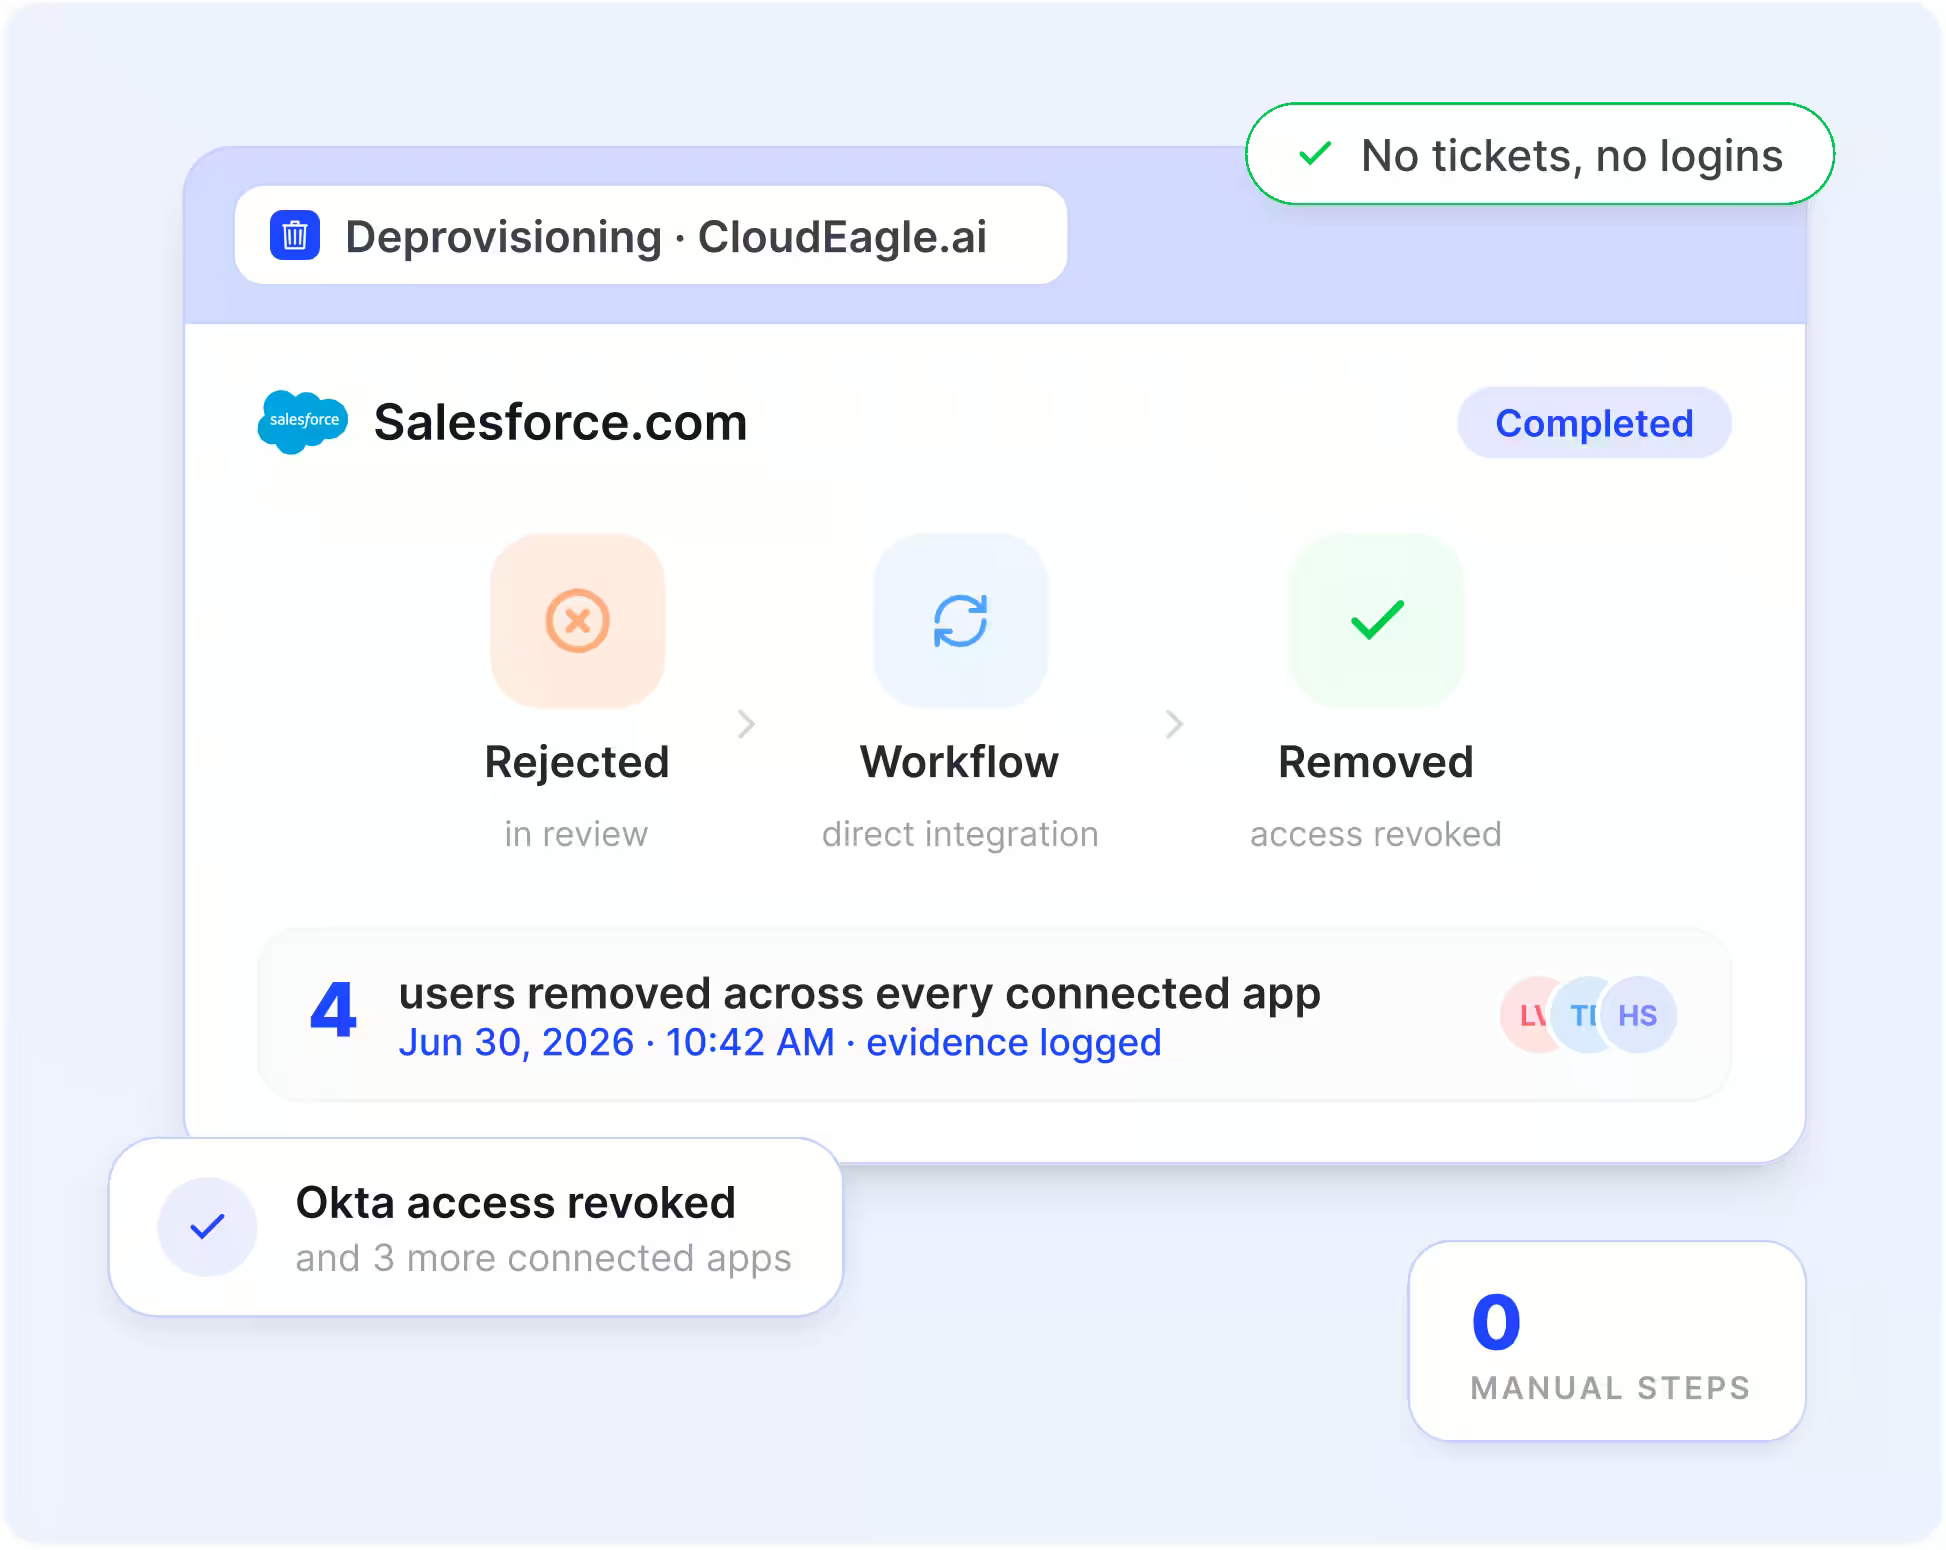
Onboarding and offboarding on auto-pilot.
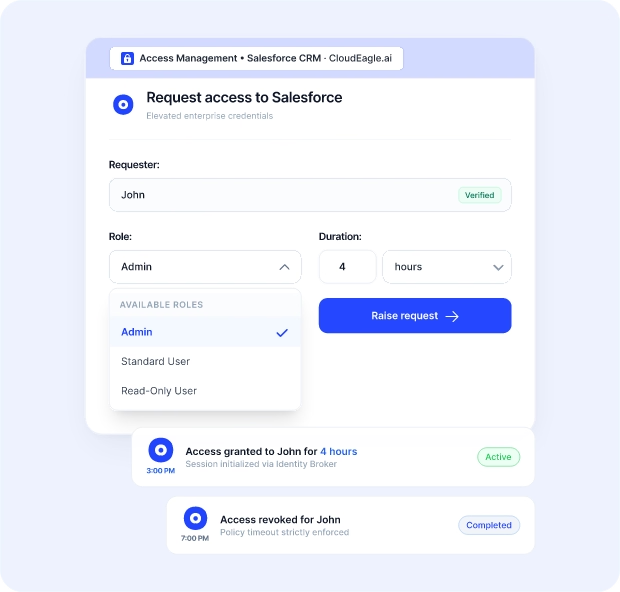
Cut access request tickets by 98%
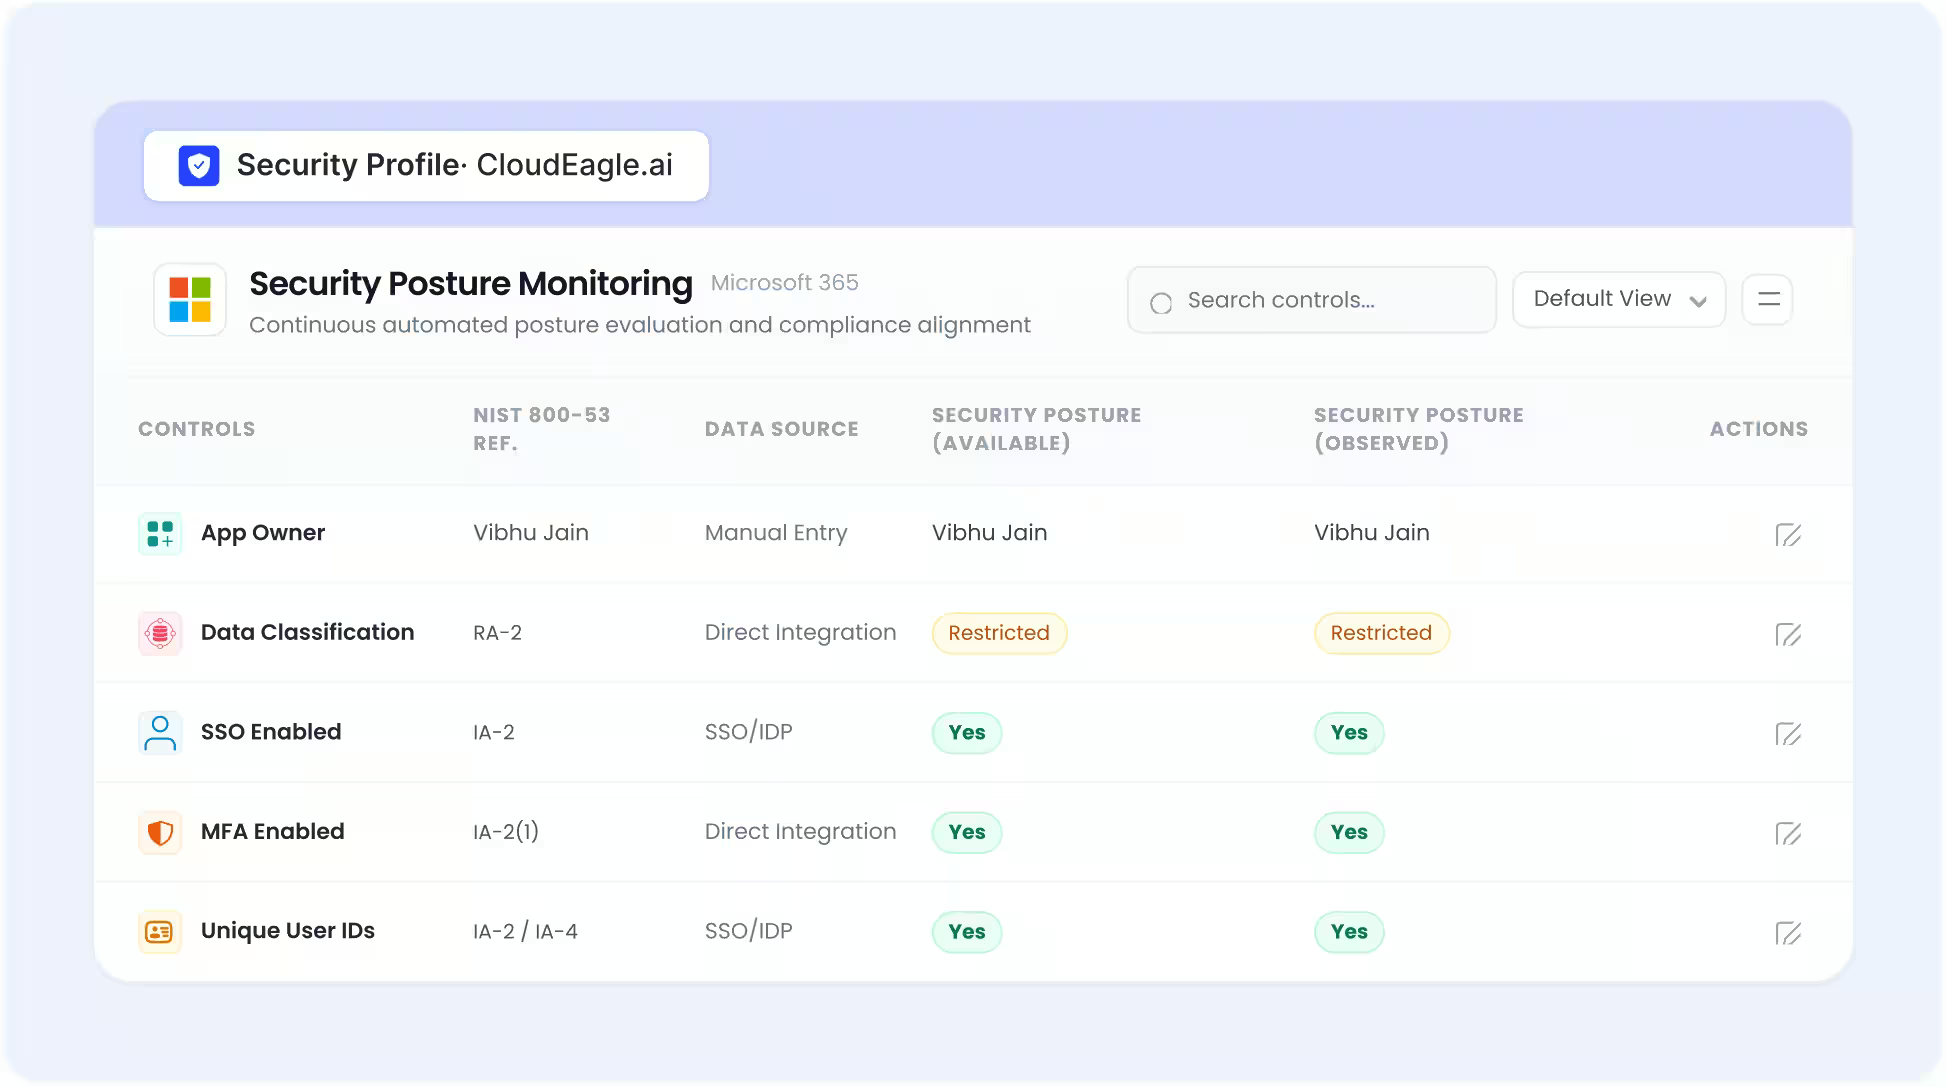
Continuously Monitor Your SaaS Security Posture
Ready to govern AI, SaaS and NHIs?
Frequently Asked Question
No. CloudEagle.ai works alongside your existing IDP. It extends governance to apps that sit outside Okta or AD, tools that don't support SCIM, apps bought on corporate cards, or AI tools employees signed up for on personal accounts. Your IDP stays in place; CloudEagle fills the gaps around it.
Through direct API provisioning. For apps that can't be connected to an IDP, CloudEagle uses the app's own API to provision and deprovision access. That means no more manually logging into 30 apps every time someone joins or leaves.
CloudEagle detects departures from your HRIS and automatically triggers deprovisioning across every connected app, whether or not it's behind Okta. That includes AI tools, non-SCIM apps, and any API tokens or service accounts tied to that employee. Freed licenses go back into the pool automatically.
Average onboarding is 30 minutes. Connect your SSO, finance system, and optionally a CASB or firewall source. Most teams see their complete app and AI inventory, including tools outside SSO, within the first session.
Yes. CloudEagle integrates bi-directionally with Jira, ServiceNow, Zendesk, and Asana. Your ticketing tool stays the source of truth. CloudEagle orchestrates workflows around it, triggering tickets, syncing status, and closing loops, without requiring your team to leave their existing systems.
Non-human identities are service accounts, API keys, bots, and AI agents, anything that accesses your systems without being a person. Every new integration or automation creates one. The problem is they accumulate without owners or review cycles, which means you can have dozens of bots with standing access that nobody's tracking. CloudEagle gives them the same lifecycle governance as human identities.
CASBs operate at the network layer and catch what passes through your traffic. They miss apps accessed on personal devices, free-tier AI tools signed up on personal email, and anything outside your network perimeter. CloudEagle adds app-layer visibility, identity governance, license management, and spend attribution, all the things a CASB doesn't cover.
CloudEagle pulls user roles, permissions, and access history from every connected app into a single dashboard. You schedule reviews, assign reviewers, and flag high-risk users automatically. When access is revoked, deprovisioning happens and the evidence is attached, no manual gathering from Jira or spreadsheets. Reviews that used to take months take days.
How IT teams run on CloudEagle.ai


