Maintain Audit-Ready SaaS Access Across Every Client Engagement
Audit and tax firms rely on SaaS tools to manage client data, collaborate across teams, and deliver regulatory outcomes. Centralized control ensures access is appropriate, temporary, and fully auditable, without adding manual audit prep work.





Growing SaaS Chaos Inside Audit and Tax Organizations
Rapid SaaS adoption without centralized control leads to overspending, audit risk, and operational inefficiencies.
Deliver Always-On SaaS Audit Readiness Across Client Workflows
Eliminate Overprivileged Access Across SaaS

- Identify and remediate over-privileged users before they create audit or compliance exposure
- Align access strictly to engagement roles, client assignments, and defined project timelines
- Continuously monitor admin roles to prevent privilege creep over time
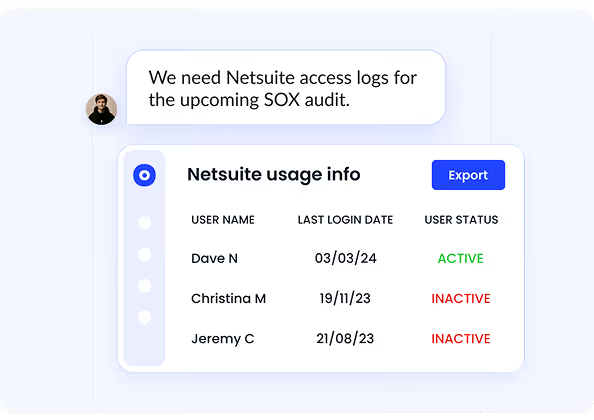
Eliminate Audit Scramble With Continuous Evidence
- Log every access request, approval, modification, and revocation with full context and timestamps
- Centralize evidence in one place, eliminating reliance on email threads, spreadsheets, or screenshots
- Reduce audit preparation time so teams can focus on risk assessment, not proof collection
Reduce Risk From Temporary and Contractor Access

- Identify which applications operate across NOC, engineering, and support teams
- Detect unapproved or redundant tools before they impact security or operations
- Clarify ownership and accountability across distributed telecom environments

Optimize Licenses Across Engagement-Based Work

- Unused licenses from completed engagements are surfaced quickly and clearly
- Licenses are reclaimed or reassigned without manual tracking or guesswork
- Software spend reflects active client work instead of historical assumptions
Frequently Asked Questions
Audit and tax firms handle sensitive client data and operate under strict regulatory scrutiny. Improper access creates compliance risk and erodes client trust.
Teams rotate frequently across engagements, but access is often granted once and never revisited, leading to excess permissions.
CloudEagle tracks access approvals, changes, and removals centrally, ensuring evidence is always available without manual preparation.
Reviews rely on scattered data and manual verification, causing reviewer fatigue and increasing the risk of rubber-stamping access.
CloudEagle highlights high-risk and privileged users first, helping reviewers focus on what matters most.
By using time-bound access that expires automatically, firms prevent lingering permissions after work is complete.
Licenses purchased for specific projects often remain assigned after engagements end, increasing unnecessary spend.
CloudEagle identifies unused licenses tied to completed engagements and enables reassignment or removal.
Auditors can review complete, consistent access records without delays, reducing findings and remediation cycles.
Clear access boundaries, continuous reviews, and strong audit trails demonstrate accountability and data protection.