Access control & compliance

SOX Compliance Cost: 2026 Guide to What You'll Pay

Share via:
Written by:
CloudEagle.ai Team
Reviewed by
Nidhi Jain
Last Updated:
October 3, 2025
blog-cms-banner-bg
Little-Known Negotiation Hacks to Get the Best Deal on Slack
cta-bg-blogDownload Your Copy

HIPAA Compliance Checklist for 2025

Download PDF

SOX compliance is critical for enterprises to ensure accurate financial reporting, prevent fraud, and maintain investor trust. When planning their budgets, enterprises must understand the costs involved, as SOX compliance costs vary between small businesses and large enterprises.

While smaller companies may spend close to $180K annually, large enterprises often allocate upward of $2 million per year to their SOX programs.

Proper budgeting for these costs helps enterprises manage risks effectively and maintain strong corporate governance. Let’s explore the details of these SOX compliance costs and why having a clear budget plan is vital for regulatory success.

‍

1. What Is SOX Compliance?

SOX compliance is the process of meeting the financial reporting, internal control, auditing, and data security requirements established by the Sarbanes-Oxley Act of 2002. 

The U.S. law was enacted to strengthen corporate accountability and protect investors from financial reporting fraud.

Key areas of SOX regulatory compliance include:

  • Internal controls: Establishing controls that protect the accuracy and integrity of financial reporting.
  • Financial reporting: Maintaining reliable processes for preparing and disclosing financial information.
  • Auditing and testing: Regularly testing controls and documenting their effectiveness.
  • Access and data security: Restricting access to financial systems and protecting sensitive financial information.
  • Remediation: Identifying control weaknesses and addressing them before they affect financial reporting.

SOX compliance therefore extends beyond financial audits. It requires organizations to continuously maintain, test, document, and improve the controls that support accurate financial reporting.

‍

Compliance Doesn't Fail Overnight

Small gaps add up.
See The Best Practices

‍

2. What Are The Four Controls of SOX?

The four main controls of SOX compliance generally refer to key internal control areas that enterprises focus on to ensure accurate financial reporting and compliance with the Sarbanes-Oxley Act. 

These controls include:

  • Access Controls: Ensuring that only authorized personnel have access to critical financial systems and data to prevent unauthorized changes or fraud.
  • Change Management Controls: Managing and documenting changes to financial systems and processes to ensure integrity and prevent unauthorized modifications.
  • Segregation of Duties (SoD): Dividing responsibilities among employees so that no single person has control over all aspects of financial transactions, reducing fraud risk.
  • Cybersecurity Controls: Implementing technical and procedural safeguards to protect financial data and systems from cyber threats.

These controls align with SOX rules, especially Section 404, which requires companies to check and report on how effective their financial controls are. Together, they help prevent errors and fraud while ensuring transparency in financial reporting.

‍

3. Typical SOX Compliance Cost Breakdown

Understanding how SOX compliance costs are allocated can help enterprises budget more effectively. Here’s a breakdown of the major cost components involved:

A. Internal Audit and Staffing Costs

A significant portion of SOX costs goes toward internal audit teams who perform control testing, documentation, and remediation. Staffing costs include salaries for audit professionals and control owners responsible for maintaining compliance, often accounting for nearly half of total SOX compliance costs.

B. Technology and Software Costs

Investing in audit management software, automation tools, and compliance platforms is essential to streamline SOX workflows. These technology expenses can be substantial, but they often reduce manual effort and long-term costs associated with maintaining compliance documentation and reporting.

C. External Auditor and Legal Fees

Many companies rely on third-party auditors and legal counsel to validate compliance and assist with regulatory interpretations. Fees paid to these external parties often constitute the largest external expense and represent a critical element of SOX compliance costs.

D. Remediation and Control Improvements

When issues or gaps are identified during audits, companies must invest in remediation efforts. This includes updating processes, enhancing controls, and implementing corrective measures to meet SOX compliance requirements.

E. Long-Term Maintenance and Monitoring

SOX compliance is an ongoing process. Costs related to continuous monitoring, periodic re-testing of controls, updates due to regulatory changes, and training updates ensure sustained compliance and contribute to the overall cost of SOX compliance.

‍

Every New App Brings New Compliance Risk

Stay ahead of it.
Stay Compliant

‍

4. What Factors Influence SOX Compliance Costs?

Several factors contribute to the cost of SOX compliance, affecting how much enterprises need to budget for regulatory adherence:

A. Company Size and Operational Complexity

Larger organizations with complex business models, multiple subsidiaries, or international operations face higher SOX compliance costs. The need to document and monitor a wide array of processes and controls increases resource requirements.

B. Internal Audit and Control Testing Efforts

The extent of internal audit activities and controls testing significantly impacts costs. Companies dedicate thousands of hours annually to test and document controls, with many hours spent on administrative tasks like spreadsheet reconciliation, which adds to the overall SOX compliance costs.

C. Use of External Auditors and Consultants

Engaging external auditors for independent assessments and consultants for advisory services incurs substantial fees. These professionals ensure companies meet SOX compliance requirements, but can increase the total budget considerably.

D. Technology, Tools, and Automation Investments

Many companies invest in audit management platforms, robotic process automation, and analytics tools to streamline compliance processes. While these require upfront costs, technology can reduce manual workloads and cut long-term SOX compliance costs.

E. Training Employees on SOX Requirements

Providing comprehensive training ensures employees understand their roles in maintaining compliance. Regular training programs, including updates on evolving regulations, contribute to budgeting for SOX compliance.

F. Ongoing Monitoring and Reporting Needs

Continuous monitoring and periodic reporting of controls are required to maintain compliance. These ongoing activities demand consistent allocation of time and resources, further influencing the total SOX compliance costs.

‍

5. How to Reduce SOX Compliance Costs Without Risking Security

Reducing the cost of SOX compliance is essential for companies aiming to optimize budgets while maintaining robust security and regulatory adherence. Here are effective strategies to lower SOX compliance costs without compromising compliance quality:

1. Automating Compliance Monitoring and Reporting

Implementing automation technologies for compliance monitoring helps reduce manual efforts and errors. Automation tools can continuously track control performance, generate audit-ready reports, and flag anomalies faster than manual processes, significantly lowering SOX compliance costs and improving accuracy.

2. Leveraging Centralized Identity and Access Controls

Strong identity and access management are a cornerstone of SOX compliance. Centralizing these controls not only enhances security by reducing the risk of unauthorized access but also simplifies the audit process. This consolidation cuts down remediation efforts and decreases SOX compliance costs related to access reviews and compliance documentation.

3. Streamlining Internal Audit Processes

Optimizing internal audit workflows through risk-based prioritization and adopting efficient audit management platforms helps companies focus their resources on high-impact controls. This reduces time and expense in testing less critical areas while ensuring adherence to SOX compliance requirements.

4. Partnering With the Right Compliance Tools

Choosing software platforms built specifically for SOX compliance can automate tedious tasks such as documentation, control testing, and reporting. These tools enhance productivity, enable collaboration, and reduce errors, leading to lower overall SOX compliance costs.

5. Prioritizing High-Risk Areas for Efficiency

Focusing compliance efforts on high-risk controls and processes ensures resources are optimally allocated. This risk-based approach ensures compliance activities mitigate the greatest financial reporting risks while avoiding unnecessary spending on low-risk areas, cutting down SOX compliance costs without risking security.

By strategically adopting these approaches, companies can achieve a cost-effective SOX compliance program that maintains regulatory rigor and strengthens security.

‍

6. Hidden Costs Enterprises Often Overlook

While the direct SOX compliance costs, such as audit fees and technology investment,s are relatively straightforward, many enterprises underestimate several hidden costs that can significantly impact their compliance budgets.

1. Employee Downtime During SOX Audits

During SOX audits, key employees spend substantial time away from their usual duties to assist with control testing, documentation, and answering auditor queries. This downtime leads to productivity loss, which is an indirect but important component of SOX compliance costs.

2. Shadow IT and Poor Documentation Risks

Untracked or unauthorized software (Shadow IT) and incomplete documentation can cause compliance gaps. Remediating these risks late in the process results in unexpected expenses, increasing overall SOX compliance costs, and complicating audit readiness.

Know how Rec Room gets complete visibility on free apps used by its teams.

3. Cost of Non-Compliance Penalties and Fines

Companies that fail to comply with SOX risk hefty fines and legal penalties. These costs also extend to potential lawsuits and settlement fees, making non-compliance far more expensive than the costs of maintaining compliance.

4. Reputational Damage and Customer Trust Issues

Beyond financial penalties, SOX violations can erode investor confidence and damage a company’s reputation. Loss of customer trust may lead to reduced business opportunities and stock price declines, adding a significant long-term cost that organizations must consider.

‍

7. How CloudEagle.ai Can Lower SOX Compliance Costs

Here’s how CloudEagle.ai helps you with enterprise governance:

A. Shadow AI Discovery: Surface Every Tool Before You Govern It

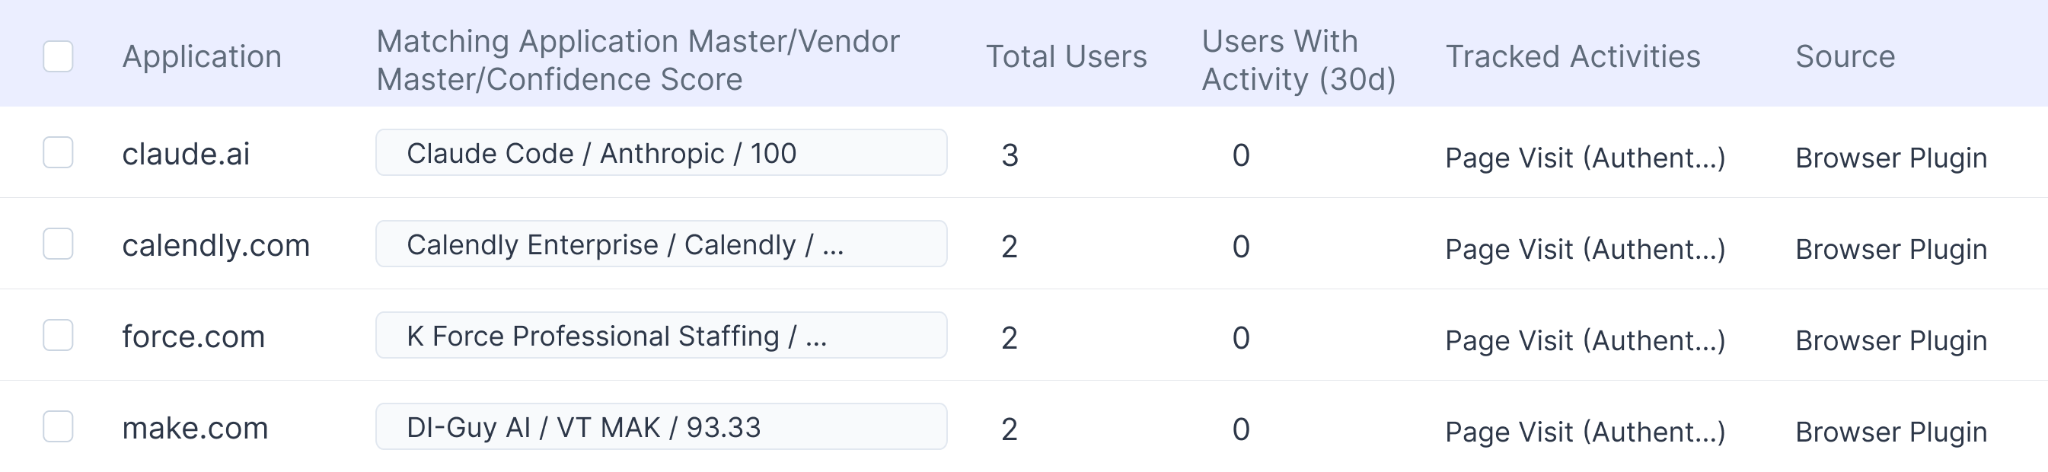
CloudEagle.ai detects Shadow AI through browser extensions, firewall logs, Zscaler, CrowdStrike, and finance signals simultaneously, building a single source of truth across every AI tool in use, sanctioned or not.

Here's how multi-signal Shadow AI discovery is designed to work:
‍

‍

In CloudEagle.ai's AI application inventory, every tool appears with adoption by team and department. 

‍

‍

It surfaces whether it was sanctioned or discovered through external signals, and whether it carries GenAI capabilities that were never part of the original procurement decision.

B. Secure Browser and Flash Page: Redirect Before Data Enters an Unapproved Session

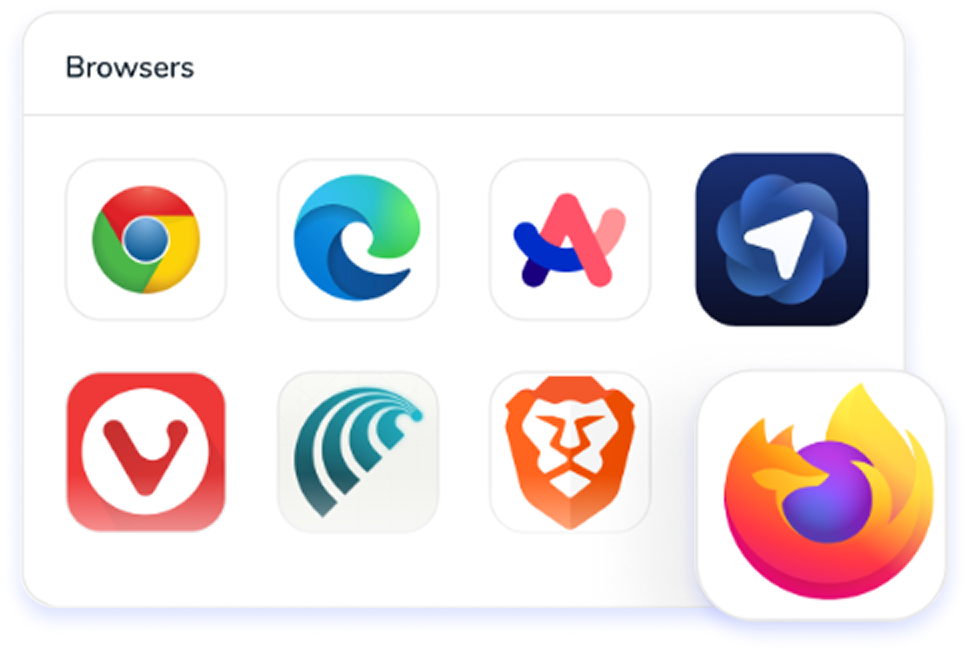
CloudEagle.ai's browser plugin catches what CASB, DLP, and LLM gateways all miss, the moment an employee opens an unapproved AI tool in a browser tab. Here’s how the browser plugin works:
‍

‍

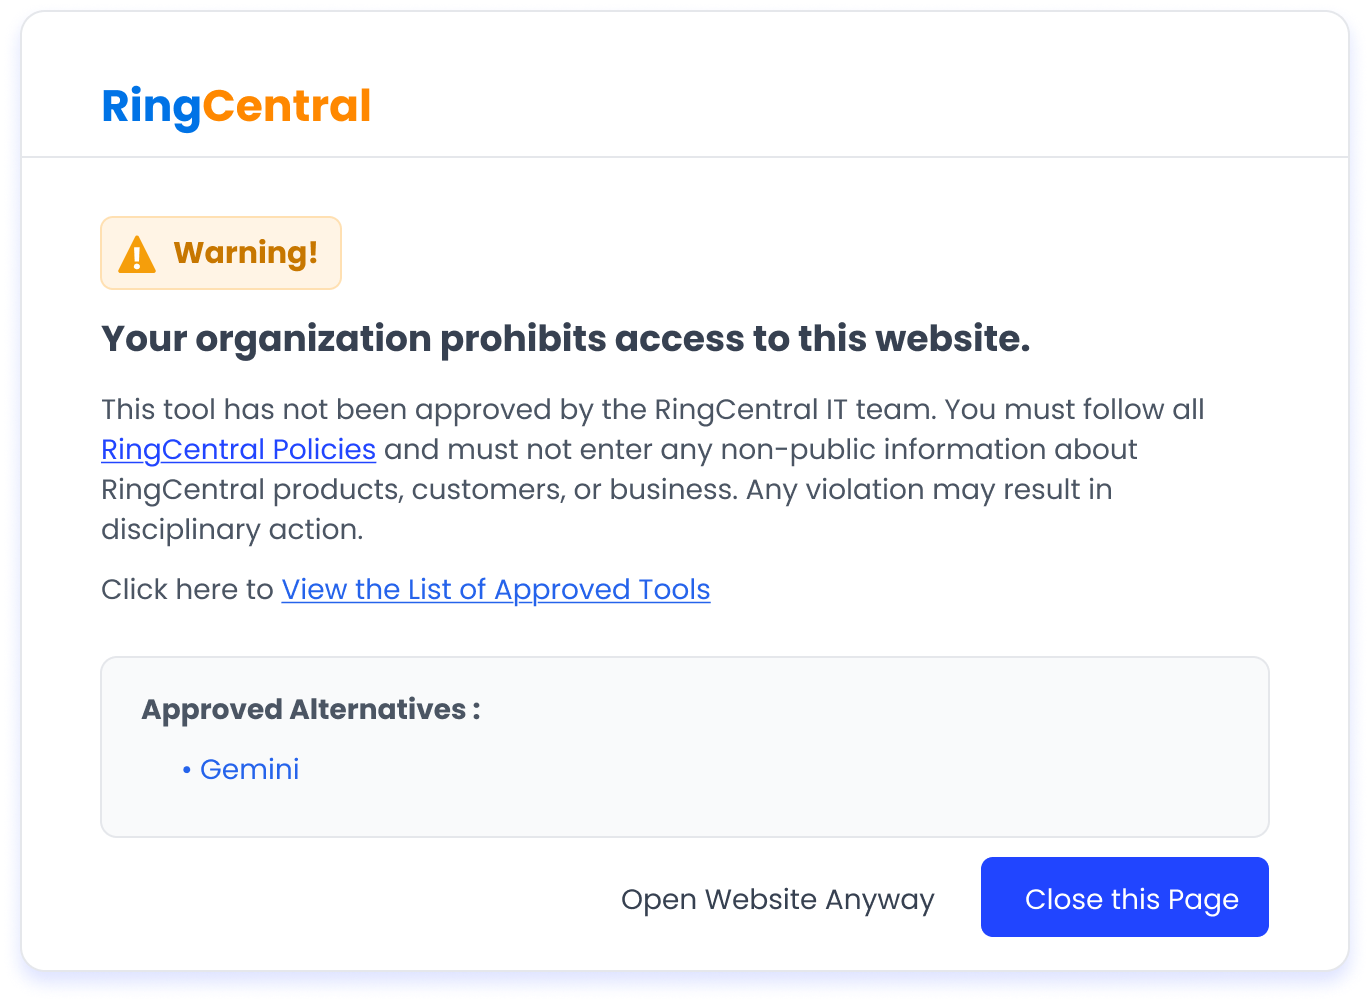
When that happens, a real-time flash page steps in before any company data is entered, redirecting the employee to the approved alternative automatically.
‍

‍

In CloudEagle.ai's Secure Browser policy view, flash page rules are configurable by team, department, and tool so Engineering can be permitted Cursor while redirected away from consumer ChatGPT.

‍

‍

Every redirect is logged automatically, tool accessed, sanctioned status, flash page triggered, and timestamp. The audit record exists in real time without additional effort.

C. Data Loss Prevention: Block Sensitive Data Before It Reaches the Model

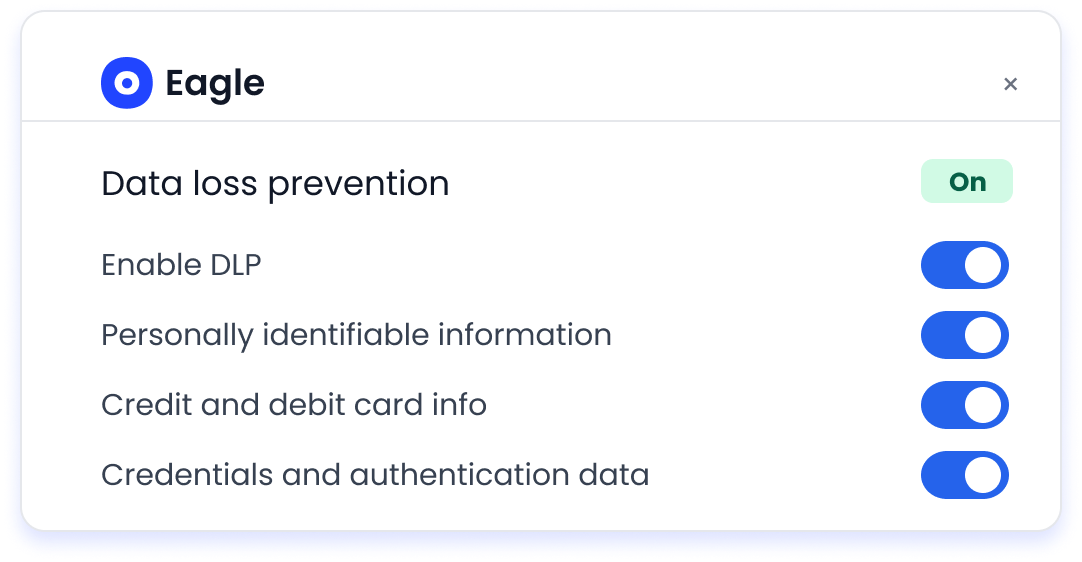
CloudEagle.ai’s DLP operates at the prompt entry layer, catching what is typed into an AI interface before it is submitted to the model. 

When an employee attempts to paste sensitive content like PII, PHI, financial data, proprietary code, into an AI tool, CloudEagle.ai fires before the content leaves the browser.
‍

‍

In CloudEagle.ai's DLP policy view, sensitive content categories are configurable. Credit card numbers, PHI, source code, and proprietary data each carry their own enforcement rules.

D. GenAI Risk Scoring: Prioritize the Riskiest Apps First

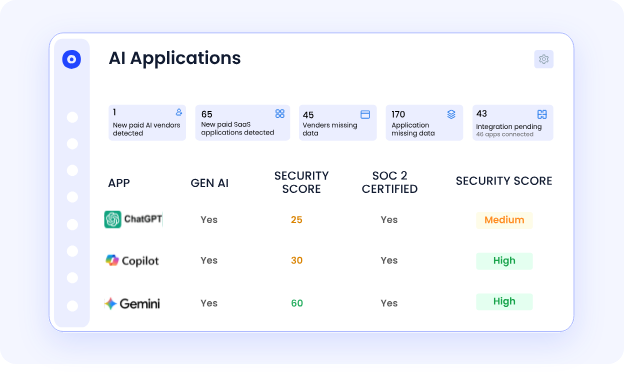
CloudEagle.ai automatically assigns a GenAI risk score to every AI tool and feature in the environment, powered by Netskope's Cloud Confidence Index.
‍

‍

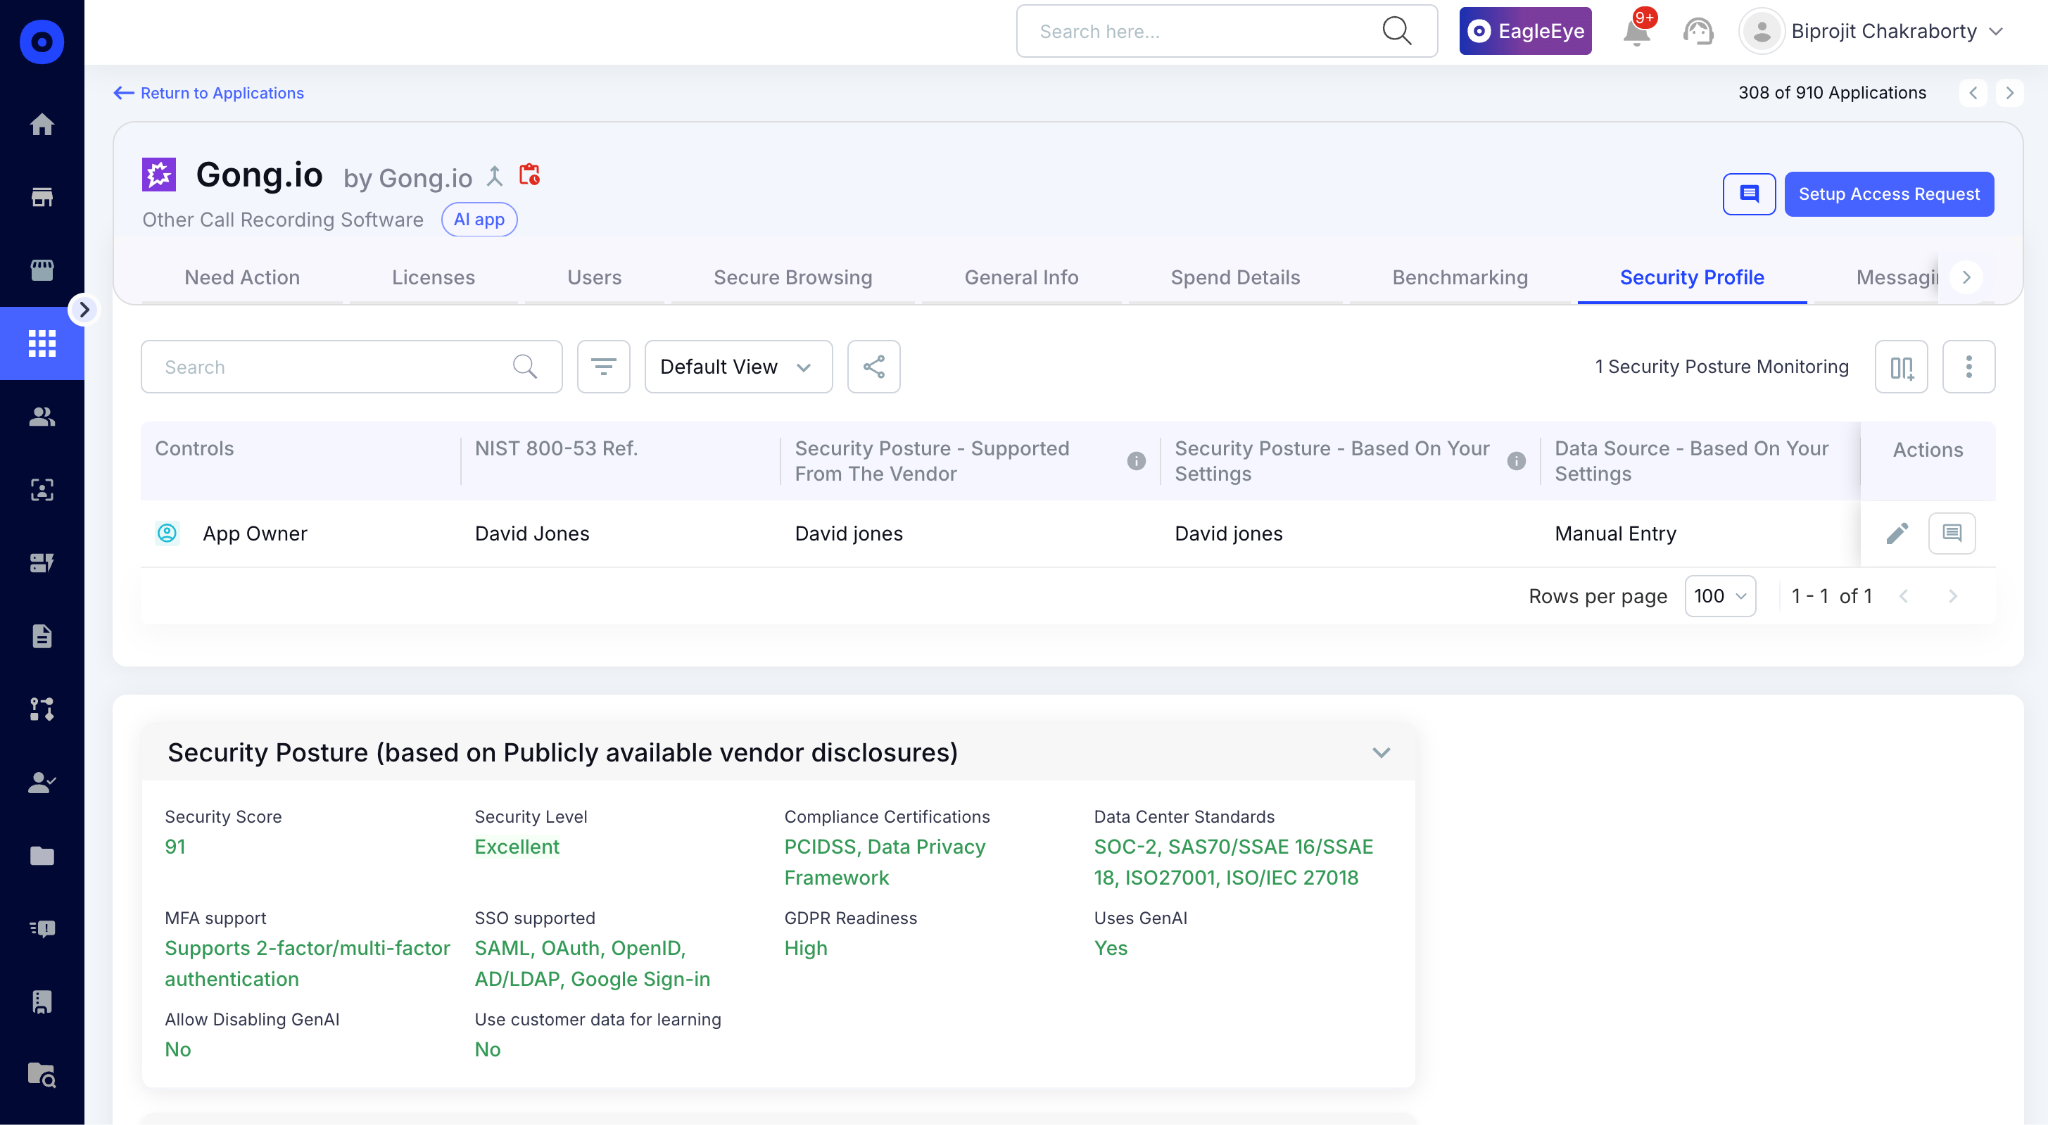
Every tool is scored on data residency, training data use, security posture, and compliance alignment, so security teams have a prioritized remediation list, not a flat inventory of 200 tools with no indication of where to start.
‍

‍

In CloudEagle.ai's risk scoring view, every AI vendor appears with its risk level, whether it trains on company data, and whether it processes regulated data without a formal agreement in place.

E. AI Usage and Token Consumption Tracking: See Who Is Using What and at What Scale

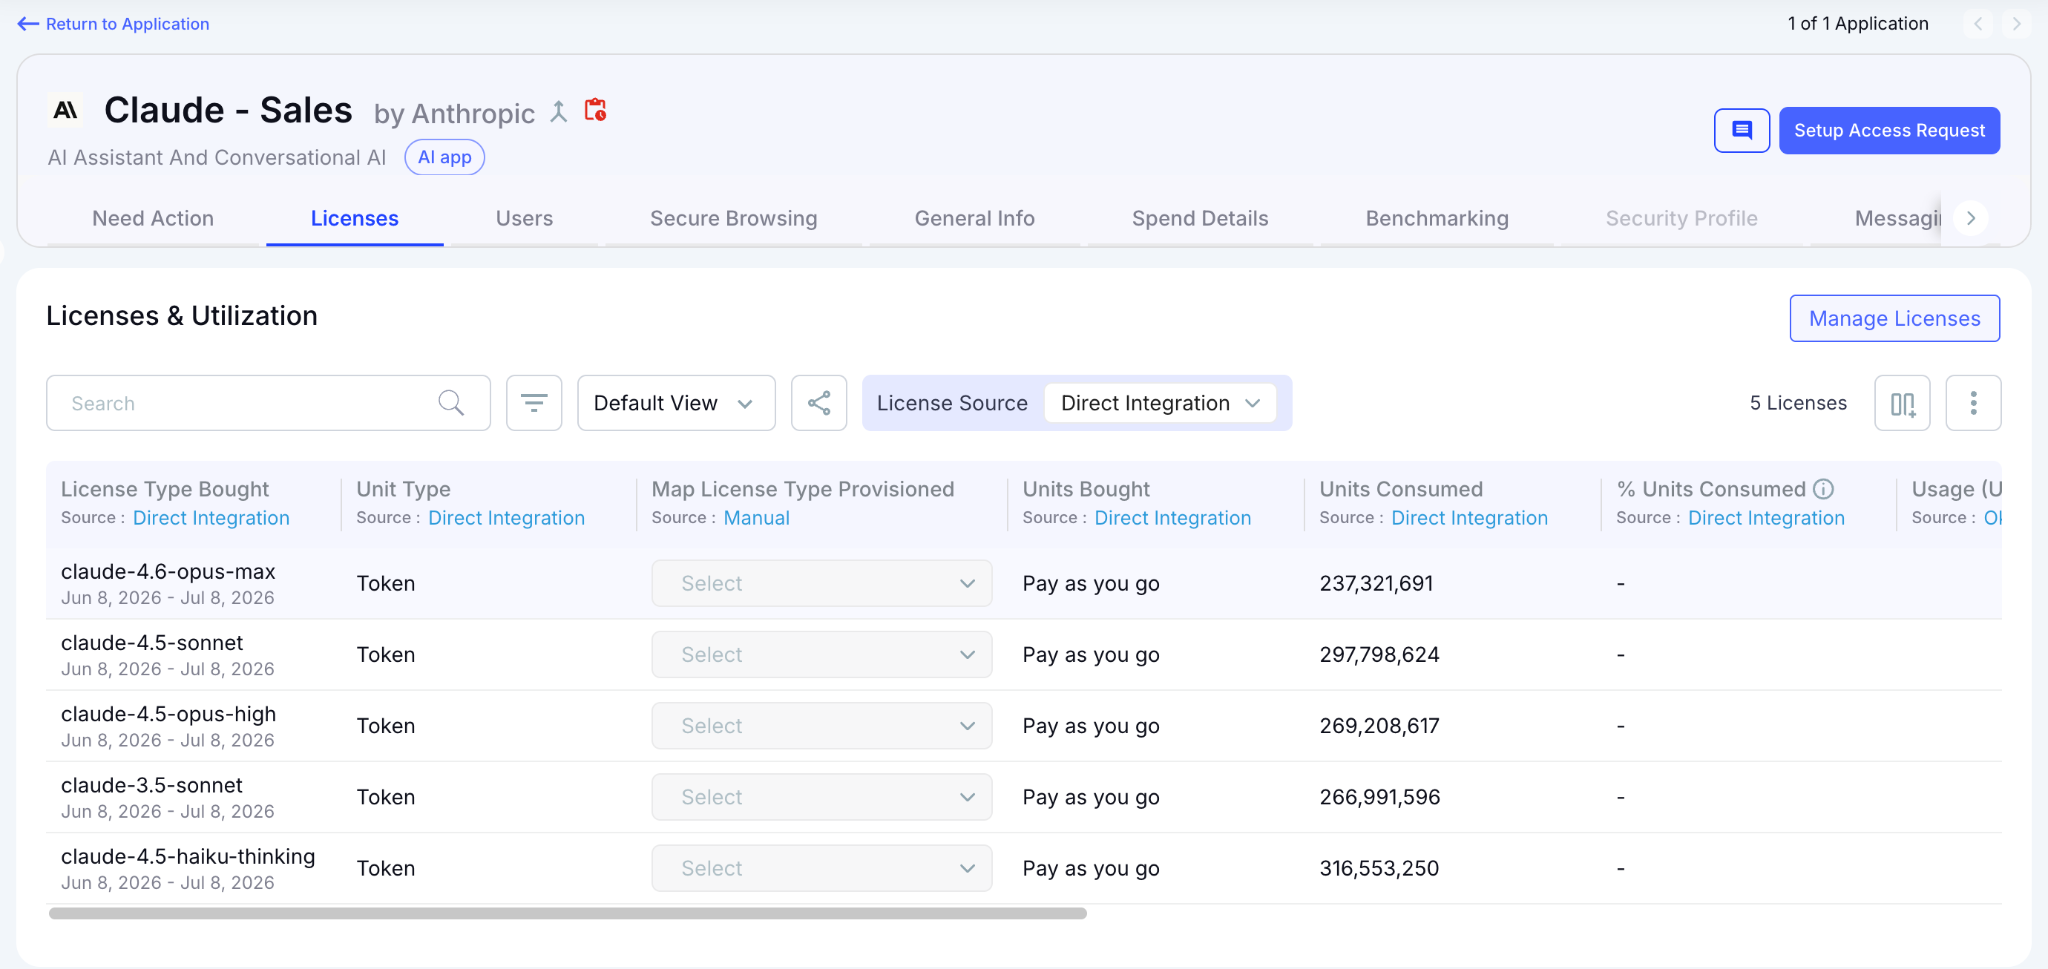
CloudEagle.ai tracks token consumption and API spend for Claude, ChatGPT, Cursor, Gemini, and GitHub Copilot, on per user, per team, per department basis.

This matters for blast radius because unusual token consumption is often the first behavioral signal that something is wrong. Here's how per-user AI usage tracking is designed:

‍

‍

In CloudEagle.ai's AI usage dashboard, every user's consumption is visible by model tier and time period. 
‍

‍

Security teams identify anomalies and Finance gets the chargeback data needed to enforce budget accountability.

F. User Access Reviews: Review Risky Access Without the Manual Work

CloudEagle.ai centralizes user access reviews, giving security teams visibility into roles, permissions, SSO/HRIS presence, and elevated privileges in one place.

Here’s how CloudEagle.ai’s access review process works:

‍

Reviewers can focus on high-risk users and ex-employees instead of manually checking access across individual applications. CloudEagle.ai also flags managers with incomplete reviews, reducing the risk of rubber-stamped approvals.

‍

Reviews can be scheduled and assigned automatically. When access is rejected, CloudEagle.ai initiates deprovisioning and attaches proof of removal, eliminating manual evidence collection from JIRA and other systems.

The result is a complete trail from review → remediation → evidence → audit report, helping teams complete access reviews in days instead of months

G. SaaS Security Posture Management

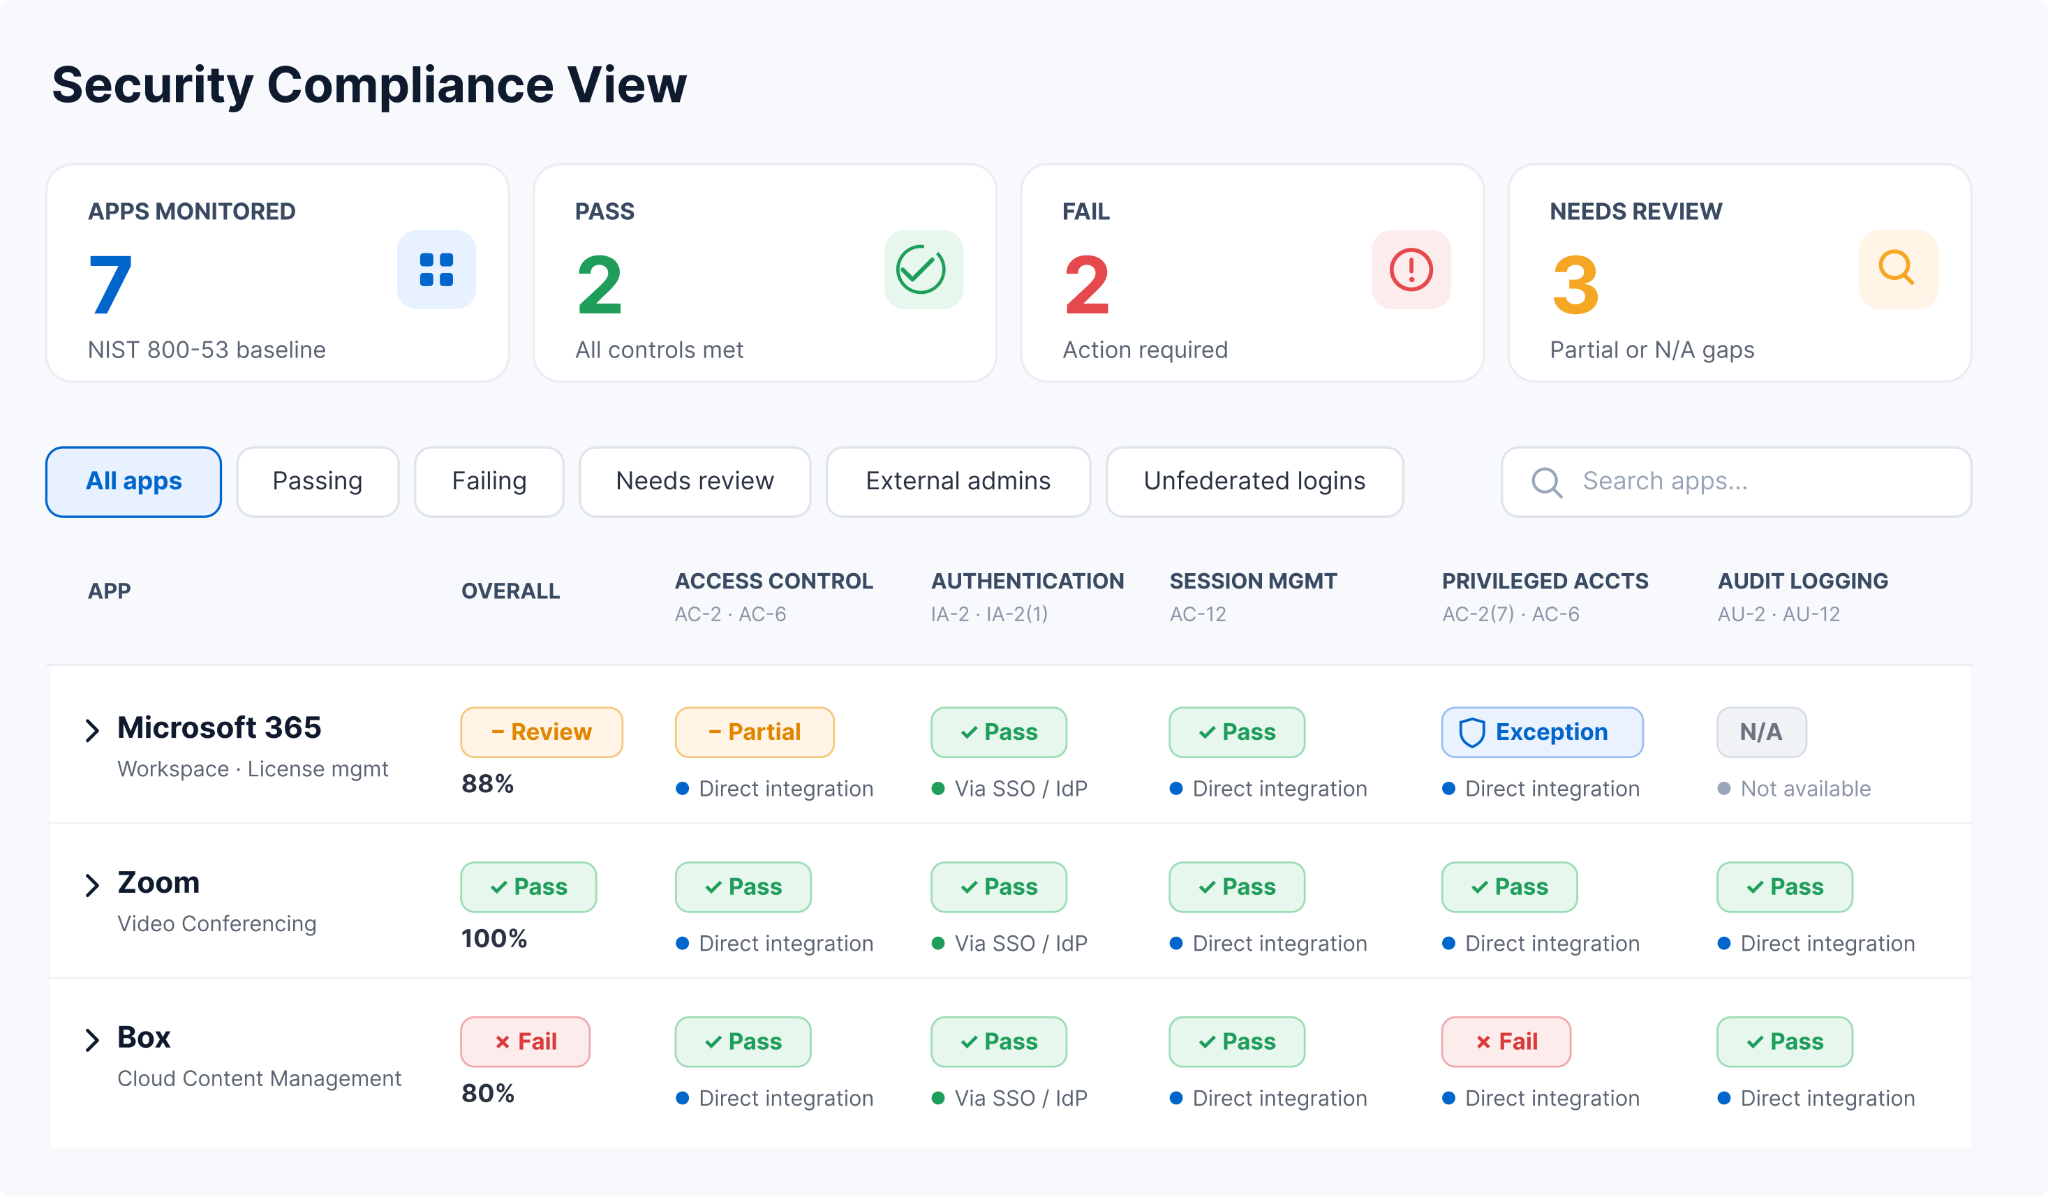
CloudEagle.ai gives security teams a continuously updated view of application-level security posture across the SaaS stack, replacing manual app-by-app checks for controls such as MFA, SSO, and NIST 800 compliance.

Here’s how CloudEagle.ai consolidates security posture:
‍

‍

CloudEagle.ai pulls federation signals such as MFA and SSO directly from Okta and Entra, retrieves compliance data through APIs where available, and supplements it with Netskope’s Cloud Confidence Index.

These signals are rolled into a single pass/fail view for each application. Teams can also manually add information that cannot be pulled automatically, such as application ownership.

This gives security teams one continuously updated view of SaaS security posture instead of relying on scattered checks and stale compliance spreadsheets.‍

‍

‍

8. Conclusion

SOX compliance can be costly and complex, but the right tools help cut costs and keep SaaS security strong. CloudEagle.ai simplifies compliance with automation, smart access controls, and centralized SaaS governance.

Features like automated onboarding/offboarding, role-based and just-in-time access, and continuous access reviews reduce manual work and hidden expenses. The Self-Service App Catalog enables employees, limits shadow IT, and optimizes SaaS spend.

Ready to take control of your SOX compliance and reduce costs without compromising security? 

Schedule a demo to see how automation and centralized SaaS management can transform your SOX compliance program.

‍

9. FAQs

1. Doesn't SOX audit prep pull key employees away from their jobs for weeks?

CloudEagle.ai cuts that downtime by putting access control, compliance reporting, and risk monitoring in one dashboard. It connects to HR systems, SSO, and over 500 SaaS applications, so audit evidence is ready without pulling people off their work to reconcile spreadsheets.

2. Aren't user access reviews one of the most expensive parts of SOX compliance?

CloudEagle.ai automates SOX access reviews to cut that cost. It continuously monitors who has access to what, sends reminders to reviewers, and runs auto-revocation workflows for stale or unused access. Dezerv used CloudEagle.ai to automate its app access review process.

3. Can't a former employee's leftover access turn into a costly SOX finding?

With CloudEagle.ai, a departing employee's access is revoked immediately. Offboarding runs automatically on predefined rules tied to role, department, and location, which removes the manual errors that lead to audit findings and expensive remediation.

4. Doesn't shadow IT create compliance gaps that are expensive to fix late?

CloudEagle.ai finds shadow IT early. It identifies unauthorized SaaS apps through identity systems, finance platforms, and credit card transaction analysis, then steers employees to a vetted catalog of approved apps. Gaps are closed before the audit instead of during it.

5. Isn't granting temporary access to financial systems a SOX risk?

CloudEagle.ai makes temporary access safe with Just-In-Time access. Permissions are granted only when needed and revoked automatically once the task is done, and every grant is recorded in audit-ready access logs. This supports SOX's least-privilege expectations without slowing work down.

‍

Advertisement for a SaaS Subscription Tracking Template with a call-to-action button to download and a partial graphic of a tablet showing charts.Banner promoting a SaaS Agreement Checklist to streamline SaaS management and avoid budget waste with a call-to-action button labeled Download checklist.Blue banner with text 'The Ultimate Employee Offboarding Checklist!' and a black button labeled 'Download checklist' alongside partial views of checklist documents from cloudeagle.ai.Digital ad for download checklist titled 'The Ultimate Checklist for IT Leaders to Optimize SaaS Operations' by cloudeagle.ai, showing checklist pages.Slack Buyer's Guide offer with text 'Unlock insider insights to get the best deal on Slack!' and a button labeled 'Get Your Copy', accompanied by a preview of the guide featuring Slack's logo.Monday Pricing Guide by cloudeagle.ai offering exclusive pricing secrets to maximize investment with a call-to-action button labeled Get Your Copy and an image of the guide's cover.Blue banner for Canva Pricing Guide by cloudeagle.ai offering a guide to Canva costs, features, and alternatives with a call-to-action button saying Get Your Copy.Blue banner with white text reading 'Little-Known Negotiation Hacks to Get the Best Deal on Slack' and a white button labeled 'Get Your Copy'.Blue banner with text 'Little-Known Negotiation Hacks to Get the Best Deal on Monday.com' and a white button labeled 'Get Your Copy'.Blue banner with text 'Little-Known Negotiation Hacks to Get the Best Deal on Canva' and a white button labeled 'Get Your Copy'.Banner with text 'Slack Buyer's Guide' and a 'Download Now' button next to images of a guide titled 'Slack Buyer’s Guide: Features, Pricing & Best Practices'.Digital cover of Monday Pricing Guide with a button labeled Get Your Copy on a blue background.Canva Pricing Guide cover with a button labeled Get Your Copy on a blue gradient background.

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.
License Count
Benchmark
Per User/Per Year

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.
License Count
Benchmark
Per User/Per Year

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.
Notion Plus
License Count
Benchmark
Per User/Per Year
100-500
$67.20 - $78.72
500-1000
$59.52 - $72.00
1000+
$51.84 - $57.60
Canva Pro
License Count
Benchmark
Per User/Per Year
100-500
$74.33-$88.71
500-1000
$64.74-$80.32
1000+
$55.14-$62.34

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.
Zoom Business
License Count
Benchmark
Per User/Per Year
100-500
$216.00 - $264.00
500-1000
$180.00 - $216.00
1000+
$156.00 - $180.00

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.

Get the Right Security Platform To Secure Your Cloud Infrastructure

Please enter a business email
Thank you!
The 2023 SaaS report has been sent to your email. Check your promotional or spam folder.
Oops! Something went wrong while submitting the form.

Access full report

Please enter a business email
Thank you!
The 2023 SaaS report has been sent to your email. Check your promotional or spam folder.
Oops! Something went wrong while submitting the form.
  • SOX compliance ensures companies maintain strong internal controls to prevent financial fraud and protect investors.
  • Costs of SOX compliance vary widely, from about $180K annually for small firms to over $2 million for large enterprises.
  • Major SOX cost drivers include internal audits, external auditor fees, technology investments, employee training, and ongoing monitoring.
  • Automating compliance processes and adopting risk-based approaches can significantly reduce SOX compliance expenses.
  • Non-compliance risks include heavy fines, legal penalties, reputational damage, and loss of investor confidence, making compliance investments worthwhile.

SOX compliance is critical for enterprises to ensure accurate financial reporting, prevent fraud, and maintain investor trust. When planning their budgets, enterprises must understand the costs involved, as SOX compliance costs vary between small businesses and large enterprises.

While smaller companies may spend close to $180K annually, large enterprises often allocate upward of $2 million per year to their SOX programs.

Proper budgeting for these costs helps enterprises manage risks effectively and maintain strong corporate governance. Let’s explore the details of these SOX compliance costs and why having a clear budget plan is vital for regulatory success.

‍

1. What Is SOX Compliance?

SOX compliance is the process of meeting the financial reporting, internal control, auditing, and data security requirements established by the Sarbanes-Oxley Act of 2002. 

The U.S. law was enacted to strengthen corporate accountability and protect investors from financial reporting fraud.

Key areas of SOX regulatory compliance include:

  • Internal controls: Establishing controls that protect the accuracy and integrity of financial reporting.
  • Financial reporting: Maintaining reliable processes for preparing and disclosing financial information.
  • Auditing and testing: Regularly testing controls and documenting their effectiveness.
  • Access and data security: Restricting access to financial systems and protecting sensitive financial information.
  • Remediation: Identifying control weaknesses and addressing them before they affect financial reporting.

SOX compliance therefore extends beyond financial audits. It requires organizations to continuously maintain, test, document, and improve the controls that support accurate financial reporting.

‍

Compliance Doesn't Fail Overnight

Small gaps add up.
See The Best Practices

‍

2. What Are The Four Controls of SOX?

The four main controls of SOX compliance generally refer to key internal control areas that enterprises focus on to ensure accurate financial reporting and compliance with the Sarbanes-Oxley Act. 

These controls include:

  • Access Controls: Ensuring that only authorized personnel have access to critical financial systems and data to prevent unauthorized changes or fraud.
  • Change Management Controls: Managing and documenting changes to financial systems and processes to ensure integrity and prevent unauthorized modifications.
  • Segregation of Duties (SoD): Dividing responsibilities among employees so that no single person has control over all aspects of financial transactions, reducing fraud risk.
  • Cybersecurity Controls: Implementing technical and procedural safeguards to protect financial data and systems from cyber threats.

These controls align with SOX rules, especially Section 404, which requires companies to check and report on how effective their financial controls are. Together, they help prevent errors and fraud while ensuring transparency in financial reporting.

‍

3. Typical SOX Compliance Cost Breakdown

Understanding how SOX compliance costs are allocated can help enterprises budget more effectively. Here’s a breakdown of the major cost components involved:

A. Internal Audit and Staffing Costs

A significant portion of SOX costs goes toward internal audit teams who perform control testing, documentation, and remediation. Staffing costs include salaries for audit professionals and control owners responsible for maintaining compliance, often accounting for nearly half of total SOX compliance costs.

B. Technology and Software Costs

Investing in audit management software, automation tools, and compliance platforms is essential to streamline SOX workflows. These technology expenses can be substantial, but they often reduce manual effort and long-term costs associated with maintaining compliance documentation and reporting.

C. External Auditor and Legal Fees

Many companies rely on third-party auditors and legal counsel to validate compliance and assist with regulatory interpretations. Fees paid to these external parties often constitute the largest external expense and represent a critical element of SOX compliance costs.

D. Remediation and Control Improvements

When issues or gaps are identified during audits, companies must invest in remediation efforts. This includes updating processes, enhancing controls, and implementing corrective measures to meet SOX compliance requirements.

E. Long-Term Maintenance and Monitoring

SOX compliance is an ongoing process. Costs related to continuous monitoring, periodic re-testing of controls, updates due to regulatory changes, and training updates ensure sustained compliance and contribute to the overall cost of SOX compliance.

‍

Every New App Brings New Compliance Risk

Stay ahead of it.
Stay Compliant

‍

4. What Factors Influence SOX Compliance Costs?

Several factors contribute to the cost of SOX compliance, affecting how much enterprises need to budget for regulatory adherence:

A. Company Size and Operational Complexity

Larger organizations with complex business models, multiple subsidiaries, or international operations face higher SOX compliance costs. The need to document and monitor a wide array of processes and controls increases resource requirements.

B. Internal Audit and Control Testing Efforts

The extent of internal audit activities and controls testing significantly impacts costs. Companies dedicate thousands of hours annually to test and document controls, with many hours spent on administrative tasks like spreadsheet reconciliation, which adds to the overall SOX compliance costs.

C. Use of External Auditors and Consultants

Engaging external auditors for independent assessments and consultants for advisory services incurs substantial fees. These professionals ensure companies meet SOX compliance requirements, but can increase the total budget considerably.

D. Technology, Tools, and Automation Investments

Many companies invest in audit management platforms, robotic process automation, and analytics tools to streamline compliance processes. While these require upfront costs, technology can reduce manual workloads and cut long-term SOX compliance costs.

E. Training Employees on SOX Requirements

Providing comprehensive training ensures employees understand their roles in maintaining compliance. Regular training programs, including updates on evolving regulations, contribute to budgeting for SOX compliance.

F. Ongoing Monitoring and Reporting Needs

Continuous monitoring and periodic reporting of controls are required to maintain compliance. These ongoing activities demand consistent allocation of time and resources, further influencing the total SOX compliance costs.

‍

5. How to Reduce SOX Compliance Costs Without Risking Security

Reducing the cost of SOX compliance is essential for companies aiming to optimize budgets while maintaining robust security and regulatory adherence. Here are effective strategies to lower SOX compliance costs without compromising compliance quality:

1. Automating Compliance Monitoring and Reporting

Implementing automation technologies for compliance monitoring helps reduce manual efforts and errors. Automation tools can continuously track control performance, generate audit-ready reports, and flag anomalies faster than manual processes, significantly lowering SOX compliance costs and improving accuracy.

2. Leveraging Centralized Identity and Access Controls

Strong identity and access management are a cornerstone of SOX compliance. Centralizing these controls not only enhances security by reducing the risk of unauthorized access but also simplifies the audit process. This consolidation cuts down remediation efforts and decreases SOX compliance costs related to access reviews and compliance documentation.

3. Streamlining Internal Audit Processes

Optimizing internal audit workflows through risk-based prioritization and adopting efficient audit management platforms helps companies focus their resources on high-impact controls. This reduces time and expense in testing less critical areas while ensuring adherence to SOX compliance requirements.

4. Partnering With the Right Compliance Tools

Choosing software platforms built specifically for SOX compliance can automate tedious tasks such as documentation, control testing, and reporting. These tools enhance productivity, enable collaboration, and reduce errors, leading to lower overall SOX compliance costs.

5. Prioritizing High-Risk Areas for Efficiency

Focusing compliance efforts on high-risk controls and processes ensures resources are optimally allocated. This risk-based approach ensures compliance activities mitigate the greatest financial reporting risks while avoiding unnecessary spending on low-risk areas, cutting down SOX compliance costs without risking security.

By strategically adopting these approaches, companies can achieve a cost-effective SOX compliance program that maintains regulatory rigor and strengthens security.

‍

6. Hidden Costs Enterprises Often Overlook

While the direct SOX compliance costs, such as audit fees and technology investment,s are relatively straightforward, many enterprises underestimate several hidden costs that can significantly impact their compliance budgets.

1. Employee Downtime During SOX Audits

During SOX audits, key employees spend substantial time away from their usual duties to assist with control testing, documentation, and answering auditor queries. This downtime leads to productivity loss, which is an indirect but important component of SOX compliance costs.

2. Shadow IT and Poor Documentation Risks

Untracked or unauthorized software (Shadow IT) and incomplete documentation can cause compliance gaps. Remediating these risks late in the process results in unexpected expenses, increasing overall SOX compliance costs, and complicating audit readiness.

Know how Rec Room gets complete visibility on free apps used by its teams.

3. Cost of Non-Compliance Penalties and Fines

Companies that fail to comply with SOX risk hefty fines and legal penalties. These costs also extend to potential lawsuits and settlement fees, making non-compliance far more expensive than the costs of maintaining compliance.

4. Reputational Damage and Customer Trust Issues

Beyond financial penalties, SOX violations can erode investor confidence and damage a company’s reputation. Loss of customer trust may lead to reduced business opportunities and stock price declines, adding a significant long-term cost that organizations must consider.

‍

7. How CloudEagle.ai Can Lower SOX Compliance Costs

Here’s how CloudEagle.ai helps you with enterprise governance:

A. Shadow AI Discovery: Surface Every Tool Before You Govern It

CloudEagle.ai detects Shadow AI through browser extensions, firewall logs, Zscaler, CrowdStrike, and finance signals simultaneously, building a single source of truth across every AI tool in use, sanctioned or not.

Here's how multi-signal Shadow AI discovery is designed to work:

‍

‍

In CloudEagle.ai's AI application inventory, every tool appears with adoption by team and department. 

‍

‍

It surfaces whether it was sanctioned or discovered through external signals, and whether it carries GenAI capabilities that were never part of the original procurement decision.

B. Secure Browser and Flash Page: Redirect Before Data Enters an Unapproved Session

CloudEagle.ai's browser plugin catches what CASB, DLP, and LLM gateways all miss, the moment an employee opens an unapproved AI tool in a browser tab. Here’s how the browser plugin works:

‍

‍

When that happens, a real-time flash page steps in before any company data is entered, redirecting the employee to the approved alternative automatically.

‍

‍

In CloudEagle.ai's Secure Browser policy view, flash page rules are configurable by team, department, and tool so Engineering can be permitted Cursor while redirected away from consumer ChatGPT.

‍

‍

Every redirect is logged automatically, tool accessed, sanctioned status, flash page triggered, and timestamp. The audit record exists in real time without additional effort.

C. Data Loss Prevention: Block Sensitive Data Before It Reaches the Model

CloudEagle.ai’s DLP operates at the prompt entry layer, catching what is typed into an AI interface before it is submitted to the model. 

When an employee attempts to paste sensitive content like PII, PHI, financial data, proprietary code, into an AI tool, CloudEagle.ai fires before the content leaves the browser.

‍

‍

In CloudEagle.ai's DLP policy view, sensitive content categories are configurable. Credit card numbers, PHI, source code, and proprietary data each carry their own enforcement rules.

D. GenAI Risk Scoring: Prioritize the Riskiest Apps First

CloudEagle.ai automatically assigns a GenAI risk score to every AI tool and feature in the environment, powered by Netskope's Cloud Confidence Index.

‍

‍

Every tool is scored on data residency, training data use, security posture, and compliance alignment, so security teams have a prioritized remediation list, not a flat inventory of 200 tools with no indication of where to start.

‍

‍

In CloudEagle.ai's risk scoring view, every AI vendor appears with its risk level, whether it trains on company data, and whether it processes regulated data without a formal agreement in place.

E. AI Usage and Token Consumption Tracking: See Who Is Using What and at What Scale

CloudEagle.ai tracks token consumption and API spend for Claude, ChatGPT, Cursor, Gemini, and GitHub Copilot, on per user, per team, per department basis.

This matters for blast radius because unusual token consumption is often the first behavioral signal that something is wrong. Here's how per-user AI usage tracking is designed:

‍

‍

In CloudEagle.ai's AI usage dashboard, every user's consumption is visible by model tier and time period. 

‍

‍

Security teams identify anomalies and Finance gets the chargeback data needed to enforce budget accountability.

F. User Access Reviews: Review Risky Access Without the Manual Work

CloudEagle.ai centralizes user access reviews, giving security teams visibility into roles, permissions, SSO/HRIS presence, and elevated privileges in one place.

Here’s how CloudEagle.ai’s access review process works:

‍

Reviewers can focus on high-risk users and ex-employees instead of manually checking access across individual applications. CloudEagle.ai also flags managers with incomplete reviews, reducing the risk of rubber-stamped approvals.

‍

Reviews can be scheduled and assigned automatically. When access is rejected, CloudEagle.ai initiates deprovisioning and attaches proof of removal, eliminating manual evidence collection from JIRA and other systems.

The result is a complete trail from review → remediation → evidence → audit report, helping teams complete access reviews in days instead of months

G. SaaS Security Posture Management

CloudEagle.ai gives security teams a continuously updated view of application-level security posture across the SaaS stack, replacing manual app-by-app checks for controls such as MFA, SSO, and NIST 800 compliance.

Here’s how CloudEagle.ai consolidates security posture:

‍

‍

CloudEagle.ai pulls federation signals such as MFA and SSO directly from Okta and Entra, retrieves compliance data through APIs where available, and supplements it with Netskope’s Cloud Confidence Index.

These signals are rolled into a single pass/fail view for each application. Teams can also manually add information that cannot be pulled automatically, such as application ownership.

This gives security teams one continuously updated view of SaaS security posture instead of relying on scattered checks and stale compliance spreadsheets.‍

‍

‍

8. Conclusion

SOX compliance can be costly and complex, but the right tools help cut costs and keep SaaS security strong. CloudEagle.ai simplifies compliance with automation, smart access controls, and centralized SaaS governance.

Features like automated onboarding/offboarding, role-based and just-in-time access, and continuous access reviews reduce manual work and hidden expenses. The Self-Service App Catalog enables employees, limits shadow IT, and optimizes SaaS spend.

Ready to take control of your SOX compliance and reduce costs without compromising security? 

Schedule a demo to see how automation and centralized SaaS management can transform your SOX compliance program.

‍

9. FAQs

1. Doesn't SOX audit prep pull key employees away from their jobs for weeks?

CloudEagle.ai cuts that downtime by putting access control, compliance reporting, and risk monitoring in one dashboard. It connects to HR systems, SSO, and over 500 SaaS applications, so audit evidence is ready without pulling people off their work to reconcile spreadsheets.

2. Aren't user access reviews one of the most expensive parts of SOX compliance?

CloudEagle.ai automates SOX access reviews to cut that cost. It continuously monitors who has access to what, sends reminders to reviewers, and runs auto-revocation workflows for stale or unused access. Dezerv used CloudEagle.ai to automate its app access review process.

3. Can't a former employee's leftover access turn into a costly SOX finding?

With CloudEagle.ai, a departing employee's access is revoked immediately. Offboarding runs automatically on predefined rules tied to role, department, and location, which removes the manual errors that lead to audit findings and expensive remediation.

4. Doesn't shadow IT create compliance gaps that are expensive to fix late?

CloudEagle.ai finds shadow IT early. It identifies unauthorized SaaS apps through identity systems, finance platforms, and credit card transaction analysis, then steers employees to a vetted catalog of approved apps. Gaps are closed before the audit instead of during it.

5. Isn't granting temporary access to financial systems a SOX risk?

CloudEagle.ai makes temporary access safe with Just-In-Time access. Permissions are granted only when needed and revoked automatically once the task is done, and every grant is recorded in audit-ready access logs. This supports SOX's least-privilege expectations without slowing work down.

‍

CloudEagle.ai recognized in the 2025 Gartner® Magic Quadrant™ for SaaS Management Platforms
Download now
gartner chart
5x
Faster employee
onboarding
80%
Reduction in time for
user access reviews
30k
Workflows
automated
$15Bn
Analyzed in
contract spend
$2Bn
Saved in
SaaS spend

Streamline SaaS governance and save 10-30%

Book a Demo with Expert
CTA image