HIPAA Compliance Checklist for 2025

TL;DR
- Manual compliance is a liability in 2026. Regulators, enterprise buyers, and audit cycles have outpaced spreadsheet-based processes.
- SaaS compliance automation tools replace evidence chasing, access reviews, and control mapping with continuous, automated workflows.
- The market is growing fast. SOC 2 compliance automation tools alone are projected to hit $2.7B by 2028.
- The right tool depends on your biggest gap: certification speed, privacy governance, internal audit, or SaaS access control.
- CloudEagle.ai is the only platform on this list that tackles compliance from the access and identity layer, covering shadow IT, shadow AI, and license governance in one place.
Somewhere right now, a compliance manager is copying evidence into a shared drive folder by hand. We've all been there, and in 2026 there's genuinely no reason to still be there.
The GRC software market sits at $60.7 billion this year, and SaaS compliance automation tools alone account for $1.3 billion of it and growing fast.
Manual compliance doesn't scale, regulators aren't slowing down, and enterprise buyers now require SOC 2 certification before they'll sign a contract.
This list covers the 10 best SaaS compliance automation tools in 2026: what each one does, who it's built for, what it costs, and how audit-ready it actually makes you.
1. What Is a SaaS Compliance Automation Tool?
A SaaS compliance automation tool replaces the manual, spreadsheet-driven side of compliance with continuous, automated workflows.
It pulls audit evidence from your SaaS and cloud tools, maps your controls to frameworks like SOC 2 and ISO 27001, and flags access that no longer belongs, so audits become a confirmation instead of a scramble.
- Evidence collection: pulls audit evidence automatically from your SaaS tools, cloud providers, and infrastructure.
- Control mapping: aligns your security controls to SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, and frameworks like the NIST Cybersecurity Framework.
- Access reviews: automates who has access to what, and flags what doesn't belong.
- Policy management: distributes, tracks, and enforces security policies across your org.
- Audit readiness: keeps you continuously ready instead of scrambling every quarter.
- Risk management: identifies, scores, and tracks compliance risks in real time.
The best SaaS compliance automation tools don't just tick boxes. They give you a live view of your compliance posture, so an audit becomes confirmation, not crisis.

2. Why SaaS Compliance Automation Tools Are Important in 2026
A few things have shifted that make SaaS compliance automation more urgent than it was even a year ago.
Why Does the Regulatory Pile Keep Growing?
GDPR, CCPA, SOC 2, ISO 27001, HIPAA, and FedRAMP now overlap for most enterprises managing more than one framework at once. Doing that by hand isn't just painful. It's a liability.
How Is SaaS Sprawl Creating New Blind Spots?
Employees adopt and abandon unapproved tools, including generative AI, without oversight. Every unsanctioned app is a compliance gap nobody knows exists yet.
Why Do Enterprise Deals Now Depend on Compliance?
Most enterprise buyers require SOC 2 certification before they'll sign a contract with a SaaS vendor. Your compliance posture is now a sales asset, or a dealbreaker.
SOC 2 compliance automation tools are forecast to grow from $850M in 2025 to $2.7B by 2028, one of the fastest-growing segments in enterprise software.
The tools below show what closing that gap actually looks like.
3. What Are the Best SaaS Compliance Automation Tools for Audits in 2026?
Here are the 10 SaaS compliance automation tools worth putting in front of your team this year, starting with the one that tackles compliance from the access and identity layer most others treat as an afterthought.
1. CloudEagle.ai
Best for: Enterprise SaaS compliance, access governance, and audit-ready identity management
CloudEagle.ai is an AI-powered SaaS Management, AI Governance, and Identity Governance platform that helps organizations discover, govern, and secure SaaS and AI applications across the enterprise, including applications outside traditional SSO and IT visibility.
For compliance teams, CloudEagle.ai connects application security posture, vendor risk, identity governance, and compliance monitoring. Teams can assess SaaS applications using security scores, certifications, breach history, data residency, GenAI indicators, and compliance posture while maintaining visibility into users and access.
Key capabilities
- SaaS security posture monitoring: Assess application security posture using security scores, breach history, certifications, data residency, and other risk indicators.
- SaaS and Shadow IT discovery: Identify applications outside traditional IT and SSO visibility that may fall outside established compliance controls.
- Vendor security and compliance visibility: Review vendor certifications, including SOC 2 and ISO 27001, alongside application security and risk information.
- Multi-framework compliance: Support compliance programs across SOC 2, ISO 27001, HIPAA, GDPR, and the EU AI Act.
- Identity and access governance: Automate provisioning and deprovisioning, conduct access reviews, and identify excessive or inappropriate access.
- Continuous compliance monitoring: Connect application, identity, vendor, and policy information to identify compliance risks between audit cycles.
- Automated audit evidence: Collect and organize evidence associated with access governance and compliance controls.
“We lacked confidence in our access certifications. Reviews were happening, but we couldn't clearly answer who had access, why it existed, or whether it was still valid. CloudEagle brought structure and accountability to user access reviews without reviewer fatigue.”
— Michal Lipinski, Director of IT & Security, ICEYE
ICEYE reported reducing manual access-review work by 90% and saving more than 1,500 hours annually after centralizing its access reviews. Read the case study.
Pricing
Custom pricing; demo required.
What If Your SaaS Compliance Ran Continuously?


2. Vanta
Vanta pioneered the continuous compliance model and is still one of the most recognized names in SaaS audit automation, a solid choice for teams that need certification fast without deep in-house compliance expertise.
What it does
- Connects to 300+ integrations to pull evidence automatically.
- Maps controls across SOC 2, ISO 27001, HIPAA, GDPR, and PCI DSS at once.
- Automates employee security training and policy acknowledgment tracking.
- Provides real-time compliance dashboards and risk scoring.
- Offers vendor risk management and questionnaire automation.
Pricing: Starts around $5,000-$7,000/year for startups. Enterprise pricing on request.
3. Drata
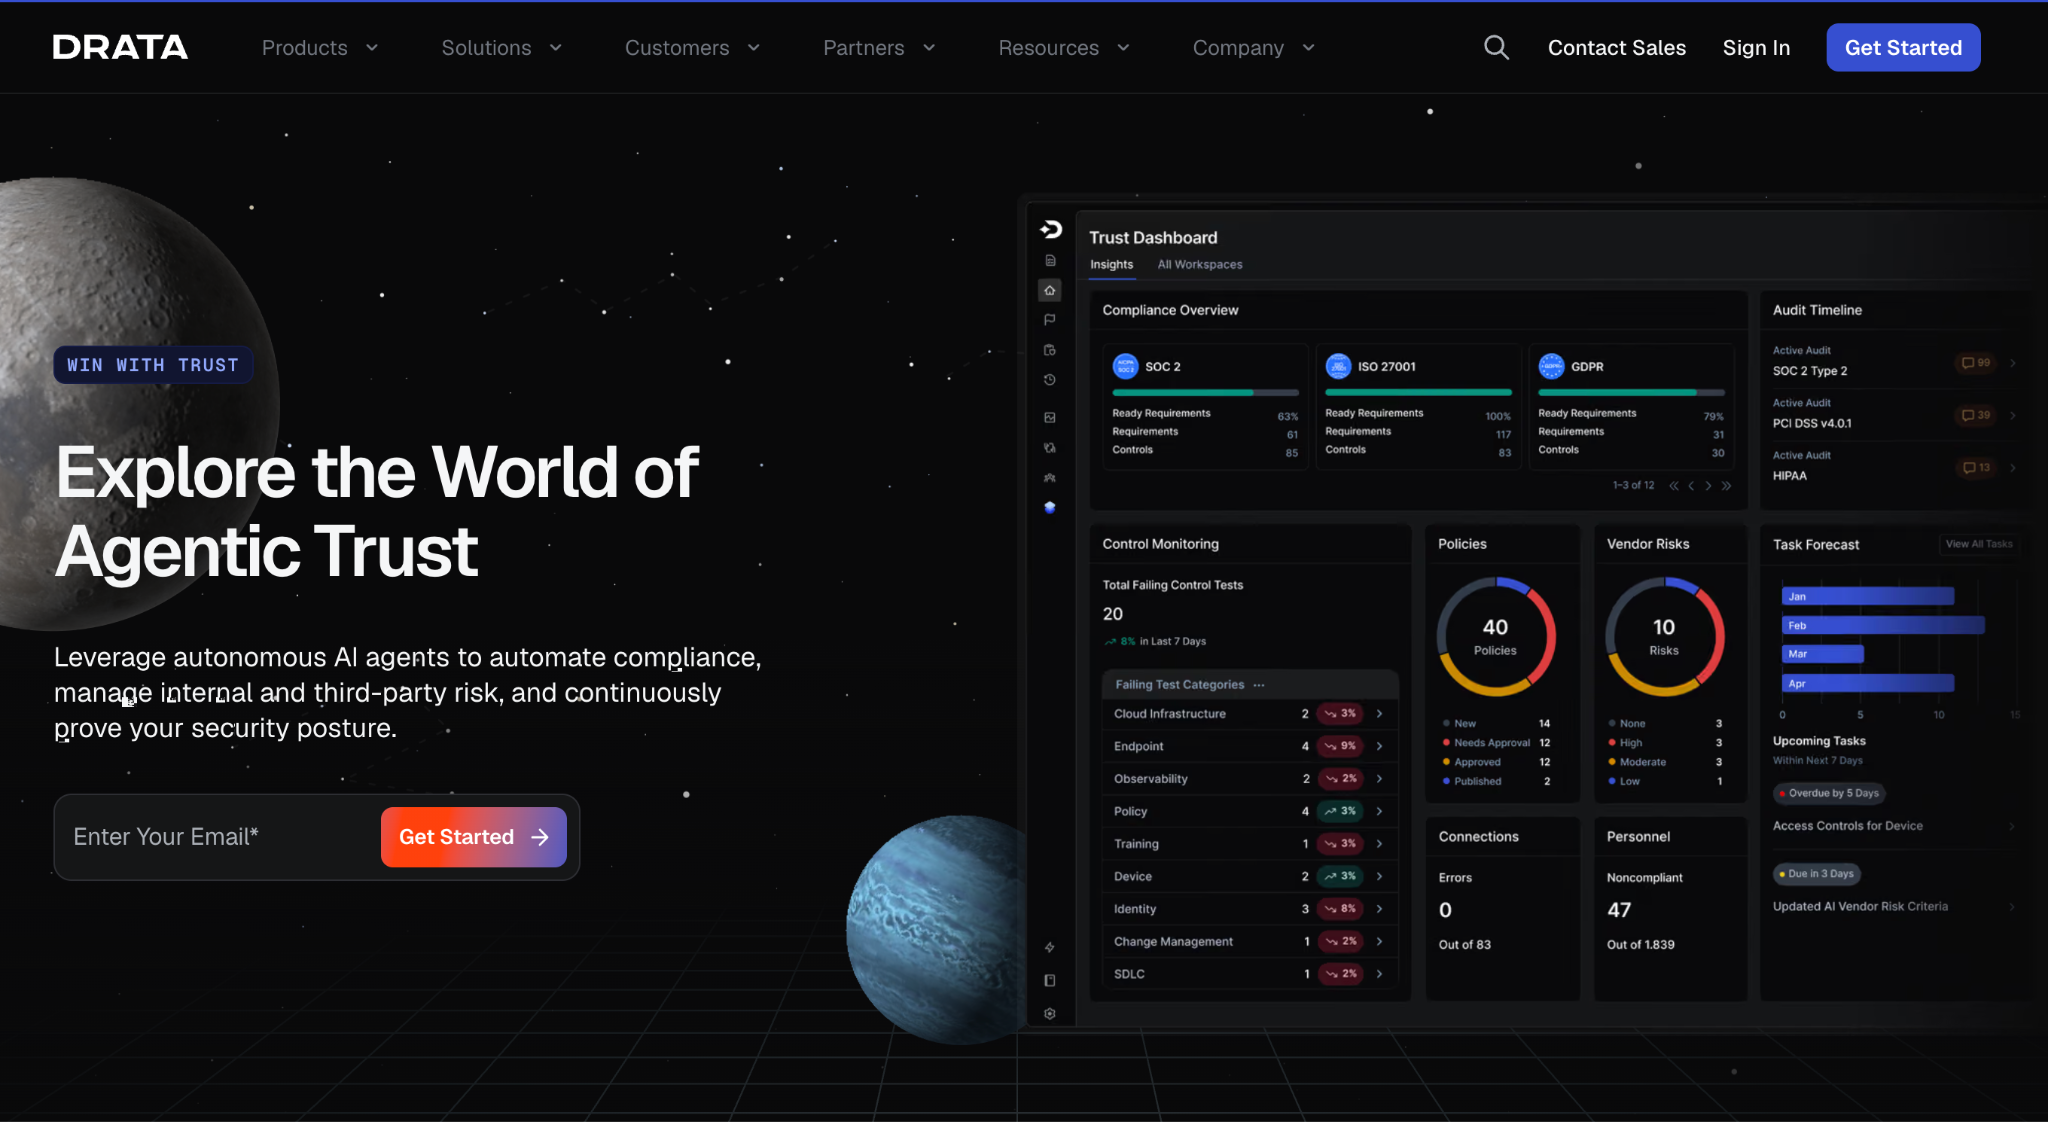
Drata goes deep where Vanta goes broad, one of the stronger picks for mature enterprise programs managing several certifications at once.
What it does
- Supports 16+ frameworks simultaneously with continuous control monitoring.
- Automates evidence collection from cloud providers, MDM tools, and SaaS apps.
- Real-time compliance health scoring and risk quantification.
- Security training, automation, and policy management built in.
Pricing: Starts around $10,000/year. Enterprise plans on request.
4. Secureframe
Secureframe pairs solid compliance automation with a notably hands-on customer success team.
What it does
- Automated evidence collection across AWS, GCP, Azure, and 200+ SaaS integrations.
- Covers SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, and FedRAMP.
- Continuous control testing with real-time failure alerts.
- Vendor security assessment workflows built in.
Pricing: Starts around $6,000-$8,000/year. Custom pricing for enterprise.
5. OneTrust
OneTrust operates at a different level than most tools here: less about SOC 2 certification, more about the full enterprise privacy governance stack.
What it does
- Comprehensive privacy program management across GDPR, CCPA, LGPD, and more.
- Data discovery and classification across cloud and on-premise environments.
- Third-party risk management and vendor assessments.
- Consent management and data subject rights automation.
Pricing: Modular pricing starting around $8,000/year. Enterprise contracts negotiated directly.
6. LogicGate
LogicGate takes a workflow-first approach, with a drag-and-drop builder for teams that want their GRC process shaped around their own workflow instead of a template.
What it does
- Drag-and-drop workflow builder for fully custom compliance processes.
- Risk management with quantification and scenario modeling.
- Audit management and evidence tracking.
- Third-party and vendor risk workflows.
Pricing: Starts around $20,000/year. Enterprise pricing on request.
7. Hyperproof
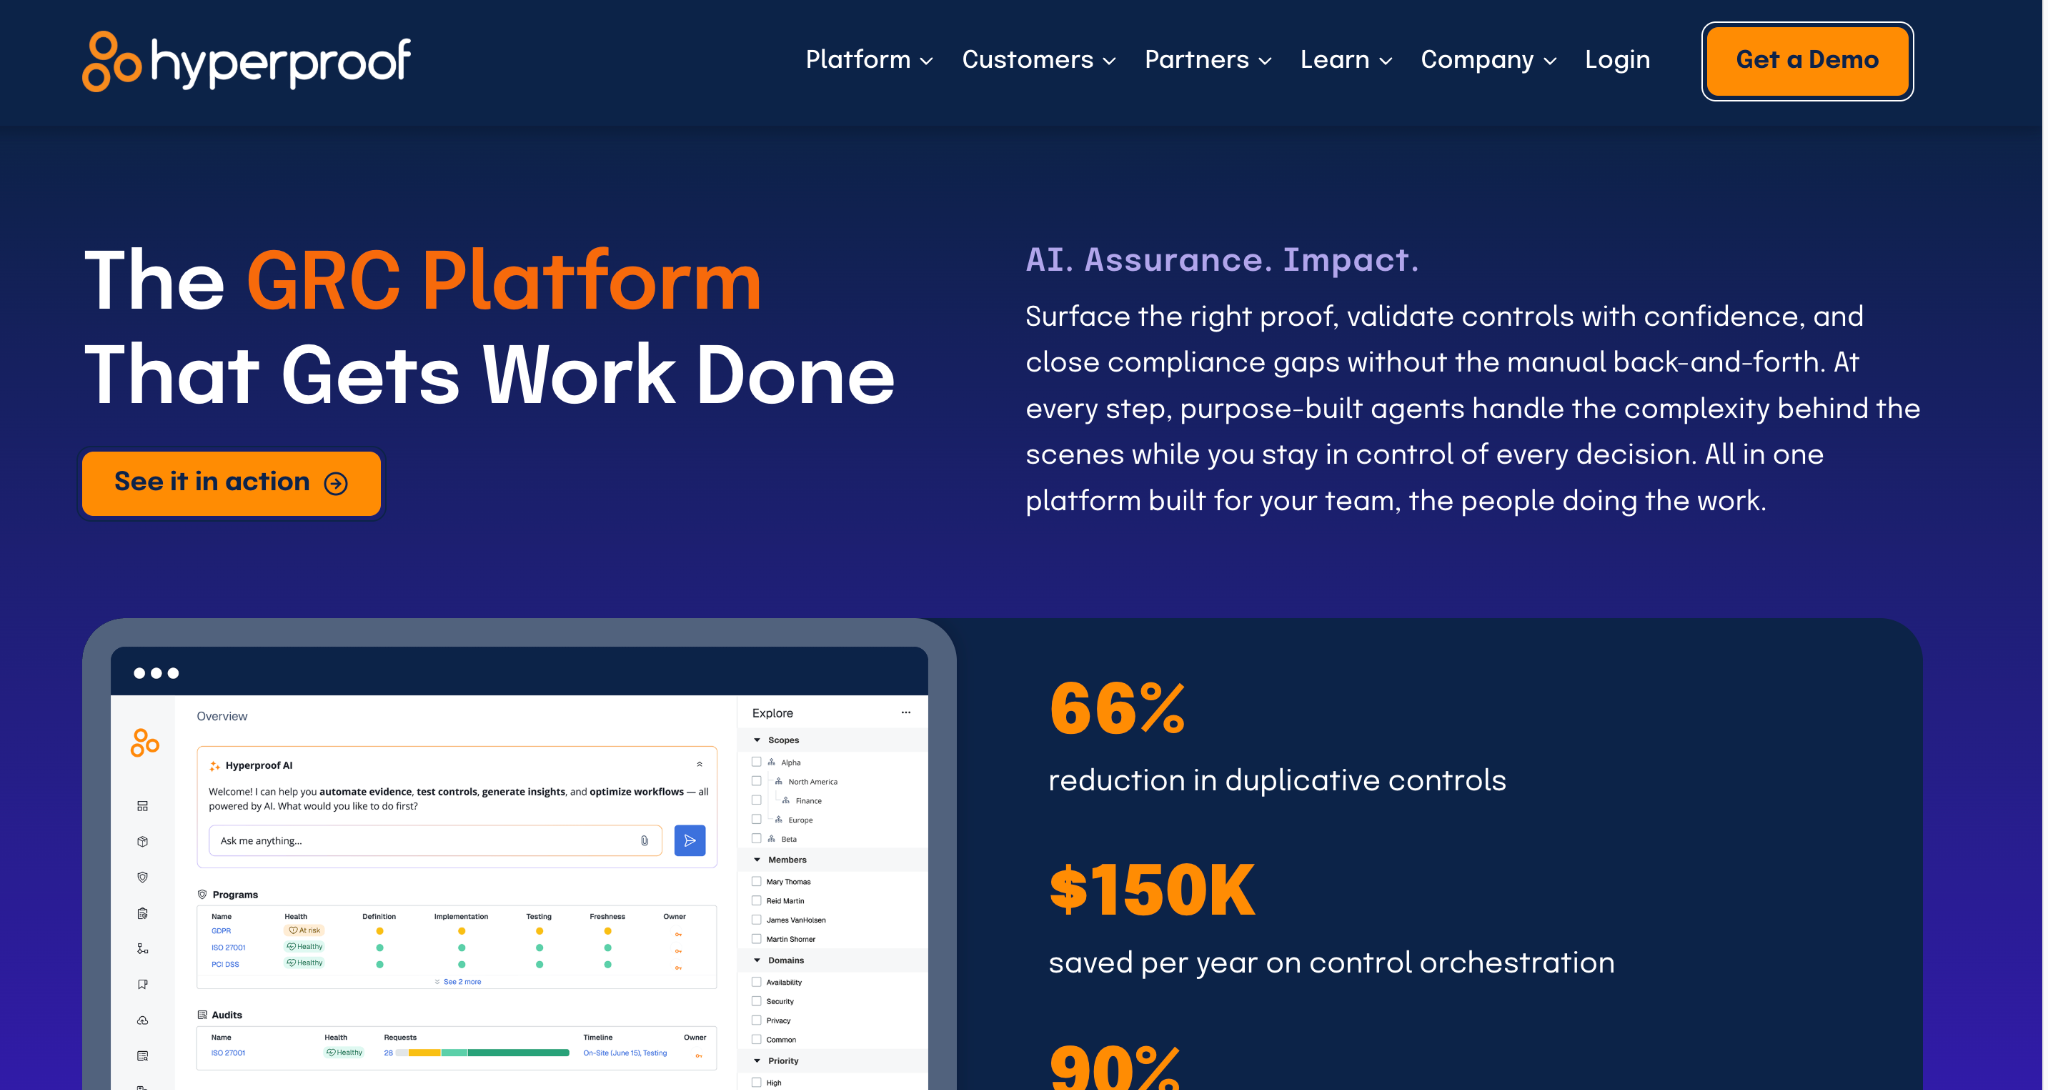
Hyperproof is built for the operational side of compliance, a strong pick when evidence collection means coordinating across ten or more internal stakeholders.
What it does
- Centralized evidence collection and control management across frameworks.
- Cross-framework compliance mapping to eliminate duplicate work.
- Task assignment and workflow management for audit coordination.
- Risk register and compliance program tracking.
Pricing: Starts around $12,000/year. Enterprise plans on request.
8. Optro
Optro covers the full compliance spectrum, one of the few tools here that seriously addresses internal audit and SOX.
What it does
- Internal audit management and scheduling.
- SOX compliance and financial controls testing.
- Risk management with heat maps and quantification.
Pricing: Enterprise pricing only, typically starting around $50,000/year depending on modules.
9. ServiceNow GRC
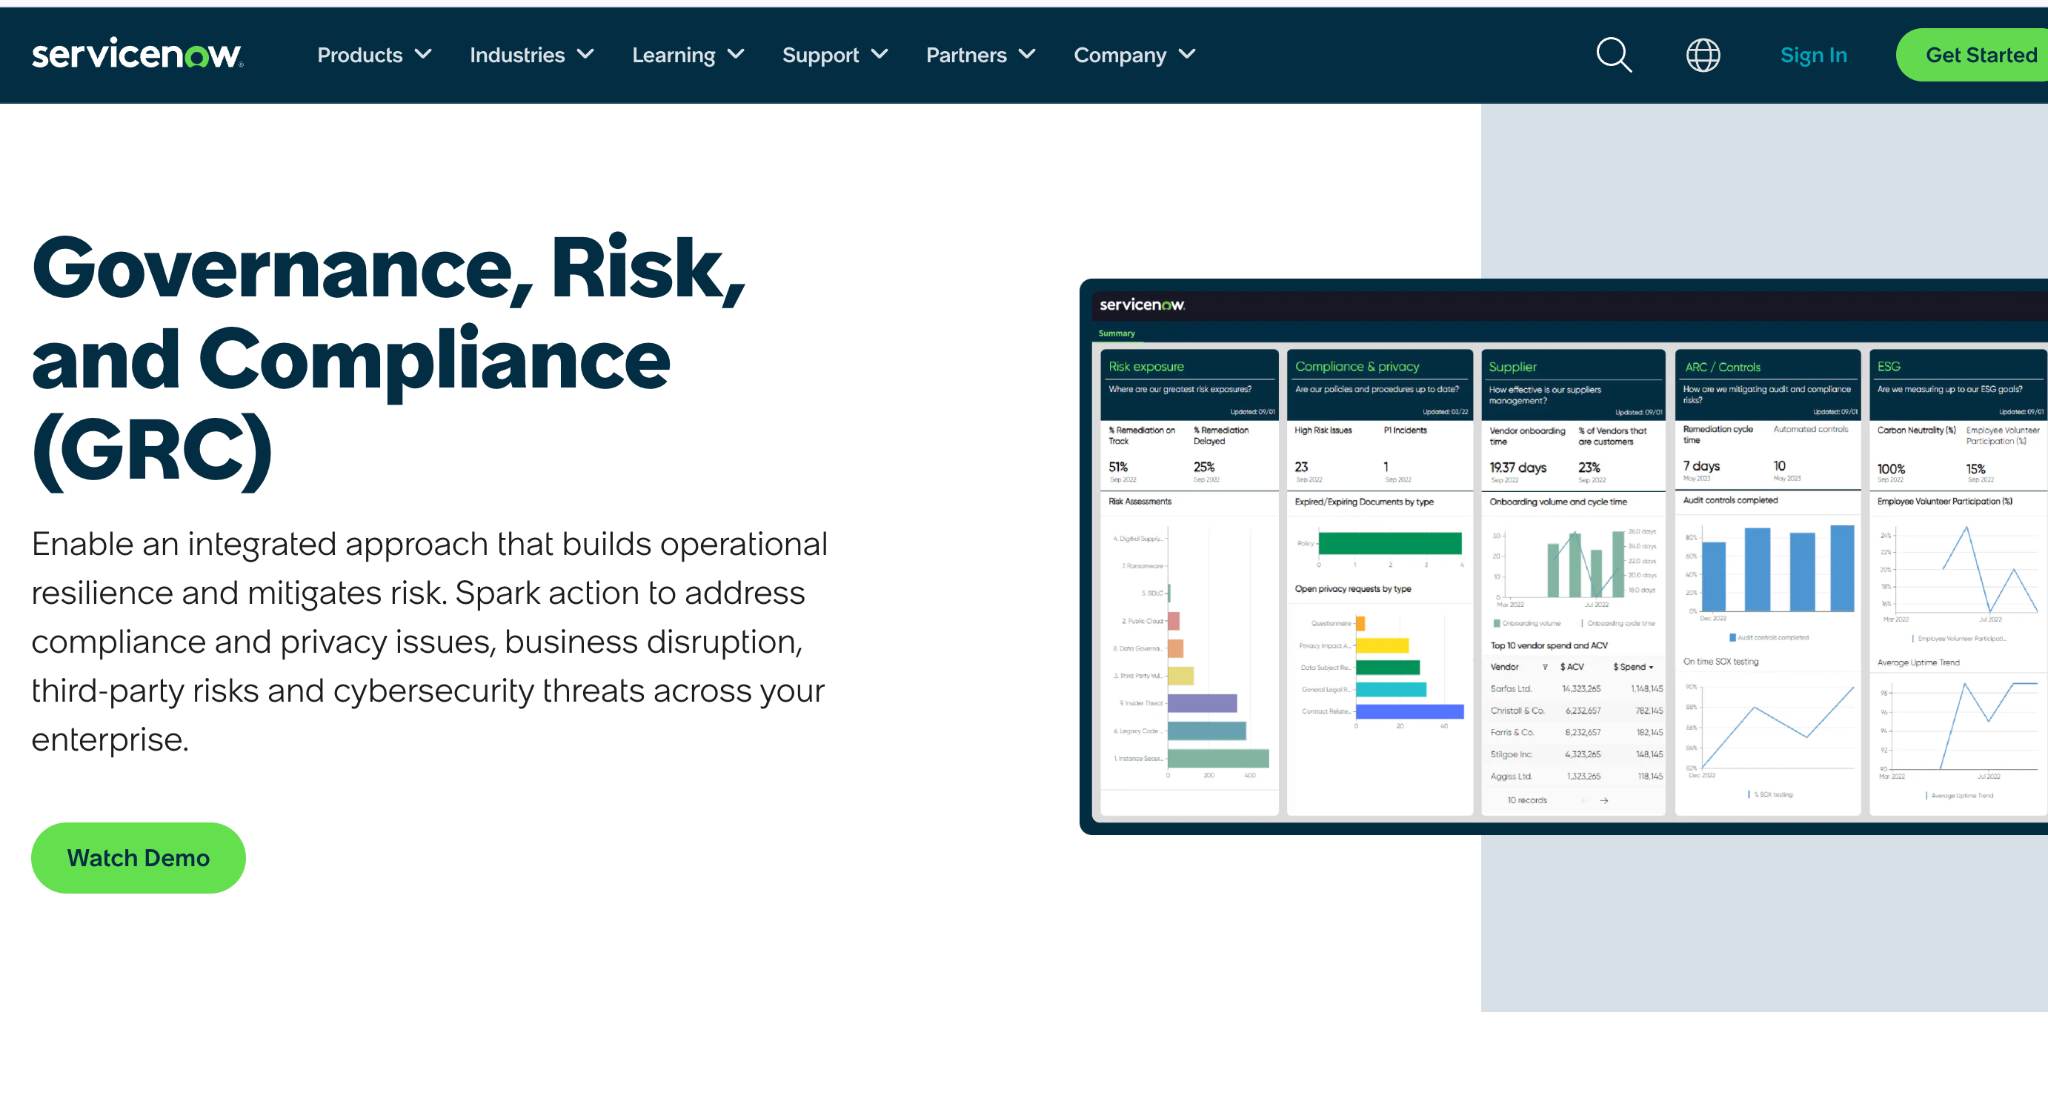
ServiceNow GRC is the compliance and risk module inside the broader ServiceNow ecosystem, and its edge is tying compliance findings directly into the change management and incident response you already run there.
What it does
- Policy and compliance management integrated with ITSM workflows.
- Risk management with real-time monitoring and remediation workflows.
- Vendor risk assessments and third-party governance.
Pricing: Add-on to existing ServiceNow contracts, typically $30,000+ annually depending on org size and modules.
10. Sprinto
Sprinto is built for high-growth SaaS startups: faster to deploy, more affordable, and designed to get you certified without a heavy internal lift.
What it does
- Automated evidence collection from cloud and SaaS tools.
- Covers SOC 2, ISO 27001, HIPAA, GDPR, and SOC 1.
- Security training and policy management included.
Pricing: Starts around $6,000-$8,000/year. Scales with company size.
4. Which SaaS Compliance Automation Tool Is Right for You?
Manual compliance had a good run. It's over.
In 2026, SaaS compliance automation isn't about making audits slightly less painful. It's about running a compliance posture continuously in the background, so your team stops reacting and starts staying ahead.
The right platform comes down to where your biggest gap actually sits. Fast certification: Vanta, Drata, or Sprinto. Privacy governance: OneTrust. SOX: Optro. Custom GRC: LogicGate. SaaS access and shadow IT: CloudEagle.ai.
If your compliance gaps live in SaaS access governance, shadow IT visibility, and license compliance, that's exactly what we built CloudEagle.ai for.
Pick the tool that meets your compliance program where it actually is, not where the marketing decks say it should be.
Frequently Asked Questions
- Can SaaS Compliance Be Managed Without Adding More Manual Work?
It can be difficult when compliance teams have to collect information from multiple applications, vendors, and internal systems. CloudEagle.ai helps centralize SaaS compliance data and automate governance workflows, reducing the manual effort involved in keeping compliance information current. - How Can You Identify Compliance Risks Across a Large SaaS Portfolio?
Reviewing every application individually can leave gaps as the SaaS environment grows. CloudEagle.ai provides a centralized view of applications, their security and compliance posture, and relevant risk signals so teams can identify applications that need further review. - What Happens When Employees Use SaaS Apps Outside the Approved Stack?
Unapproved applications can introduce security, privacy, and compliance risks that may not appear in standard IT systems. CloudEagle.ai helps surface these applications and bring them into the same governance process as the rest of the SaaS environment. - Can SaaS Compliance Teams Keep Vendor Information Up to Date?
Keeping track of vendor certifications, security information, and compliance status manually can become difficult across a large application portfolio. CloudEagle.ai centralizes vendor and application information to make ongoing reviews easier to manage. - How Does CloudEagle.ai Support Compliance as the SaaS Environment Changes?
SaaS portfolios change continuously as employees adopt new applications, access requirements change, and vendors update their security posture. CloudEagle.ai provides ongoing visibility into applications, access, and compliance-related risk so teams can address changes without relying entirely on periodic manual reviews.
What If Your SaaS Compliance Ran Continuously?