HIPAA Compliance Checklist for 2025

The auditor wants a list of everyone with admin access to the CRM and the production database.
The IT lead at a 600-person company exports users from Entra ID, opens the HR spreadsheet next to it, and spends the afternoon matching names.
Three contractors who left in the spring are still active, and one of them still holds admin rights.
Most mid-sized companies run identity governance this way.
CloudEagle.ai is recognized in KuppingerCole Analysts’ 2026 Leadership Compass for Lean Identity Governance and Administration (IGA), and we built our identity governance for the teams stuck in that afternoon.
Why Do Mid-Sized Companies Struggle With Identity Governance?
These teams need the same core controls an enterprise needs: lifecycle automation, access requests, access reviews, and reporting an auditor will accept.
What they don’t have is an identity team or a year to roll out a suite.
Access usually runs through Active Directory or Entra ID, help desk tickets, scripts, and spreadsheets. Those methods break quietly.
48% of former employees still have app access months after leaving, according to our IGA Report. Nobody notices until a review forces the question.
What Changed Now That Audits and AI Agents Reached Small Teams?
Customers send security questionnaires. Insurers and regulators ask who can reach sensitive data. Structured governance used to be an enterprise problem, and now it lands on companies with four people in IT.
Employees are also no longer the only identities. Service accounts, API keys, and AI agents now sit alongside the workforce.
Many are created by a developer or a SaaS integration without IT’s involvement, and few have a named owner.
“Identity governance was built for organizations with a dedicated identity team and a long implementation runway. Most companies have neither, and their identity risk is growing faster than their headcount,” said Nidhi Jain, CEO of CloudEagle.ai. “AI agents and non-human accounts have made the gap wider. CloudEagle.ai exists so a small IT team can govern every identity, and can show who owns it, what it accesses, and whether it should still exist.”
What Does Identity Governance Look Like for a Small IT Team?
Our identity governance gives a lean team these outcomes without a dedicated identity program:
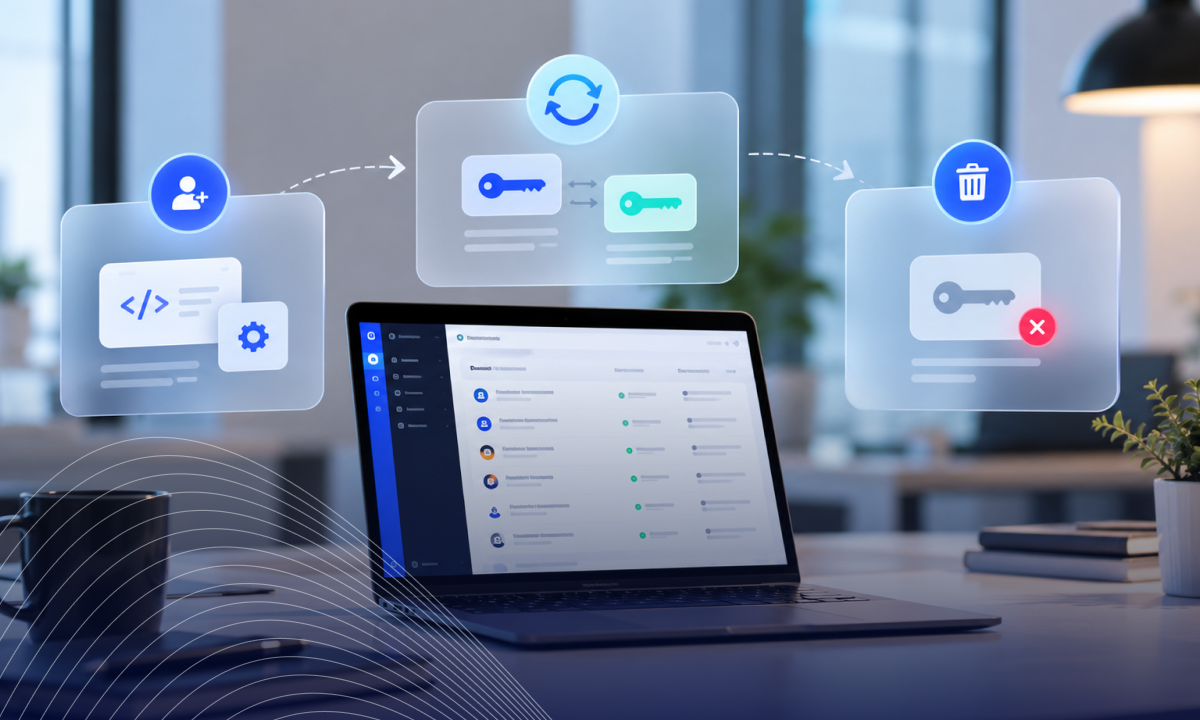
- Access on Day One, Nothing Left Behind: New hires start with the apps their role needs, and leavers lose every login the moment HR records the exit. IT changes an approval path through no-code workflows, with no engineering ticket.
- Every Non-Human Identity Has an Owner: Each service account, API key, and AI agent gets a named owner and a clear view of what it’s accessing. Excessive permissions get caught and fixed by revoking access or rotating keys.
- App Requests Without the Help Desk Queue: Employees get the apps they need as soon as the right owner approves.
- Temporary Access That Stays Temporary: Access ends on its own when the period does, so short-term access never becomes permanent.
- Access Reviews Ready for the Auditor: Reviewers see high-risk users and former employees first, across SaaS and AI apps, and every decision leaves evidence behind.
- No App Left Unseen: An SSO export only shows the apps connected to SSO. EagleIQ, our context graph, works from sign-on and browser activity and other application signals, so tools a team signed up for on a credit card show up next to the approved stack.
- Risk Flagged Before It Becomes an Incident: Anomalies and risky access are scored and surfaced. With EagleEye, an IT lead can ask which accounts look risky this week and get an answer without building a report.
How Do Access Reviews and License Spend Connect?
Identity governance sits on the same platform as our SaaS usage intelligence, so the access review and the license review become one exercise.
An account nobody has used in 90 days is a security finding and a wasted seat at once.
When we remove the access, the license goes back into the pool. The cleanup that satisfies the auditor also shows up as savings Finance can count.
Identity governance stops being a cost line IT has to defend.
What Should You Ask Before Choosing an Identity Governance Platform?
If you are evaluating identity governance for the first time, these four questions sort the vendors quickly:
- How long until the first access review runs on live data, measured in weeks?
- Can it find apps that never went through SSO or procurement?
- Does it govern service accounts and AI agents with the same workflows as employees?
- When access is removed, does the license spend change with it?
The answers separate platforms built for a lean team from ones scaled down from an enterprise suite.
Can your team name the owner of every account in your SaaS and AI stack? See who still has access, which accounts no one owns, and what each unused login costs you.
Name the Owner of Every Account in Your Stack