Security Best Practices & Guides

10 Best GRC Platforms in 2026: A Buyer's Comparison

Share via:
Written by:
CloudEagle.ai Team
Reviewed by
Nidhi Jain
Last Updated:
October 27, 2026
blog-cms-banner-bg
Little-Known Negotiation Hacks to Get the Best Deal on Slack
cta-bg-blogDownload Your Copy

HIPAA Compliance Checklist for 2025

Download PDF

‍

Managing governance, risk, and compliance is becoming more complex as businesses adopt AI tools, expand their SaaS environments, and face evolving regulatory requirements. According to the World Economic Forum's Global Cybersecurity Outlook 2026, 87% of surveyed organizations identified AI-related vulnerabilities as the fastest-growing cyber risk during 2025.

The right governance, risk, and compliance (GRC) platform helps organizations manage risks, streamline audits, monitor controls, and maintain compliance. However, capabilities vary across enterprise GRC suites, compliance automation tools, and specialist governance solutions.

This guide compares the 10 best GRC platforms in 2026, starting with CloudEagle.ai, to help businesses evaluate their options based on features, integrations, scalability, and pricing considerations.

‍

1. What is GRC Platform?

Governance, risk, and compliance (GRC) software helps organizations manage business risks, internal policies, and regulatory requirements through a centralized platform. It streamlines risk assessments, audit management, control monitoring, and compliance reporting.

Most GRC platforms support frameworks such as SOC 2, ISO 27001, and GDPR. While enterprise GRC software covers broader risk and governance processes, compliance automation tools focus on tasks such as evidence collection and control monitoring. 

Organizations managing growing SaaS environments and AI adoption may also need dedicated capabilities for SaaS security, access governance, and AI risk management.
‍

Compliant on Paper. Exposed in Practice?

Find the gaps before auditors do
Find Out

‍

2. How We Evaluated the Best GRC Platforms

We compared the platforms based on their publicly documented capabilities, primary use cases, integration considerations, scalability, and pricing availability. The goal is to help buyers identify a suitable shortlist, not to replace product demonstrations or hands-on evaluation.

The comparison considers six criteria:

  • Risk and compliance management: Risk assessments, policy management, control mapping, and regulatory framework support.
  • Audit and evidence management: Audit workflows, evidence collection, control testing, and remediation tracking.
  • Automation and integrations: Connections with identity providers, cloud services, HR systems, and security tools.
  • SaaS and AI governance: Application visibility, access governance, and AI risk oversight where supported.
  • Scalability and usability: Configuration requirements, administrative effort, and suitability for different organizational needs.
  • Pricing and implementation: Pricing availability, licensing considerations, deployment complexity, and ongoing maintenance.

The platforms are presented according to their primary use cases, recognizing that full-suite GRC platforms and specialist governance tools do not offer identical capabilities.

3. 10 Best GRC Platforms in 2026

The best GRC platform depends on whether an organization needs enterprise-wide risk management, automated compliance workflows, audit management, or stronger governance across SaaS applications and AI tools. 

This list includes both full-suite GRC platforms and specialist governance solutions. The ranking is an editorial selection, not a claim that every platform offers the same capabilities. The right choice depends on your organization's risk management, compliance, and operational governance requirements.

‍

Platform Best for
CloudEagle.ai SaaS security, AI governance, and identity oversight
ServiceNow IRM Connected risk and business workflows
Archer Configurable, organization-wide risk management
OneTrust Privacy, third-party risk, and AI governance
LogicGate Risk Cloud Adaptable risk and compliance workflows
Optro Internal audit, SOX, and broader GRC processes
MetricStream Complex risk and compliance programs
Diligent One Board oversight and enterprise risk reporting
Hyperproof Evidence management and multiple frameworks
Vanta Automated evidence collection and control monitoring

‍

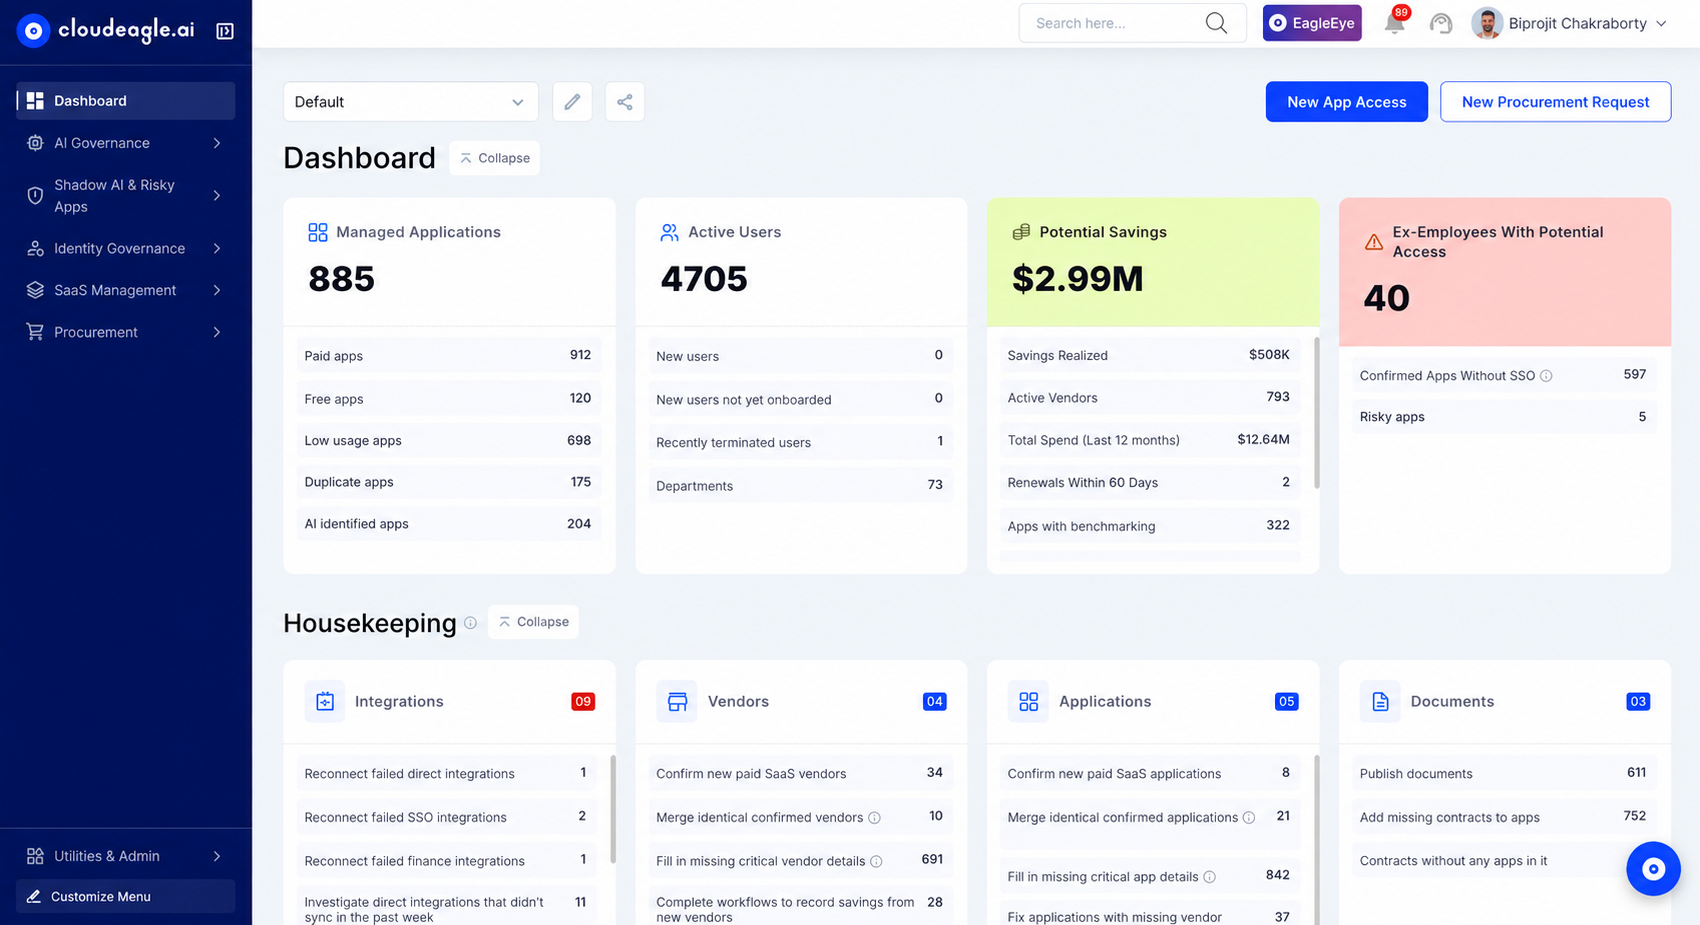
A. CloudEagle.ai

‍

‍

CloudEagle.ai helps GRC teams govern the fastest-growing source of compliance risk: access across SaaS apps, AI tools, and non-human identities.

Instead of collecting evidence once a quarter, compliance and security teams get continuous control monitoring over who can access what, risk scores for every unsanctioned app and AI tool, and automated access reviews that produce audit-ready evidence for SOC 2, SOX, HIPAA, PCI DSS, ISO 27001, and GDPR.

It also extends governance to AI, enforcing usage policy and documenting decisions so AI adoption doesn’t become an audit finding.

CloudEagle.ai is named in the 2026 Gartner Market Guide for IGA and recognized as a Product Leader in KuppingerCole’s 2026 Leadership Compass for SaaS Security and AI Governance.

Key features:

  • Audit-Ready Access Reviews: Automates access reviews across every connected app and logs each certification, revocation, and approval as evidence for SOC 2, SOX, and ISO 27001 audits.
  • Continuous Access Control Monitoring: Monitors risky activity across SaaS and AI apps around the clock and automatically removes excessive privileges, so controls hold between audits, not just during them.
  • Shadow IT and Shadow AI Risk Scoring: Discovers apps adopted outside IT and SSO and assigns each a risk score, giving risk teams a complete, prioritized inventory of third-party exposure.
  • AI Governance and Policy Enforcement: Enforces AI usage policy inside the browser, requires approval for new AI tools, and flags sensitive data shared with public AI services, supporting frameworks like ISO 42001 and the EU AI Act.
  • Non-Human Identity Governance: Tracks AI agents, service accounts, and API keys, including what each can access, closing a blind spot most identity audits miss.
  • Joiner-Mover-Leaver Controls: Revokes all access at offboarding with a complete audit trail, eliminating orphaned accounts, one of the most common audit exceptions.
  • Board-Ready Risk Reporting: Consolidates access, AI usage, and risk signals into a single dashboard for leadership and audit committee reporting.

Best for: Compliance, security, and IT teams at mid-market and enterprise organizations that need continuous evidence of access control across SaaS and AI, especially where AI adoption is outpacing formal governance.

Pros:

  • Evidence Without the Scramble: Access reviews run up to 80% faster, and every decision is logged automatically for auditors.
  • Measurable Risk Reduction: Customers see up to a 95% reduction in excessive privileges.
  • Covers AI Risk Natively: Governs AI apps, agents, and MCP servers that traditional GRC platforms don’t discover.
  • Strengthens Your Existing GRC Stack: Supplies the identity and access controls that policy-and-evidence platforms depend on.

Pricing: Custom pricing based on organization size and modules. A free trial is available.

‍

‍

B. ServiceNow Integrated Risk Management
‍

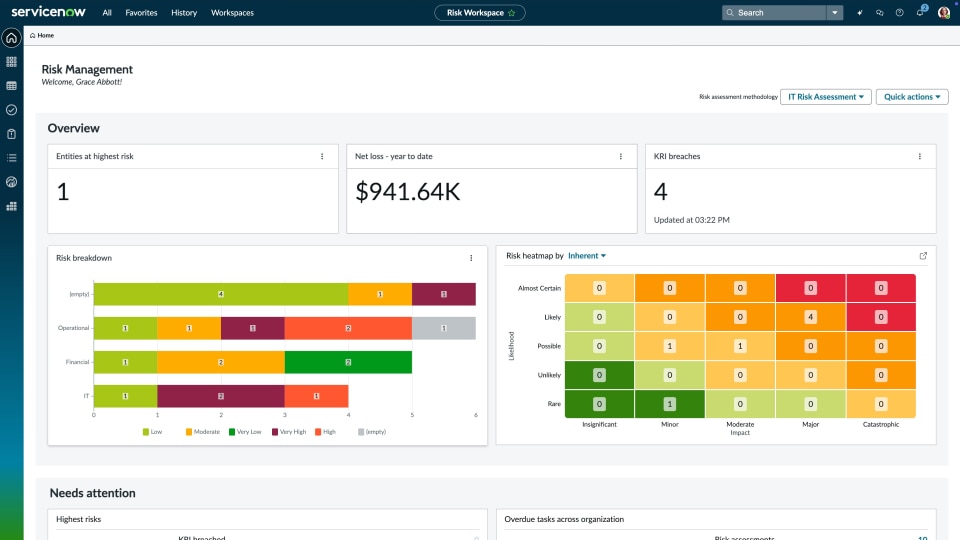
Integrated Risk Management - IRM - ServiceNow

‍

ServiceNow Integrated Risk Management (IRM) connects risk assessments, compliance activities, policy management, and issue remediation in one platform. It helps large organizations monitor controls, coordinate responses, and manage risk across business and IT teams.

Key features:

  • Enterprise Risk Management: Assess and monitor risks across business units.
  • Compliance Management: Map regulatory requirements to policies and controls.
  • Workflow Automation: Assign remediation tasks and track progress.
  • Audit Management: Centralize control evidence and compliance records.
  • Risk Reporting: Track risk exposure, control gaps, and remediation activities.

Pricing: Contact ServiceNow for a custom quote based on your organization's requirements.

C. Archer
‍

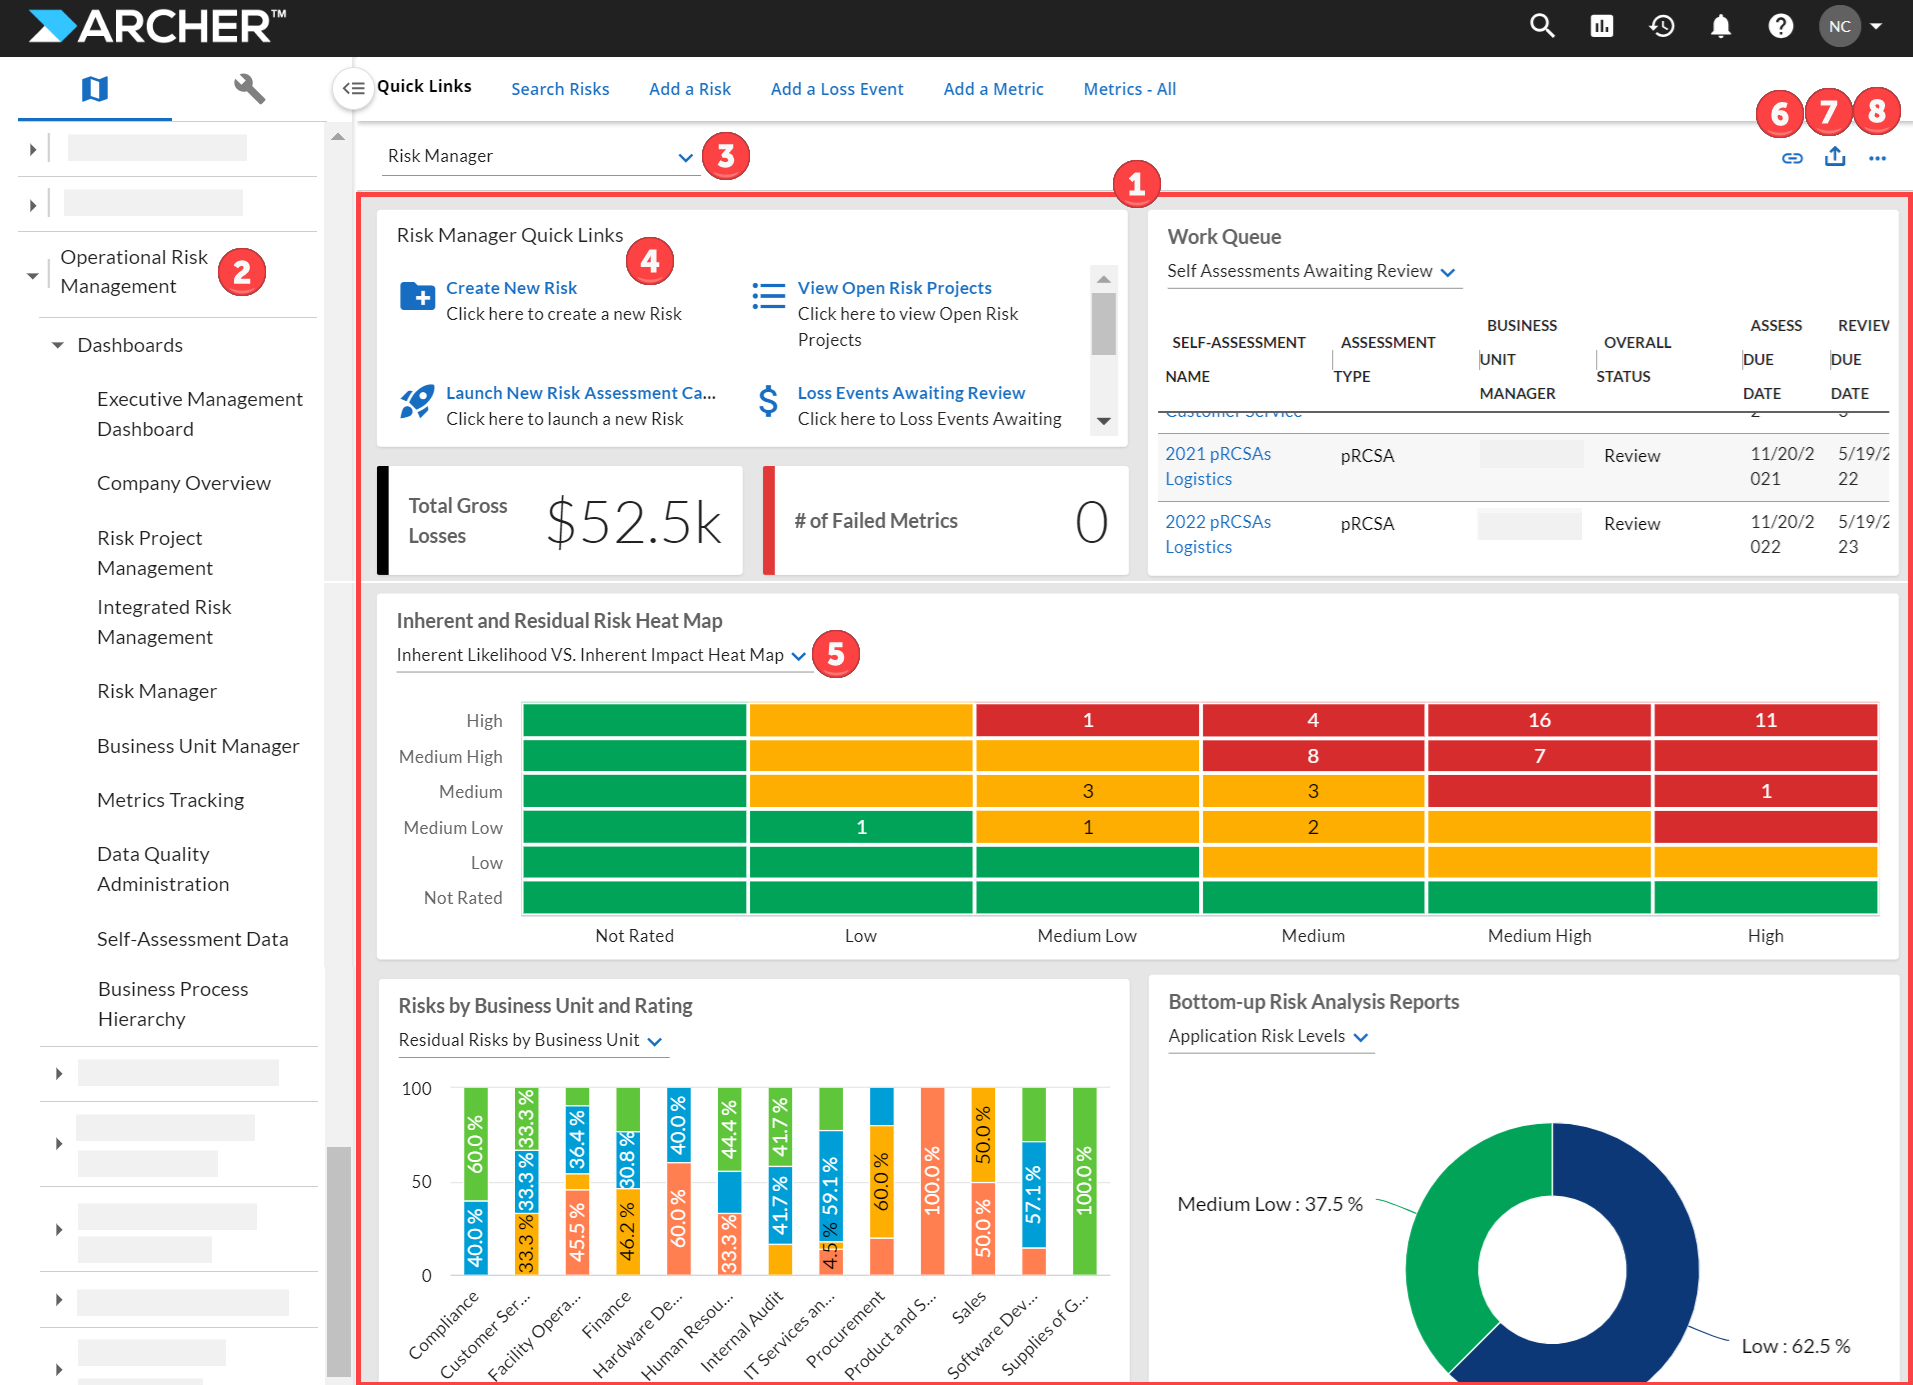
Dashboards: What do you need help with?

‍

Archer provides an integrated risk management platform for organizations managing complex risk and compliance programs. It connects risk assessments, internal controls, regulatory obligations, and remediation workflows across enterprise, operational, IT, and third-party risk management.

Key features:

  • Risk Assessments: Evaluate inherent and residual risks across business functions.
  • Control Management: Map risks to controls and monitor their effectiveness.
  • Regulatory Compliance: Track obligations and align them with policies and controls.
  • Third-Party Risk Management: Assess and monitor risks associated with external vendors.
  • Risk Reporting: Use dashboards to monitor exposure, issues, and remediation progress.

Pricing: Contact Archer for a custom quote based on the required products and deployment needs.

D. OneTrust
‍

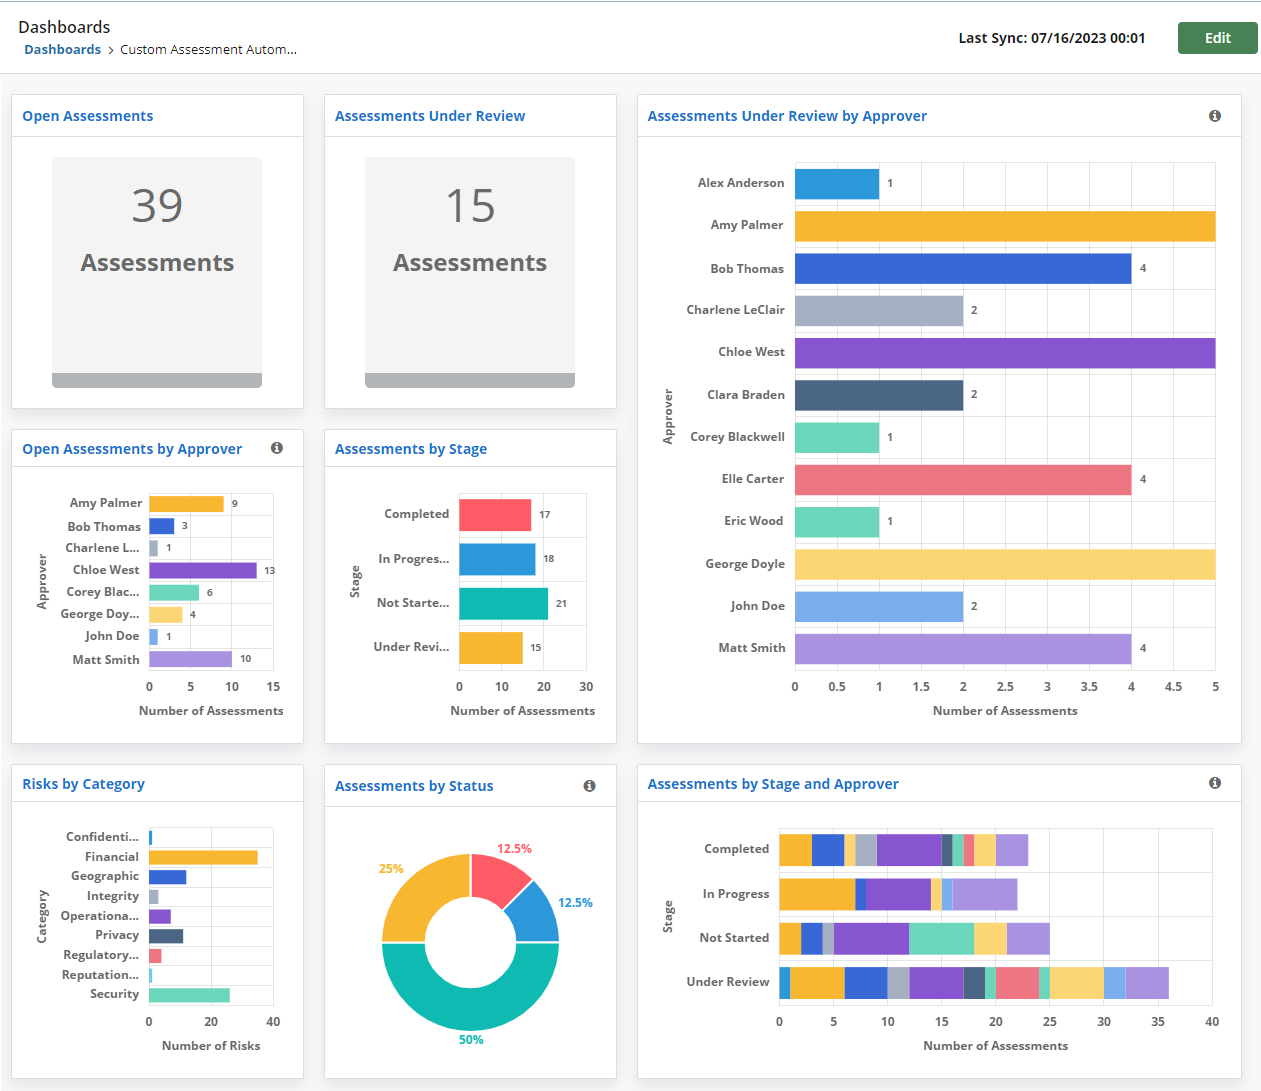
Viewing and Using Dashboards | MyOneTrust

‍

‍

OneTrust helps organizations manage privacy obligations, assess technology risks, and establish governance processes for AI systems. Its platform connects privacy, third-party risk, compliance, and AI governance workflows.

Key features:

  • Privacy Management: Support data protection and privacy compliance activities.
  • Risk and Compliance Management: Map requirements to controls and track remediation.
  • Third-Party Risk Management: Assess vendors and monitor associated risks.
  • AI Governance: Maintain AI inventories and assess AI-related risks.
  • Policy Management: Organize governance policies and support compliance workflows.

Pricing: Contact OneTrust for pricing based on the selected products and modules.

E. LogicGate Risk Cloud
‍

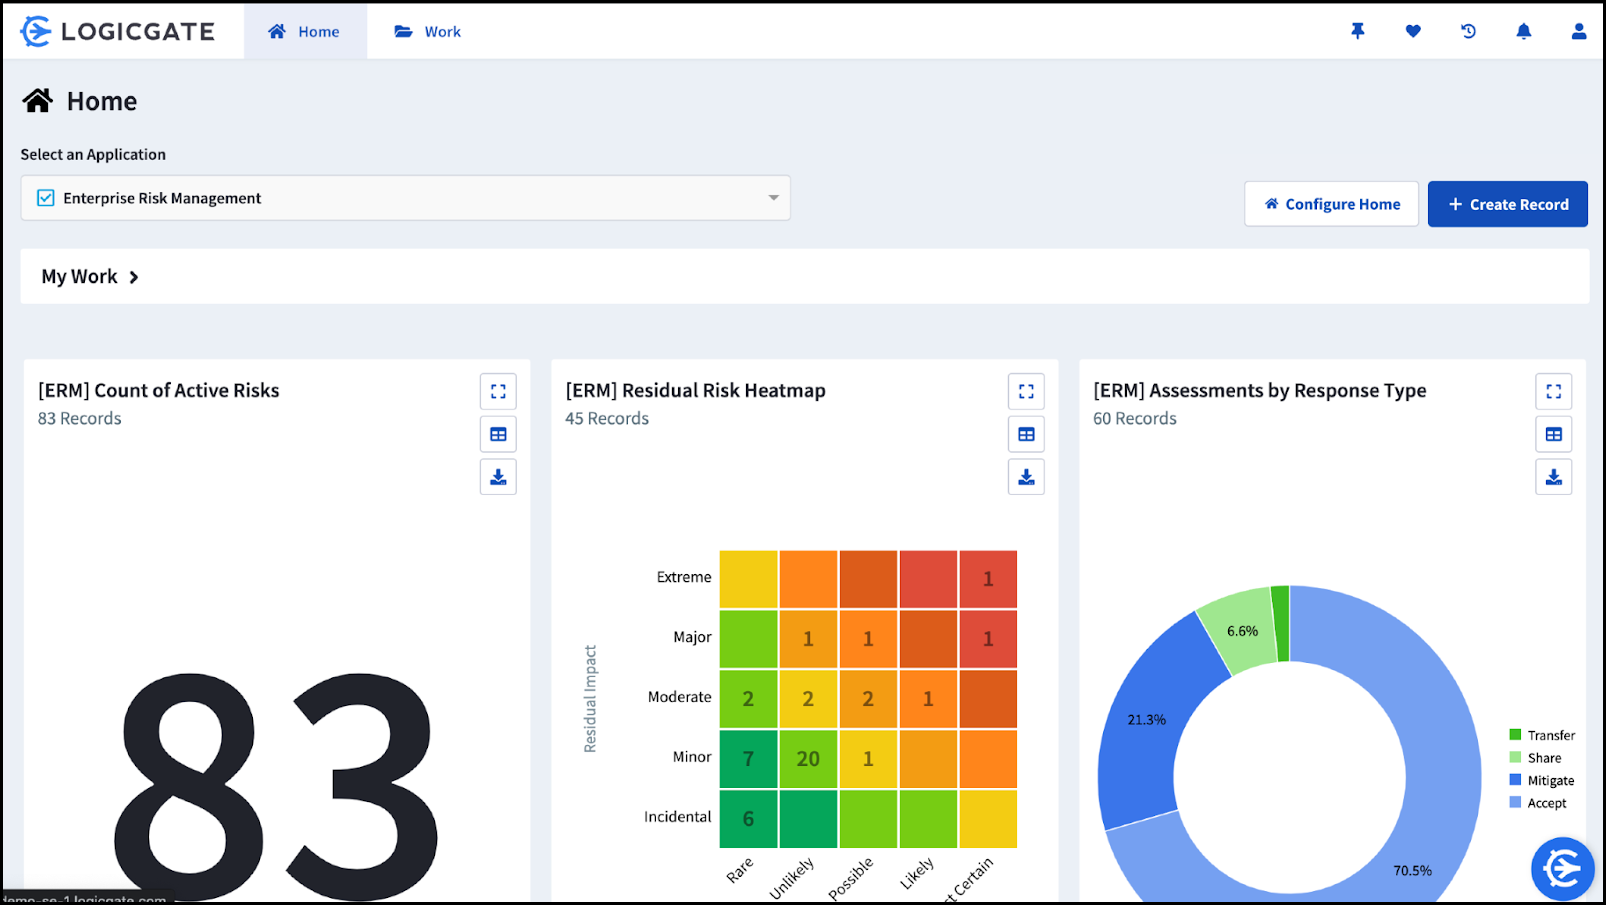
Access-Based Home Screens – LogicGate Help Center

‍

LogicGate Risk Cloud helps teams manage enterprise risk, compliance, audits, and third-party assessments through configurable applications. Its no-code platform connects risk data and automates workflows to accommodate changing business requirements.

Key features:

  • Risk Management: Centralize risk assessments and mitigation workflows.
  • Compliance Automation: Collect evidence and monitor controls across supported frameworks.
  • Workflow Customization: Adapt GRC processes without extensive custom coding.
  • Audit Management: Organize audit activities, findings, and remediation tasks.
  • AI-Powered Workflows: Use available AI capabilities to streamline selected GRC tasks.

Pricing: Contact LogicGate for a quote based on your organization's requirements and selected capabilities.

F. Optro (formerly AuditBoard)

‍

Optro Reporting & Dashboards | Optro

‍

Optro provides a platform for internal audit, enterprise risk management, information security, and compliance workflows. It helps organizations coordinate audit activities, manage controls, assess risks, and track remediation across governance processes.

Key features:

  • Internal Audit: Plan audits, document findings, and track remediation.
  • SOX and Controls Management: Coordinate control testing and documentation.
  • Enterprise Risk Management: Connect risk assessments with audit and compliance activities.
  • Information Security Management: Support oversight of security-related risks and controls.
  • Reporting and Analytics: Monitor findings, control gaps, and remediation progress.

Pricing: Contact Optro for current pricing based on the products and capabilities required.

G. MetricStream
‍

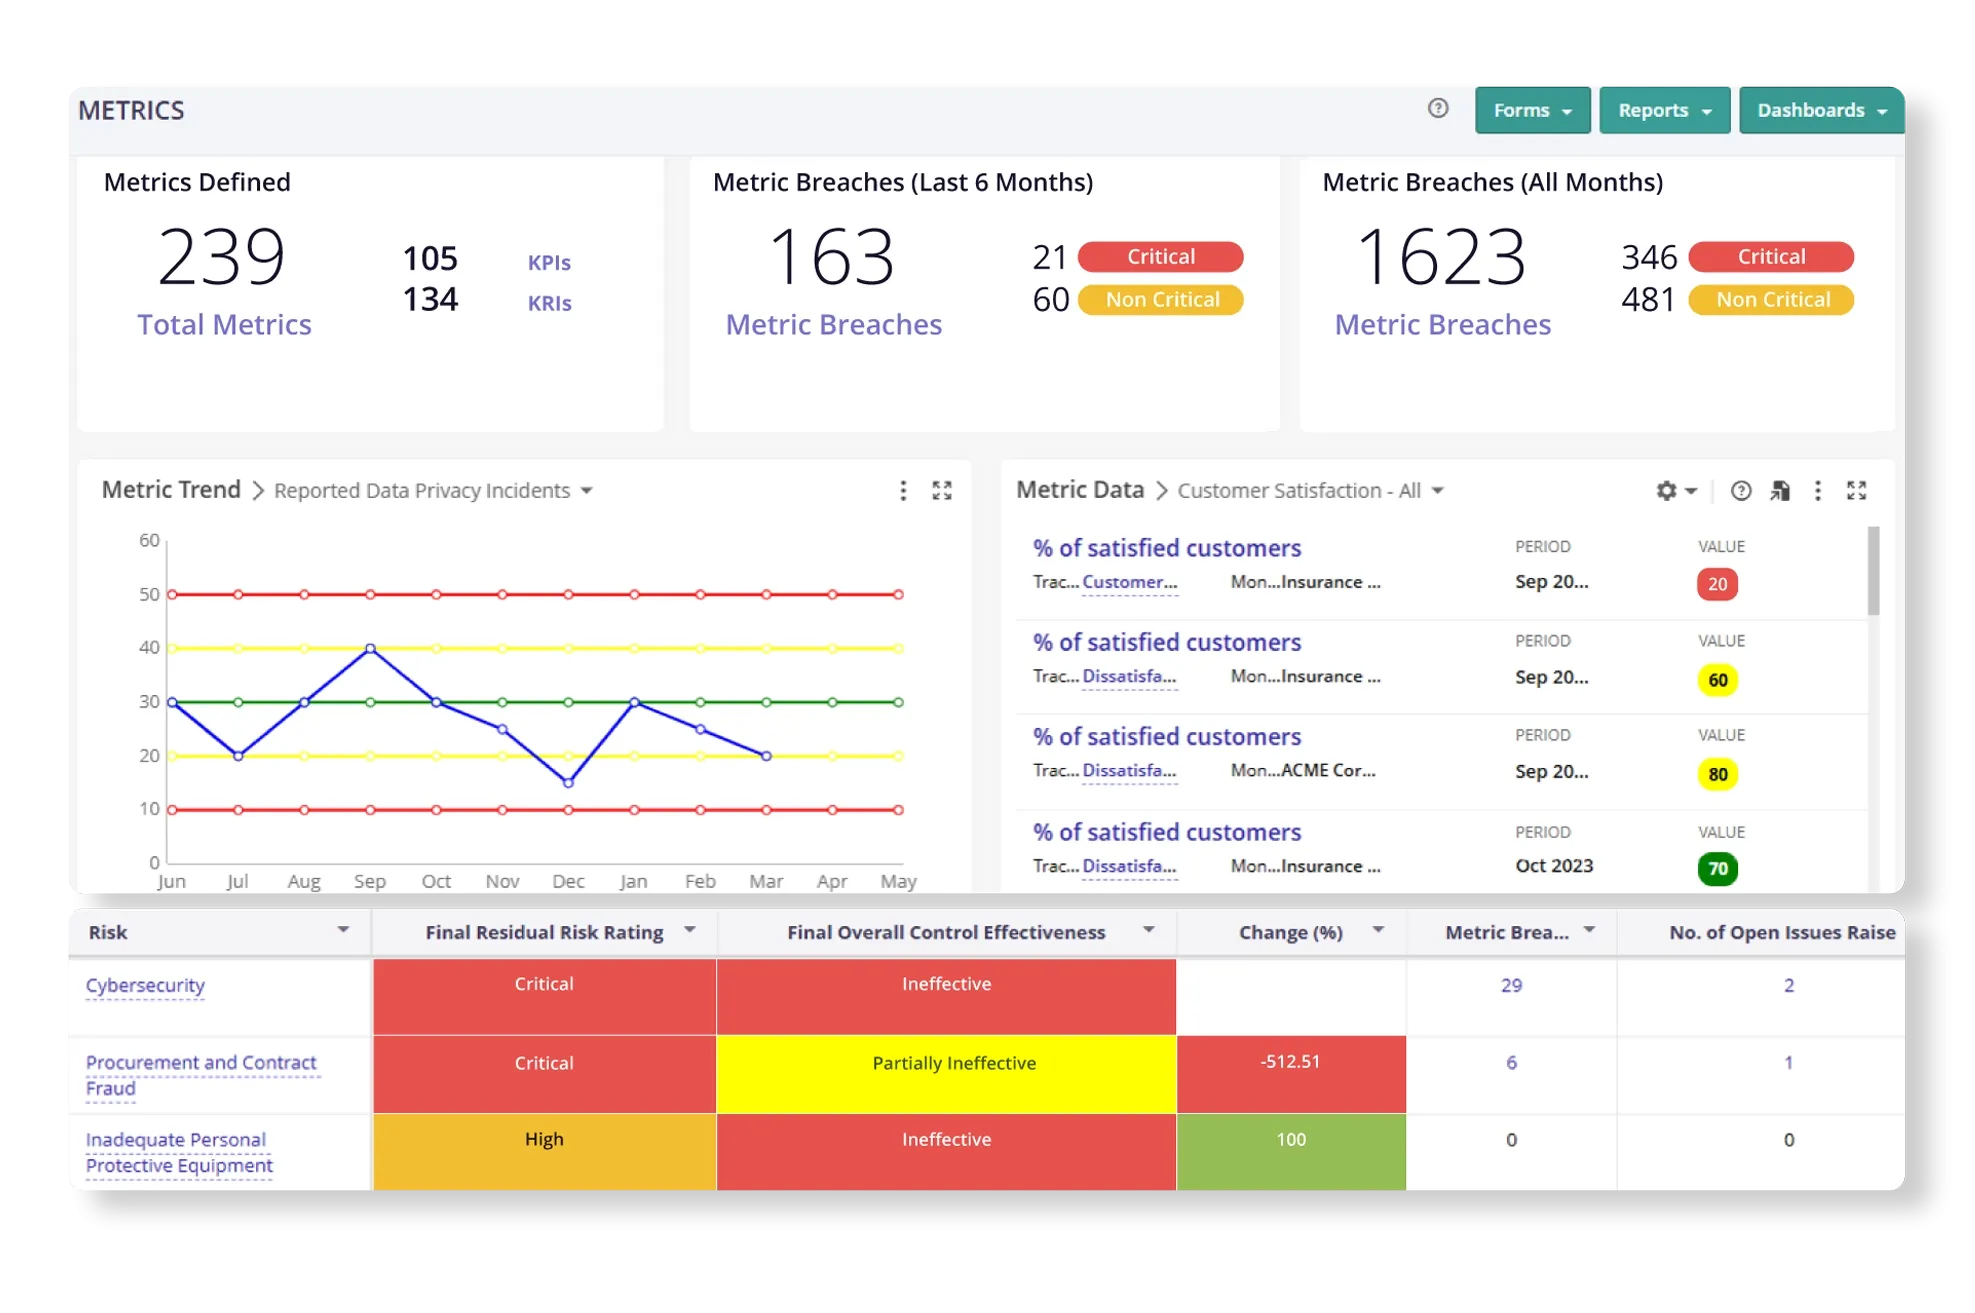
Key Metrics Monitoring and Reporting Software Solution | MetricStream

‍

MetricStream provides integrated governance, risk, and compliance software for organizations managing complex, enterprise-wide GRC programs. Its platform connects risk information across business functions to support consistent oversight, compliance management, and reporting.

Key features:

  • Enterprise Risk Management: Identify, assess, and monitor risks across business units.
  • Regulatory Compliance: Track obligations and align them with internal controls.
  • Audit Management: Coordinate audit planning, testing, and remediation.
  • Policy and Control Management: Organize policies and monitor control effectiveness.
  • Risk Reporting: Consolidate risk data to support management decisions.

Pricing: Contact MetricStream for a custom quote based on your organization's requirements.

H. Diligent One

‍

AI-Powered Third-Party Risk Triage | Diligent

‍

Diligent One brings governance, risk, compliance, and audit capabilities together to help organizations monitor risk exposure and support leadership decision-making. Its governance ecosystem connects risk reporting with board and executive oversight.

Key features:

  • Enterprise Risk Management: Assess risks and track mitigation activities.
  • Audit Management: Coordinate audit planning, findings, and remediation.
  • Board Reporting: Present risk information for executive and board oversight.
  • Compliance Workflows: Organize governance activities and monitor relevant obligations.
  • Risk Reporting: Consolidate risk information to improve visibility into organizational exposure.

Pricing: Contact Diligent for pricing based on the selected products and organizational needs.

I. Hyperproof
‍

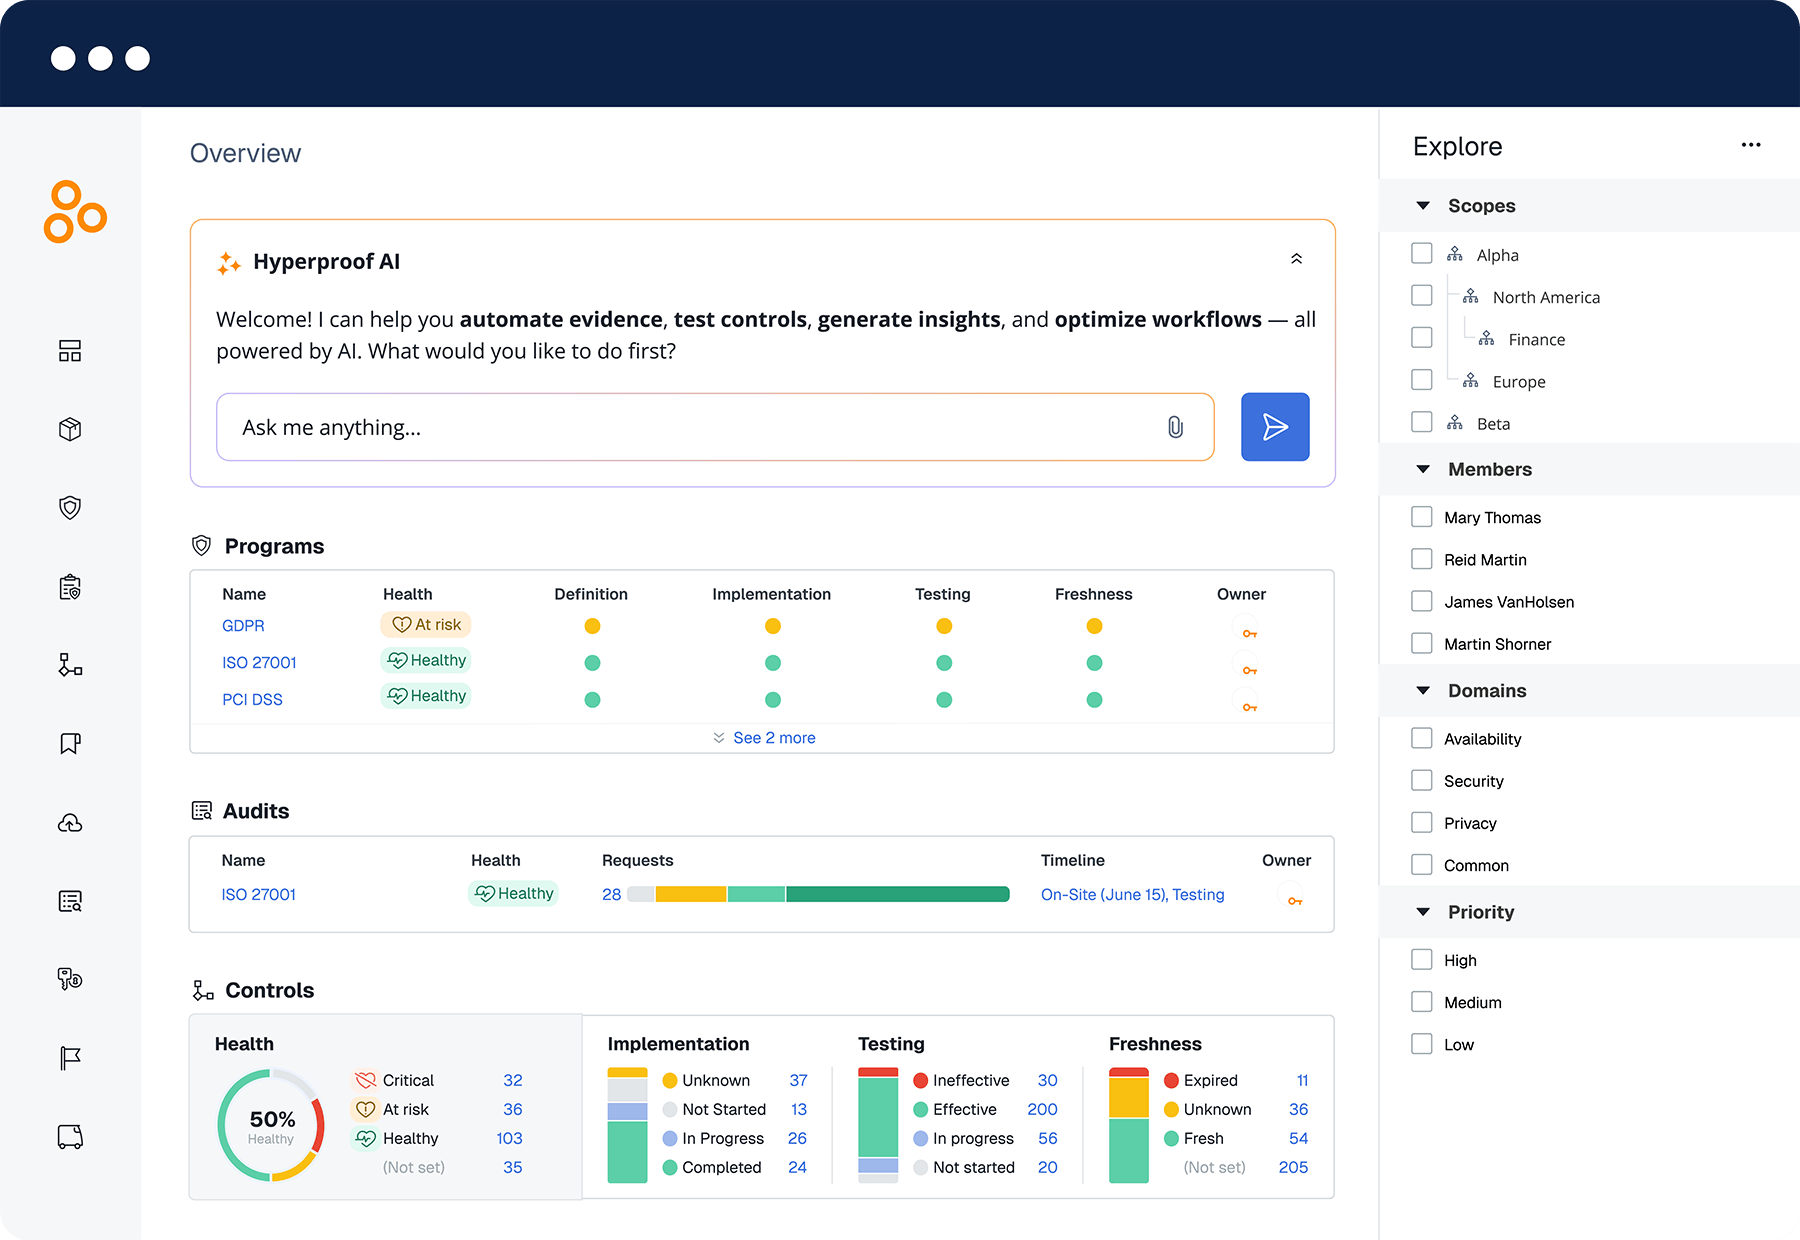
Hyperproof | The GRC Platform That Makes Compliance Easy

‍

Hyperproof helps security and compliance teams centralize compliance activities, organize audit evidence, map controls across frameworks, and track remediation tasks. Its compliance operations approach reduces duplicated work when organizations manage multiple compliance programs.

Key features:

  • Evidence Management: Organize compliance evidence and track collection.
  • Framework Mapping: Map shared controls across supported compliance frameworks.
  • Workflow Automation: Assign tasks, monitor progress, and coordinate audit preparation.
  • Risk Tracking: Connect compliance activities with risks and remediation workflows.
  • Compliance Reporting: Monitor control status and maintain visibility into compliance progress.

Pricing: Contact Hyperproof for current pricing based on your compliance requirements.

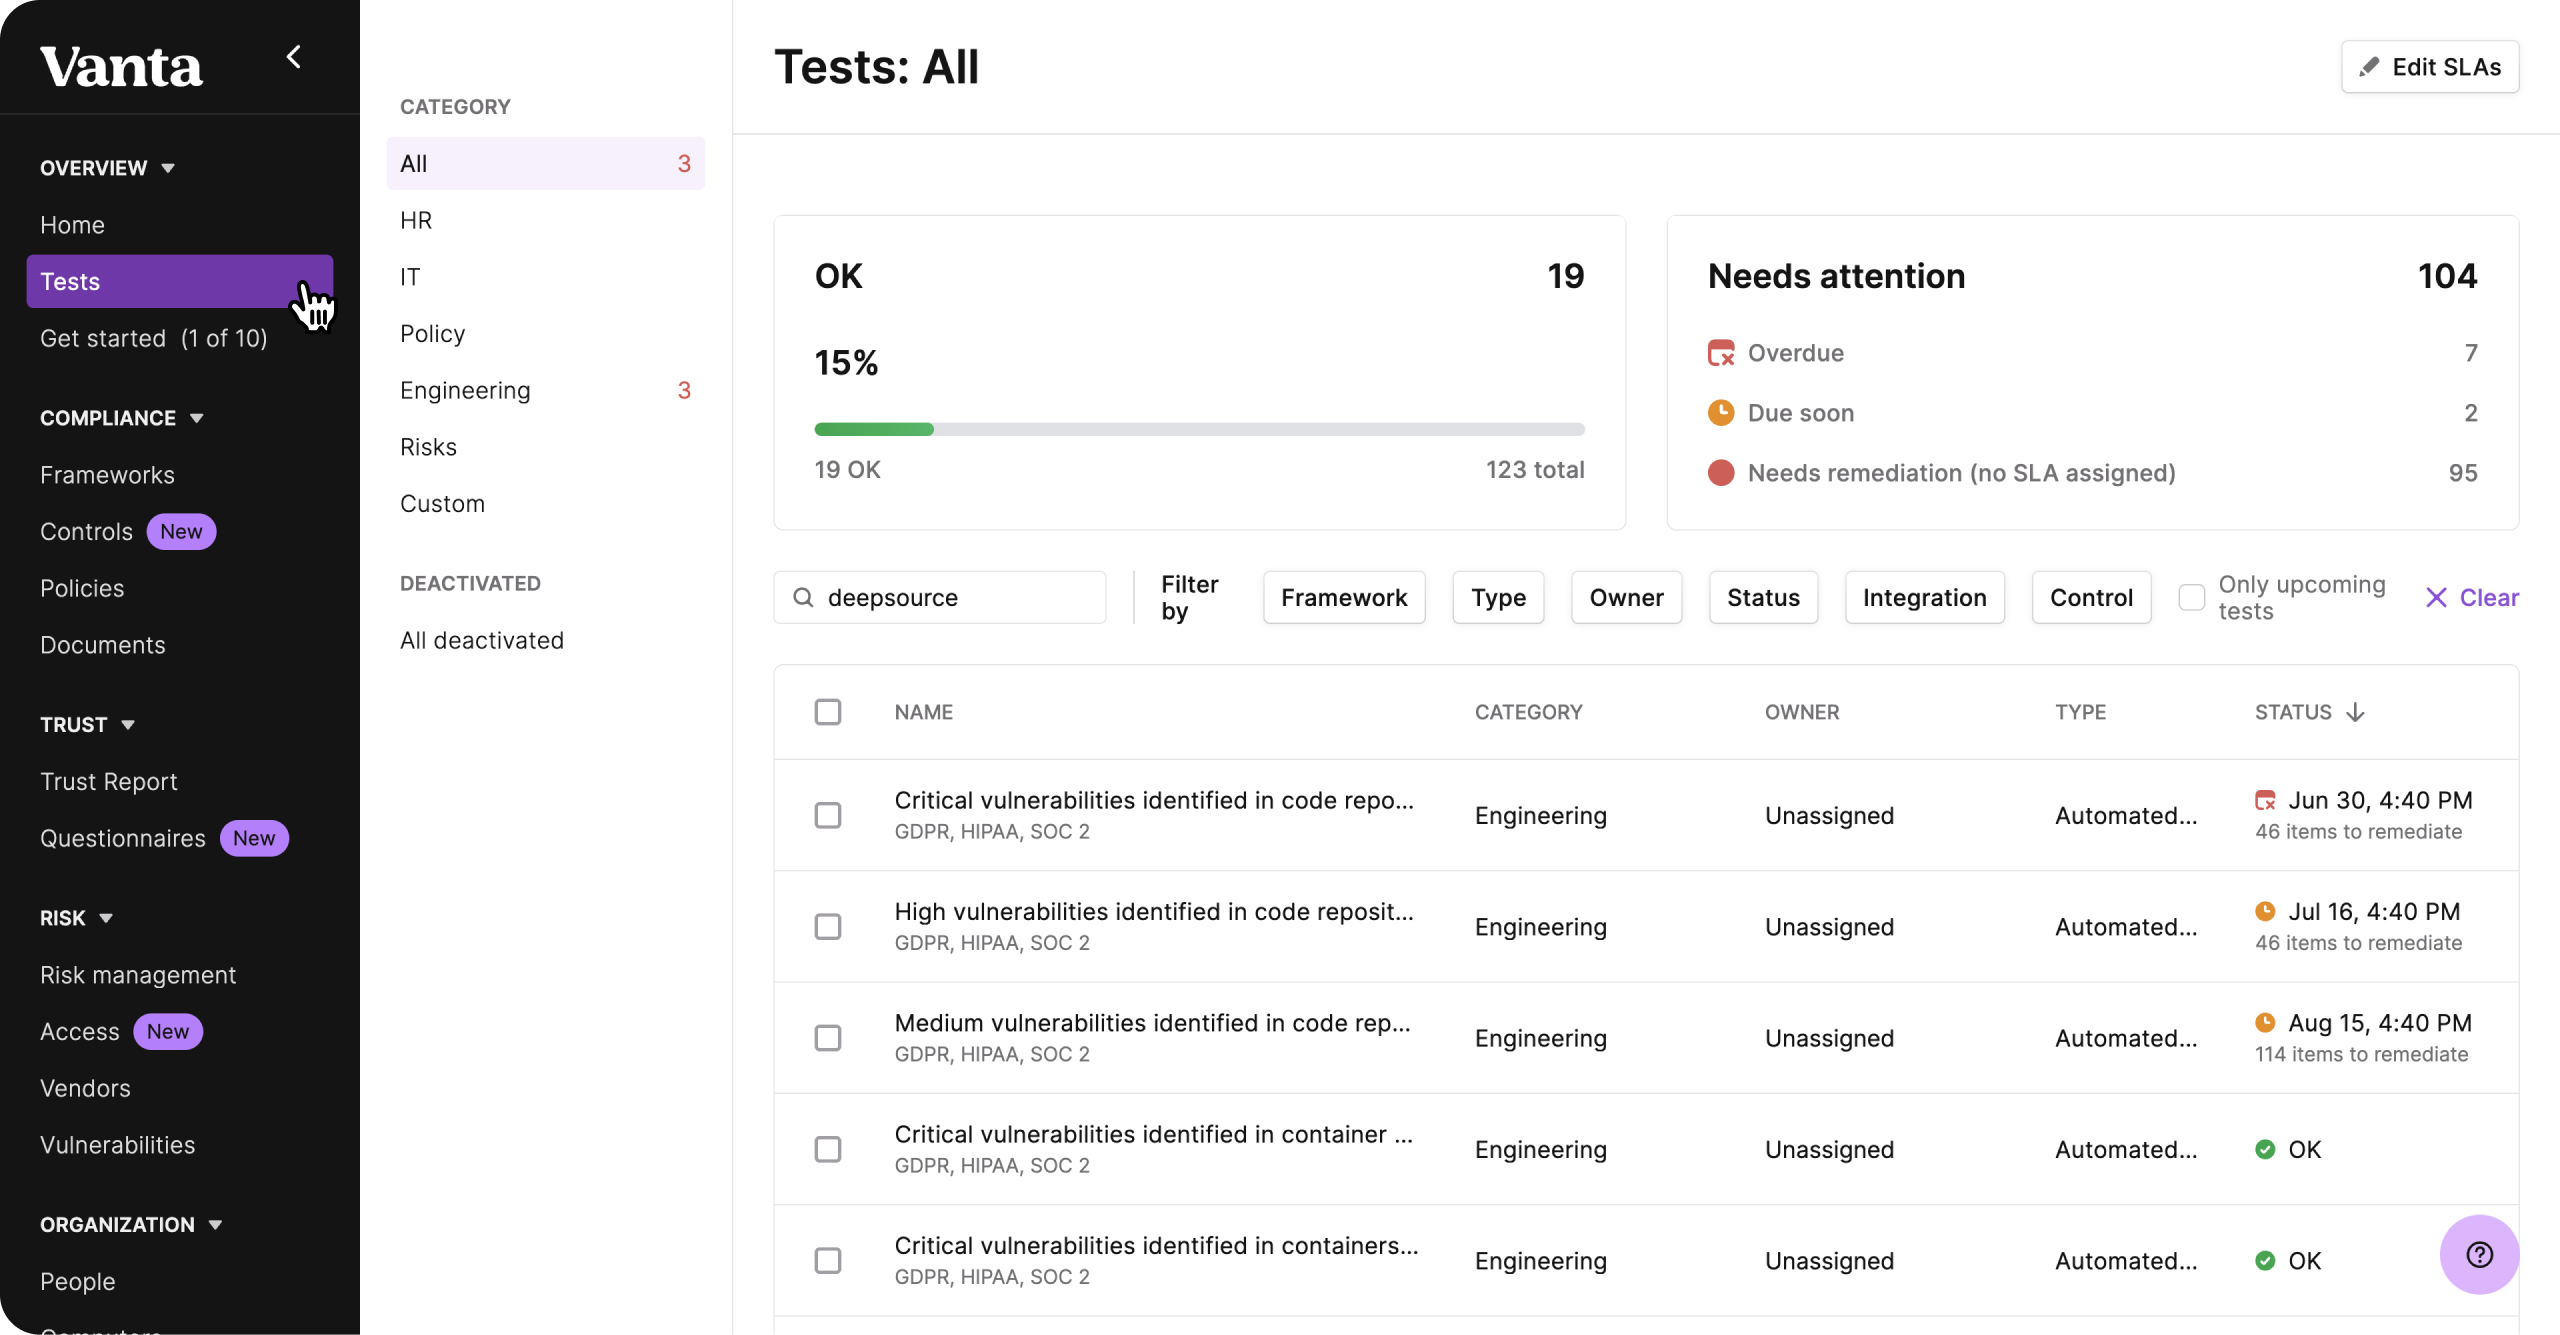
J. Vanta
‍

Vanta | DeepSource Docs

‍

Vanta helps businesses streamline security compliance by automating evidence collection, monitoring controls, and tracking requirements across supported frameworks. It is particularly useful for organizations that need to demonstrate security practices to customers and auditors while reducing manual work.

Key features:

  • Compliance Automation: Streamline workflows for supported frameworks such as SOC 2 and ISO 27001.
  • Evidence Collection: Gather evidence from connected systems to reduce manual effort.
  • Continuous Monitoring: Identify control issues and track remediation.
  • Risk Management: Support security risk assessments and related workflows.
  • Audit Readiness: Organize compliance activities to prepare for audits and customer reviews.

Pricing: Contact Vanta for a quote based on your organization's size, requirements, and selected products.

‍

4. How to Choose the Right GRC Platform

The right GRC platform should match your organization's risk exposure, compliance obligations, and existing technology stack. Evaluate these five factors before making a decision.

  • Compliance requirements: Confirm support for relevant frameworks, control mapping, and audit evidence.
  • Risk visibility: Check whether the platform connects risk assessments, control gaps, third-party risks, and remediation activities.
  • Integrations and automation: Assess connections with identity providers, cloud services, HR systems, and security tools.
  • Total cost of ownership: Consider licensing, migration, customization, training, and ongoing administration.
  • Governance gaps: Determine whether your core GRC platform covers your SaaS and AI governance needs or requires specialist tools.

Questions to Ask Before Buying

  • Does the platform support our required frameworks and risk workflows?
  • Which integrations and automation features are included?
  • What are the implementation costs and ongoing maintenance requirements?
  • Are additional tools needed for SaaS security or AI governance?

Compare vendors against the same requirements and prioritize capabilities that address measurable business needs.

‍

Hackers Need Just One Opening

Close the gaps they could exploit.
Secure Your Stack

‍

5. Why SaaS and AI Governance Matter When Choosing GRC Software

As organizations adopt more SaaS applications and AI tools, governance requires visibility into application usage, access permissions, and emerging technology risks. Unapproved tools and excessive privileges can create security and compliance gaps that are difficult to identify through policy documentation alone.

SaaS governance helps teams discover applications, review access, and identify potential security issues. AI governance adds oversight of AI tools, usage policies, and risks associated with AI systems and agents.

When comparing platforms, assess whether your GRC software provides this operational visibility or whether specialist tools are needed alongside it.

CloudEagle.ai supports this layer through its SaaS management, AI governance, identity governance, and SaaS security and compliance capabilities.

Choose the Right GRC Platform for Your Business

The right GRC platform should align with your risk management priorities, compliance requirements, and technology environment. While enterprise GRC suites support broad risk and audit workflows, organizations may also need specialized capabilities to govern SaaS applications, AI tools, and application access.

CloudEagle.ai helps organizations strengthen SaaS security, AI governance, and identity oversight alongside their broader governance strategy.

‍

6. FAQs

1. What is the difference between GRC and integrated risk management (IRM)?

GRC is the broader approach to aligning governance, risk management, and compliance, while integrated risk management (IRM) connects risk-related processes across an organization. Many modern GRC platforms incorporate IRM capabilities to link risk assessments, controls, compliance obligations, and reporting.

2. Can GRC software manage multiple compliance frameworks at once?

Yes, many GRC platforms support multiple frameworks, including SOC 2, ISO 27001, GDPR, and NIST standards. Cross-framework control mapping allows organizations to reuse relevant controls and evidence, reducing duplicated work across compliance programs.

3. How long does it take to implement GRC software?

Implementation can take weeks to several months, depending on the platform, number of frameworks, integration requirements, data migration, and workflow complexity. Defining requirements, assigning control owners, and preparing existing risk and compliance data can help reduce delays.

4. Can small businesses benefit from GRC software?

Yes, small businesses can use GRC software to organize compliance evidence, track risks, manage controls, and prepare for audits. Teams with straightforward certification requirements may prefer compliance automation tools, while businesses with broader risk management needs may benefit from a more comprehensive GRC platform.

5. What features should businesses look for in a GRC platform?

Businesses should prioritize risk assessment, policy management, control monitoring, audit workflows, compliance evidence collection, and integrations with existing systems. Organizations adopting SaaS applications and AI tools should also evaluate SaaS visibility, access governance, and AI risk management capabilities to address emerging security and compliance risks.

‍

Advertisement for a SaaS Subscription Tracking Template with a call-to-action button to download and a partial graphic of a tablet showing charts.Banner promoting a SaaS Agreement Checklist to streamline SaaS management and avoid budget waste with a call-to-action button labeled Download checklist.Blue banner with text 'The Ultimate Employee Offboarding Checklist!' and a black button labeled 'Download checklist' alongside partial views of checklist documents from cloudeagle.ai.Digital ad for download checklist titled 'The Ultimate Checklist for IT Leaders to Optimize SaaS Operations' by cloudeagle.ai, showing checklist pages.Slack Buyer's Guide offer with text 'Unlock insider insights to get the best deal on Slack!' and a button labeled 'Get Your Copy', accompanied by a preview of the guide featuring Slack's logo.Monday Pricing Guide by cloudeagle.ai offering exclusive pricing secrets to maximize investment with a call-to-action button labeled Get Your Copy and an image of the guide's cover.Blue banner for Canva Pricing Guide by cloudeagle.ai offering a guide to Canva costs, features, and alternatives with a call-to-action button saying Get Your Copy.Blue banner with white text reading 'Little-Known Negotiation Hacks to Get the Best Deal on Slack' and a white button labeled 'Get Your Copy'.Blue banner with text 'Little-Known Negotiation Hacks to Get the Best Deal on Monday.com' and a white button labeled 'Get Your Copy'.Blue banner with text 'Little-Known Negotiation Hacks to Get the Best Deal on Canva' and a white button labeled 'Get Your Copy'.Banner with text 'Slack Buyer's Guide' and a 'Download Now' button next to images of a guide titled 'Slack Buyer’s Guide: Features, Pricing & Best Practices'.Digital cover of Monday Pricing Guide with a button labeled Get Your Copy on a blue background.Canva Pricing Guide cover with a button labeled Get Your Copy on a blue gradient background.

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.
License Count
Benchmark
Per User/Per Year

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.
License Count
Benchmark
Per User/Per Year

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.
Notion Plus
License Count
Benchmark
Per User/Per Year
100-500
$67.20 - $78.72
500-1000
$59.52 - $72.00
1000+
$51.84 - $57.60
Canva Pro
License Count
Benchmark
Per User/Per Year
100-500
$74.33-$88.71
500-1000
$64.74-$80.32
1000+
$55.14-$62.34

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.
Zoom Business
License Count
Benchmark
Per User/Per Year
100-500
$216.00 - $264.00
500-1000
$180.00 - $216.00
1000+
$156.00 - $180.00

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.

Get the Right Security Platform To Secure Your Cloud Infrastructure

Please enter a business email
Thank you!
The 2023 SaaS report has been sent to your email. Check your promotional or spam folder.
Oops! Something went wrong while submitting the form.

Access full report

Please enter a business email
Thank you!
The 2023 SaaS report has been sent to your email. Check your promotional or spam folder.
Oops! Something went wrong while submitting the form.
  • GRC platforms help organizations manage risk, compliance, audits, and internal controls.
  • The right platform depends on business size, compliance needs, integrations, and implementation costs.
  • Enterprise GRC tools support broad risk management, while specialist platforms focus on compliance automation, SaaS security, or AI governance.
  • CloudEagle.ai strengthens SaaS and AI governance through application discovery, access governance, and SaaS security and compliance

‍

Managing governance, risk, and compliance is becoming more complex as businesses adopt AI tools, expand their SaaS environments, and face evolving regulatory requirements. According to the World Economic Forum's Global Cybersecurity Outlook 2026, 87% of surveyed organizations identified AI-related vulnerabilities as the fastest-growing cyber risk during 2025.

The right governance, risk, and compliance (GRC) platform helps organizations manage risks, streamline audits, monitor controls, and maintain compliance. However, capabilities vary across enterprise GRC suites, compliance automation tools, and specialist governance solutions.

This guide compares the 10 best GRC platforms in 2026, starting with CloudEagle.ai, to help businesses evaluate their options based on features, integrations, scalability, and pricing considerations.

‍

1. What is GRC Platform?

Governance, risk, and compliance (GRC) software helps organizations manage business risks, internal policies, and regulatory requirements through a centralized platform. It streamlines risk assessments, audit management, control monitoring, and compliance reporting.

Most GRC platforms support frameworks such as SOC 2, ISO 27001, and GDPR. While enterprise GRC software covers broader risk and governance processes, compliance automation tools focus on tasks such as evidence collection and control monitoring. 

Organizations managing growing SaaS environments and AI adoption may also need dedicated capabilities for SaaS security, access governance, and AI risk management.

‍

Compliant on Paper. Exposed in Practice?

Find the gaps before auditors do
Find Out

‍

2. How We Evaluated the Best GRC Platforms

We compared the platforms based on their publicly documented capabilities, primary use cases, integration considerations, scalability, and pricing availability. The goal is to help buyers identify a suitable shortlist, not to replace product demonstrations or hands-on evaluation.

The comparison considers six criteria:

  • Risk and compliance management: Risk assessments, policy management, control mapping, and regulatory framework support.
  • Audit and evidence management: Audit workflows, evidence collection, control testing, and remediation tracking.
  • Automation and integrations: Connections with identity providers, cloud services, HR systems, and security tools.
  • SaaS and AI governance: Application visibility, access governance, and AI risk oversight where supported.
  • Scalability and usability: Configuration requirements, administrative effort, and suitability for different organizational needs.
  • Pricing and implementation: Pricing availability, licensing considerations, deployment complexity, and ongoing maintenance.

The platforms are presented according to their primary use cases, recognizing that full-suite GRC platforms and specialist governance tools do not offer identical capabilities.

3. 10 Best GRC Platforms in 2026

The best GRC platform depends on whether an organization needs enterprise-wide risk management, automated compliance workflows, audit management, or stronger governance across SaaS applications and AI tools. 

This list includes both full-suite GRC platforms and specialist governance solutions. The ranking is an editorial selection, not a claim that every platform offers the same capabilities. The right choice depends on your organization's risk management, compliance, and operational governance requirements.

‍

Platform Best for
CloudEagle.ai SaaS security, AI governance, and identity oversight
ServiceNow IRM Connected risk and business workflows
Archer Configurable, organization-wide risk management
OneTrust Privacy, third-party risk, and AI governance
LogicGate Risk Cloud Adaptable risk and compliance workflows
Optro Internal audit, SOX, and broader GRC processes
MetricStream Complex risk and compliance programs
Diligent One Board oversight and enterprise risk reporting
Hyperproof Evidence management and multiple frameworks
Vanta Automated evidence collection and control monitoring

‍

A. CloudEagle.ai

‍

‍

CloudEagle.ai helps GRC teams govern the fastest-growing source of compliance risk: access across SaaS apps, AI tools, and non-human identities.

Instead of collecting evidence once a quarter, compliance and security teams get continuous control monitoring over who can access what, risk scores for every unsanctioned app and AI tool, and automated access reviews that produce audit-ready evidence for SOC 2, SOX, HIPAA, PCI DSS, ISO 27001, and GDPR.

It also extends governance to AI, enforcing usage policy and documenting decisions so AI adoption doesn’t become an audit finding.

CloudEagle.ai is named in the 2026 Gartner Market Guide for IGA and recognized as a Product Leader in KuppingerCole’s 2026 Leadership Compass for SaaS Security and AI Governance.

Key features:

  • Audit-Ready Access Reviews: Automates access reviews across every connected app and logs each certification, revocation, and approval as evidence for SOC 2, SOX, and ISO 27001 audits.
  • Continuous Access Control Monitoring: Monitors risky activity across SaaS and AI apps around the clock and automatically removes excessive privileges, so controls hold between audits, not just during them.
  • Shadow IT and Shadow AI Risk Scoring: Discovers apps adopted outside IT and SSO and assigns each a risk score, giving risk teams a complete, prioritized inventory of third-party exposure.
  • AI Governance and Policy Enforcement: Enforces AI usage policy inside the browser, requires approval for new AI tools, and flags sensitive data shared with public AI services, supporting frameworks like ISO 42001 and the EU AI Act.
  • Non-Human Identity Governance: Tracks AI agents, service accounts, and API keys, including what each can access, closing a blind spot most identity audits miss.
  • Joiner-Mover-Leaver Controls: Revokes all access at offboarding with a complete audit trail, eliminating orphaned accounts, one of the most common audit exceptions.
  • Board-Ready Risk Reporting: Consolidates access, AI usage, and risk signals into a single dashboard for leadership and audit committee reporting.

Best for: Compliance, security, and IT teams at mid-market and enterprise organizations that need continuous evidence of access control across SaaS and AI, especially where AI adoption is outpacing formal governance.

Pros:

  • Evidence Without the Scramble: Access reviews run up to 80% faster, and every decision is logged automatically for auditors.
  • Measurable Risk Reduction: Customers see up to a 95% reduction in excessive privileges.
  • Covers AI Risk Natively: Governs AI apps, agents, and MCP servers that traditional GRC platforms don’t discover.
  • Strengthens Your Existing GRC Stack: Supplies the identity and access controls that policy-and-evidence platforms depend on.

Pricing: Custom pricing based on organization size and modules. A free trial is available.

‍

‍

B. ServiceNow Integrated Risk Management

‍

Integrated Risk Management - IRM - ServiceNow

‍

ServiceNow Integrated Risk Management (IRM) connects risk assessments, compliance activities, policy management, and issue remediation in one platform. It helps large organizations monitor controls, coordinate responses, and manage risk across business and IT teams.

Key features:

  • Enterprise Risk Management: Assess and monitor risks across business units.
  • Compliance Management: Map regulatory requirements to policies and controls.
  • Workflow Automation: Assign remediation tasks and track progress.
  • Audit Management: Centralize control evidence and compliance records.
  • Risk Reporting: Track risk exposure, control gaps, and remediation activities.

Pricing: Contact ServiceNow for a custom quote based on your organization's requirements.

C. Archer

‍

Dashboards: What do you need help with?

‍

Archer provides an integrated risk management platform for organizations managing complex risk and compliance programs. It connects risk assessments, internal controls, regulatory obligations, and remediation workflows across enterprise, operational, IT, and third-party risk management.

Key features:

  • Risk Assessments: Evaluate inherent and residual risks across business functions.
  • Control Management: Map risks to controls and monitor their effectiveness.
  • Regulatory Compliance: Track obligations and align them with policies and controls.
  • Third-Party Risk Management: Assess and monitor risks associated with external vendors.
  • Risk Reporting: Use dashboards to monitor exposure, issues, and remediation progress.

Pricing: Contact Archer for a custom quote based on the required products and deployment needs.

D. OneTrust

‍

Viewing and Using Dashboards | MyOneTrust

‍

‍

OneTrust helps organizations manage privacy obligations, assess technology risks, and establish governance processes for AI systems. Its platform connects privacy, third-party risk, compliance, and AI governance workflows.

Key features:

  • Privacy Management: Support data protection and privacy compliance activities.
  • Risk and Compliance Management: Map requirements to controls and track remediation.
  • Third-Party Risk Management: Assess vendors and monitor associated risks.
  • AI Governance: Maintain AI inventories and assess AI-related risks.
  • Policy Management: Organize governance policies and support compliance workflows.

Pricing: Contact OneTrust for pricing based on the selected products and modules.

E. LogicGate Risk Cloud

‍

Access-Based Home Screens – LogicGate Help Center

‍

LogicGate Risk Cloud helps teams manage enterprise risk, compliance, audits, and third-party assessments through configurable applications. Its no-code platform connects risk data and automates workflows to accommodate changing business requirements.

Key features:

  • Risk Management: Centralize risk assessments and mitigation workflows.
  • Compliance Automation: Collect evidence and monitor controls across supported frameworks.
  • Workflow Customization: Adapt GRC processes without extensive custom coding.
  • Audit Management: Organize audit activities, findings, and remediation tasks.
  • AI-Powered Workflows: Use available AI capabilities to streamline selected GRC tasks.

Pricing: Contact LogicGate for a quote based on your organization's requirements and selected capabilities.

F. Optro (formerly AuditBoard)

‍

Optro Reporting & Dashboards | Optro

‍

Optro provides a platform for internal audit, enterprise risk management, information security, and compliance workflows. It helps organizations coordinate audit activities, manage controls, assess risks, and track remediation across governance processes.

Key features:

  • Internal Audit: Plan audits, document findings, and track remediation.
  • SOX and Controls Management: Coordinate control testing and documentation.
  • Enterprise Risk Management: Connect risk assessments with audit and compliance activities.
  • Information Security Management: Support oversight of security-related risks and controls.
  • Reporting and Analytics: Monitor findings, control gaps, and remediation progress.

Pricing: Contact Optro for current pricing based on the products and capabilities required.

G. MetricStream

‍

Key Metrics Monitoring and Reporting Software Solution | MetricStream

‍

MetricStream provides integrated governance, risk, and compliance software for organizations managing complex, enterprise-wide GRC programs. Its platform connects risk information across business functions to support consistent oversight, compliance management, and reporting.

Key features:

  • Enterprise Risk Management: Identify, assess, and monitor risks across business units.
  • Regulatory Compliance: Track obligations and align them with internal controls.
  • Audit Management: Coordinate audit planning, testing, and remediation.
  • Policy and Control Management: Organize policies and monitor control effectiveness.
  • Risk Reporting: Consolidate risk data to support management decisions.

Pricing: Contact MetricStream for a custom quote based on your organization's requirements.

H. Diligent One

‍

AI-Powered Third-Party Risk Triage | Diligent

‍

Diligent One brings governance, risk, compliance, and audit capabilities together to help organizations monitor risk exposure and support leadership decision-making. Its governance ecosystem connects risk reporting with board and executive oversight.

Key features:

  • Enterprise Risk Management: Assess risks and track mitigation activities.
  • Audit Management: Coordinate audit planning, findings, and remediation.
  • Board Reporting: Present risk information for executive and board oversight.
  • Compliance Workflows: Organize governance activities and monitor relevant obligations.
  • Risk Reporting: Consolidate risk information to improve visibility into organizational exposure.

Pricing: Contact Diligent for pricing based on the selected products and organizational needs.

I. Hyperproof

‍

Hyperproof | The GRC Platform That Makes Compliance Easy

‍

Hyperproof helps security and compliance teams centralize compliance activities, organize audit evidence, map controls across frameworks, and track remediation tasks. Its compliance operations approach reduces duplicated work when organizations manage multiple compliance programs.

Key features:

  • Evidence Management: Organize compliance evidence and track collection.
  • Framework Mapping: Map shared controls across supported compliance frameworks.
  • Workflow Automation: Assign tasks, monitor progress, and coordinate audit preparation.
  • Risk Tracking: Connect compliance activities with risks and remediation workflows.
  • Compliance Reporting: Monitor control status and maintain visibility into compliance progress.

Pricing: Contact Hyperproof for current pricing based on your compliance requirements.

J. Vanta

‍

Vanta | DeepSource Docs

‍

Vanta helps businesses streamline security compliance by automating evidence collection, monitoring controls, and tracking requirements across supported frameworks. It is particularly useful for organizations that need to demonstrate security practices to customers and auditors while reducing manual work.

Key features:

  • Compliance Automation: Streamline workflows for supported frameworks such as SOC 2 and ISO 27001.
  • Evidence Collection: Gather evidence from connected systems to reduce manual effort.
  • Continuous Monitoring: Identify control issues and track remediation.
  • Risk Management: Support security risk assessments and related workflows.
  • Audit Readiness: Organize compliance activities to prepare for audits and customer reviews.

Pricing: Contact Vanta for a quote based on your organization's size, requirements, and selected products.

‍

4. How to Choose the Right GRC Platform

The right GRC platform should match your organization's risk exposure, compliance obligations, and existing technology stack. Evaluate these five factors before making a decision.

  • Compliance requirements: Confirm support for relevant frameworks, control mapping, and audit evidence.
  • Risk visibility: Check whether the platform connects risk assessments, control gaps, third-party risks, and remediation activities.
  • Integrations and automation: Assess connections with identity providers, cloud services, HR systems, and security tools.
  • Total cost of ownership: Consider licensing, migration, customization, training, and ongoing administration.
  • Governance gaps: Determine whether your core GRC platform covers your SaaS and AI governance needs or requires specialist tools.

Questions to Ask Before Buying

  • Does the platform support our required frameworks and risk workflows?
  • Which integrations and automation features are included?
  • What are the implementation costs and ongoing maintenance requirements?
  • Are additional tools needed for SaaS security or AI governance?

Compare vendors against the same requirements and prioritize capabilities that address measurable business needs.

‍

Hackers Need Just One Opening

Close the gaps they could exploit.
Secure Your Stack

‍

5. Why SaaS and AI Governance Matter When Choosing GRC Software

As organizations adopt more SaaS applications and AI tools, governance requires visibility into application usage, access permissions, and emerging technology risks. Unapproved tools and excessive privileges can create security and compliance gaps that are difficult to identify through policy documentation alone.

SaaS governance helps teams discover applications, review access, and identify potential security issues. AI governance adds oversight of AI tools, usage policies, and risks associated with AI systems and agents.

When comparing platforms, assess whether your GRC software provides this operational visibility or whether specialist tools are needed alongside it.

CloudEagle.ai supports this layer through its SaaS management, AI governance, identity governance, and SaaS security and compliance capabilities.

Choose the Right GRC Platform for Your Business

The right GRC platform should align with your risk management priorities, compliance requirements, and technology environment. While enterprise GRC suites support broad risk and audit workflows, organizations may also need specialized capabilities to govern SaaS applications, AI tools, and application access.

CloudEagle.ai helps organizations strengthen SaaS security, AI governance, and identity oversight alongside their broader governance strategy.

‍

6. FAQs

1. What is the difference between GRC and integrated risk management (IRM)?

GRC is the broader approach to aligning governance, risk management, and compliance, while integrated risk management (IRM) connects risk-related processes across an organization. Many modern GRC platforms incorporate IRM capabilities to link risk assessments, controls, compliance obligations, and reporting.

2. Can GRC software manage multiple compliance frameworks at once?

Yes, many GRC platforms support multiple frameworks, including SOC 2, ISO 27001, GDPR, and NIST standards. Cross-framework control mapping allows organizations to reuse relevant controls and evidence, reducing duplicated work across compliance programs.

3. How long does it take to implement GRC software?

Implementation can take weeks to several months, depending on the platform, number of frameworks, integration requirements, data migration, and workflow complexity. Defining requirements, assigning control owners, and preparing existing risk and compliance data can help reduce delays.

4. Can small businesses benefit from GRC software?

Yes, small businesses can use GRC software to organize compliance evidence, track risks, manage controls, and prepare for audits. Teams with straightforward certification requirements may prefer compliance automation tools, while businesses with broader risk management needs may benefit from a more comprehensive GRC platform.

5. What features should businesses look for in a GRC platform?

Businesses should prioritize risk assessment, policy management, control monitoring, audit workflows, compliance evidence collection, and integrations with existing systems. Organizations adopting SaaS applications and AI tools should also evaluate SaaS visibility, access governance, and AI risk management capabilities to address emerging security and compliance risks.

‍

CloudEagle.ai recognized in the 2025 Gartner® Magic Quadrant™ for SaaS Management Platforms
Download now
gartner chart
5x
Faster employee
onboarding
80%
Reduction in time for
user access reviews
30k
Workflows
automated
$15Bn
Analyzed in
contract spend
$2Bn
Saved in
SaaS spend

Streamline SaaS governance and save 10-30%

Book a Demo with Expert
CTA image