AI Agent Security Platform
Say Yes to AI Agents Without Handing Over the Keys
Know where every agent is, what it can reach, and what permissions it holds, with a kill switch for any agent that shouldn't be there.
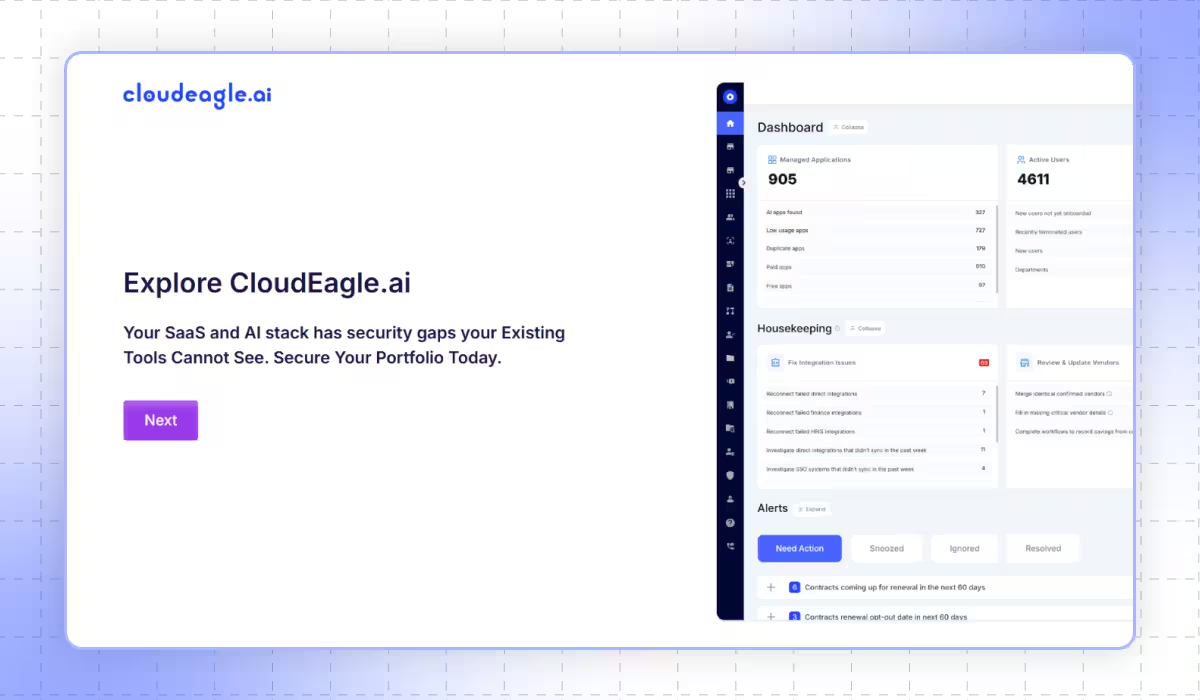




Nobody Can Say Which Agents Are Running or What They Can Reach
Without Agent Governance

Agent Governance With CloudEagle.ai

Security Leaders Who Took Control of AI and Access


Govern Every AI Agent Without Slowing Your Teams Down
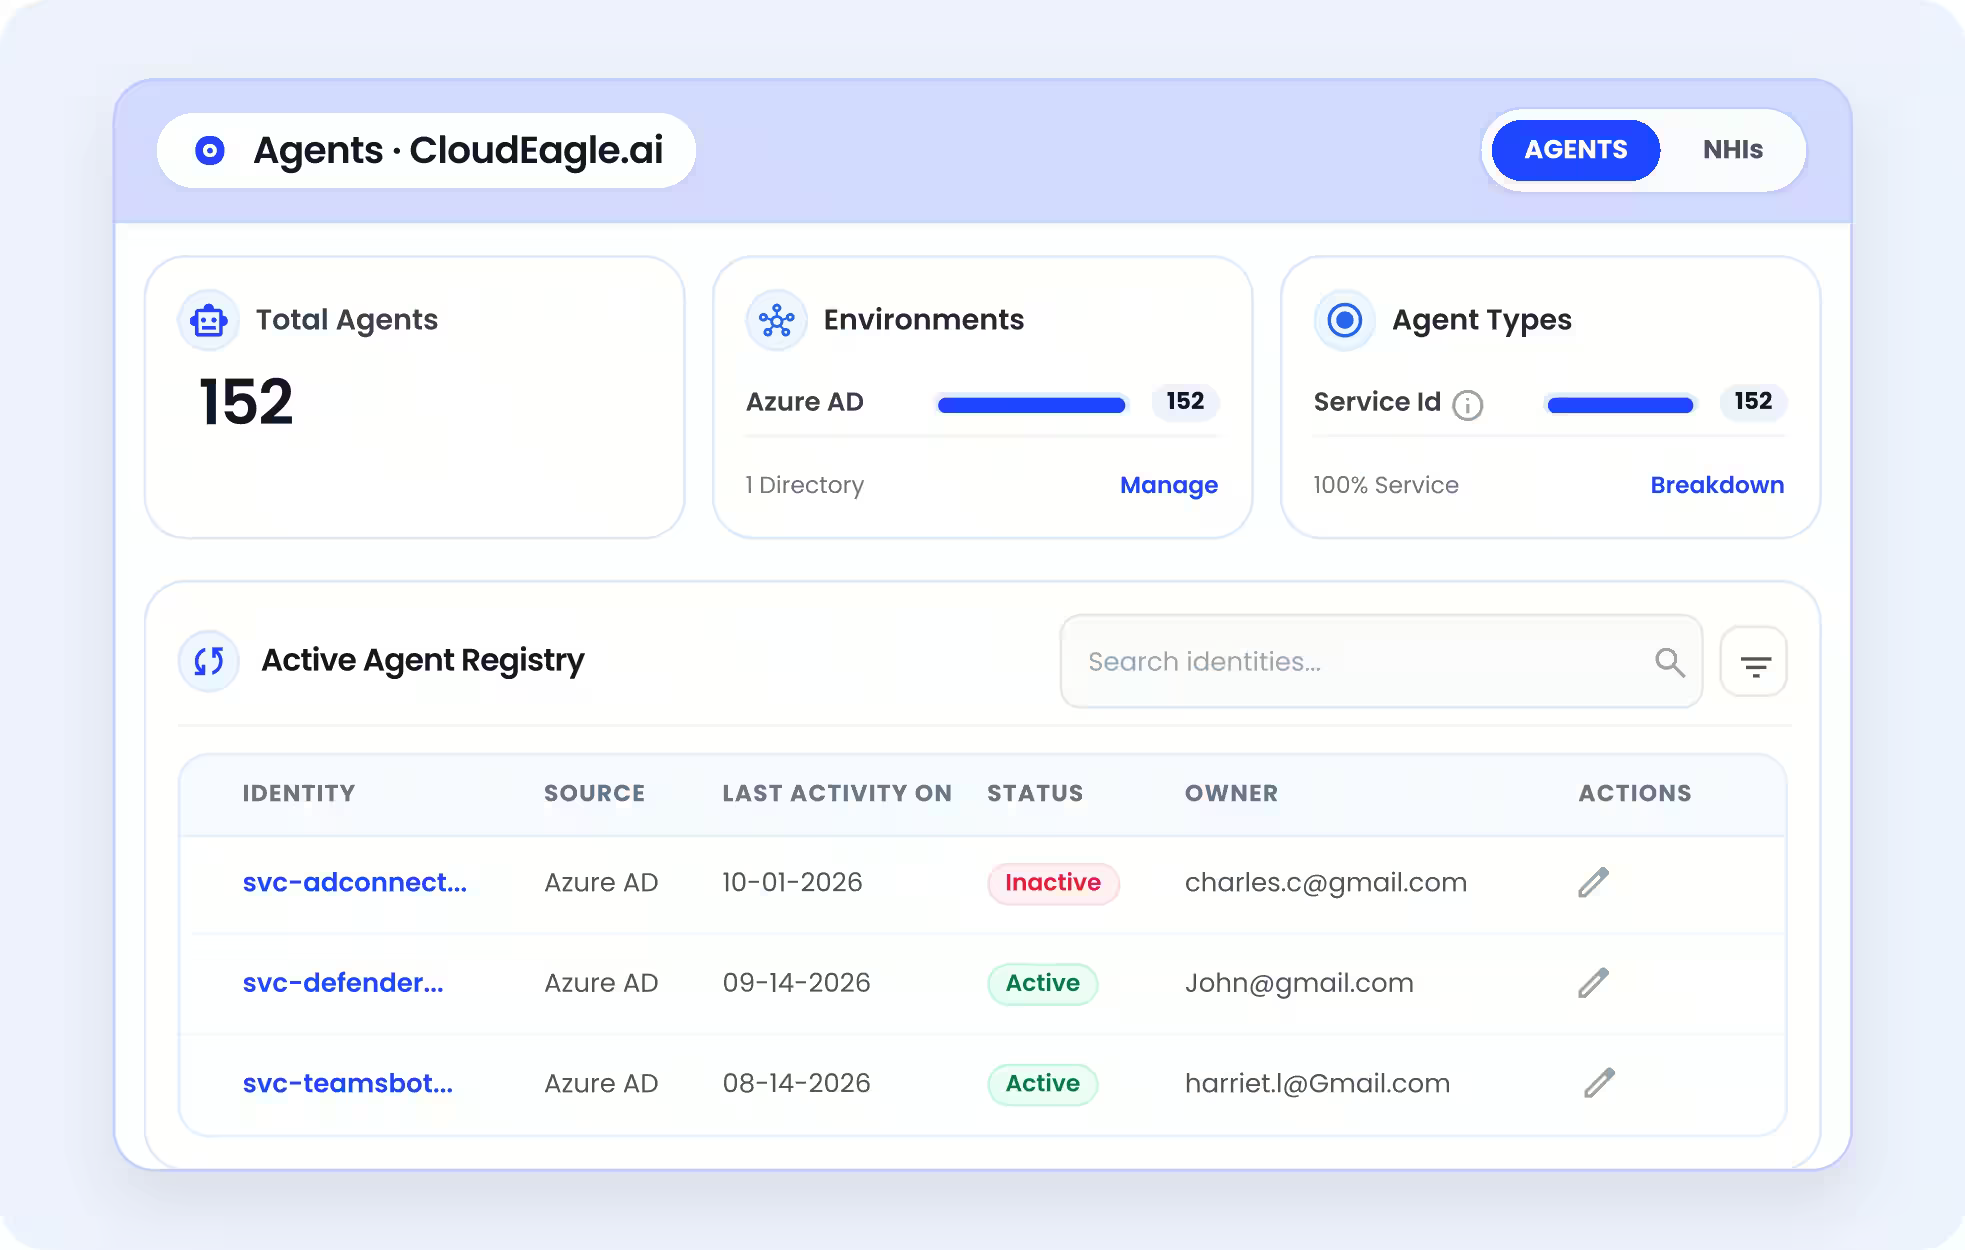
Find Every Agent Running in Your Environment
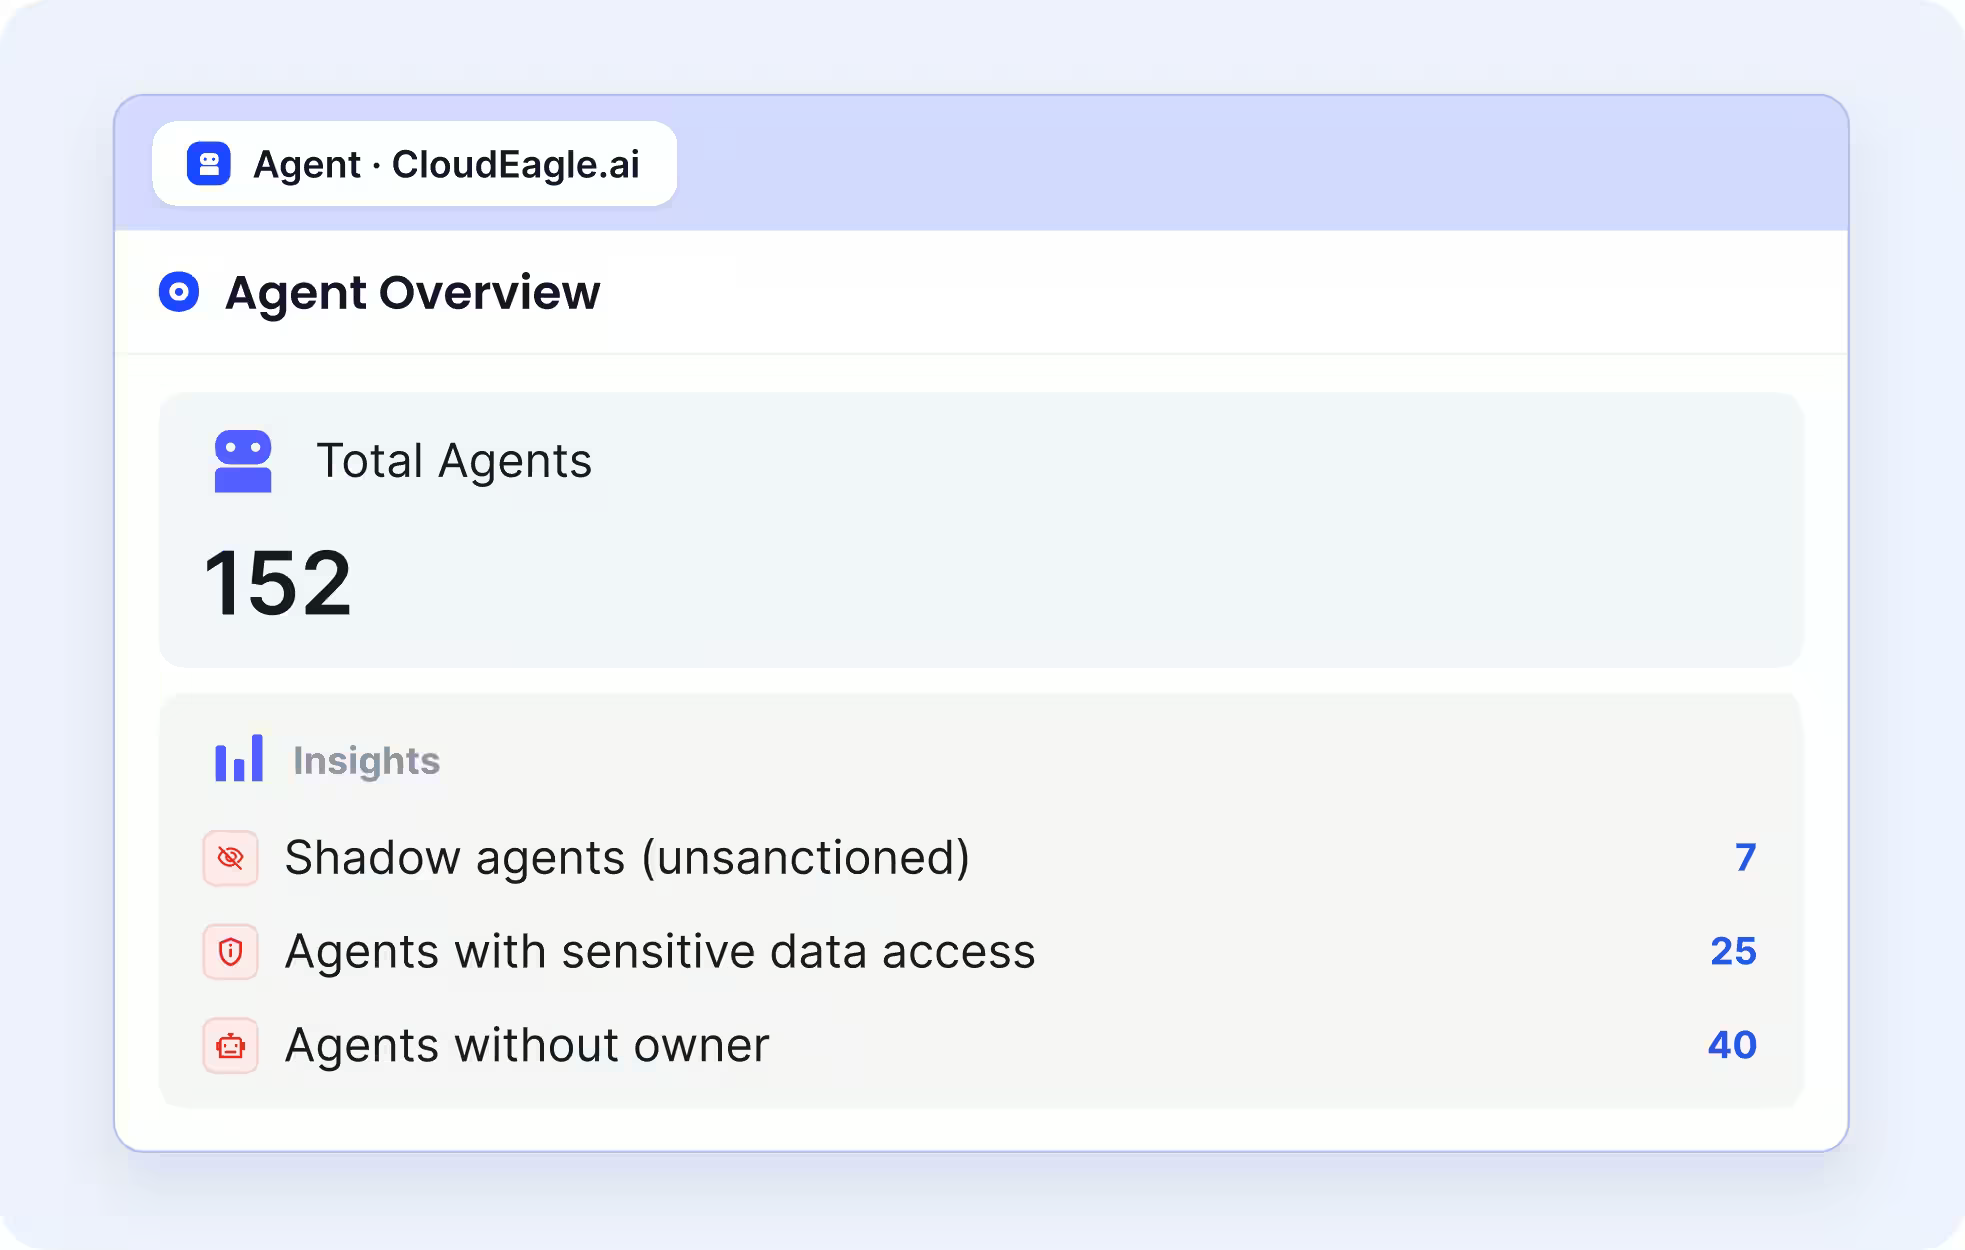
Know Exactly What Each Agent Can Access
Hold Every Agent to Least Privilege
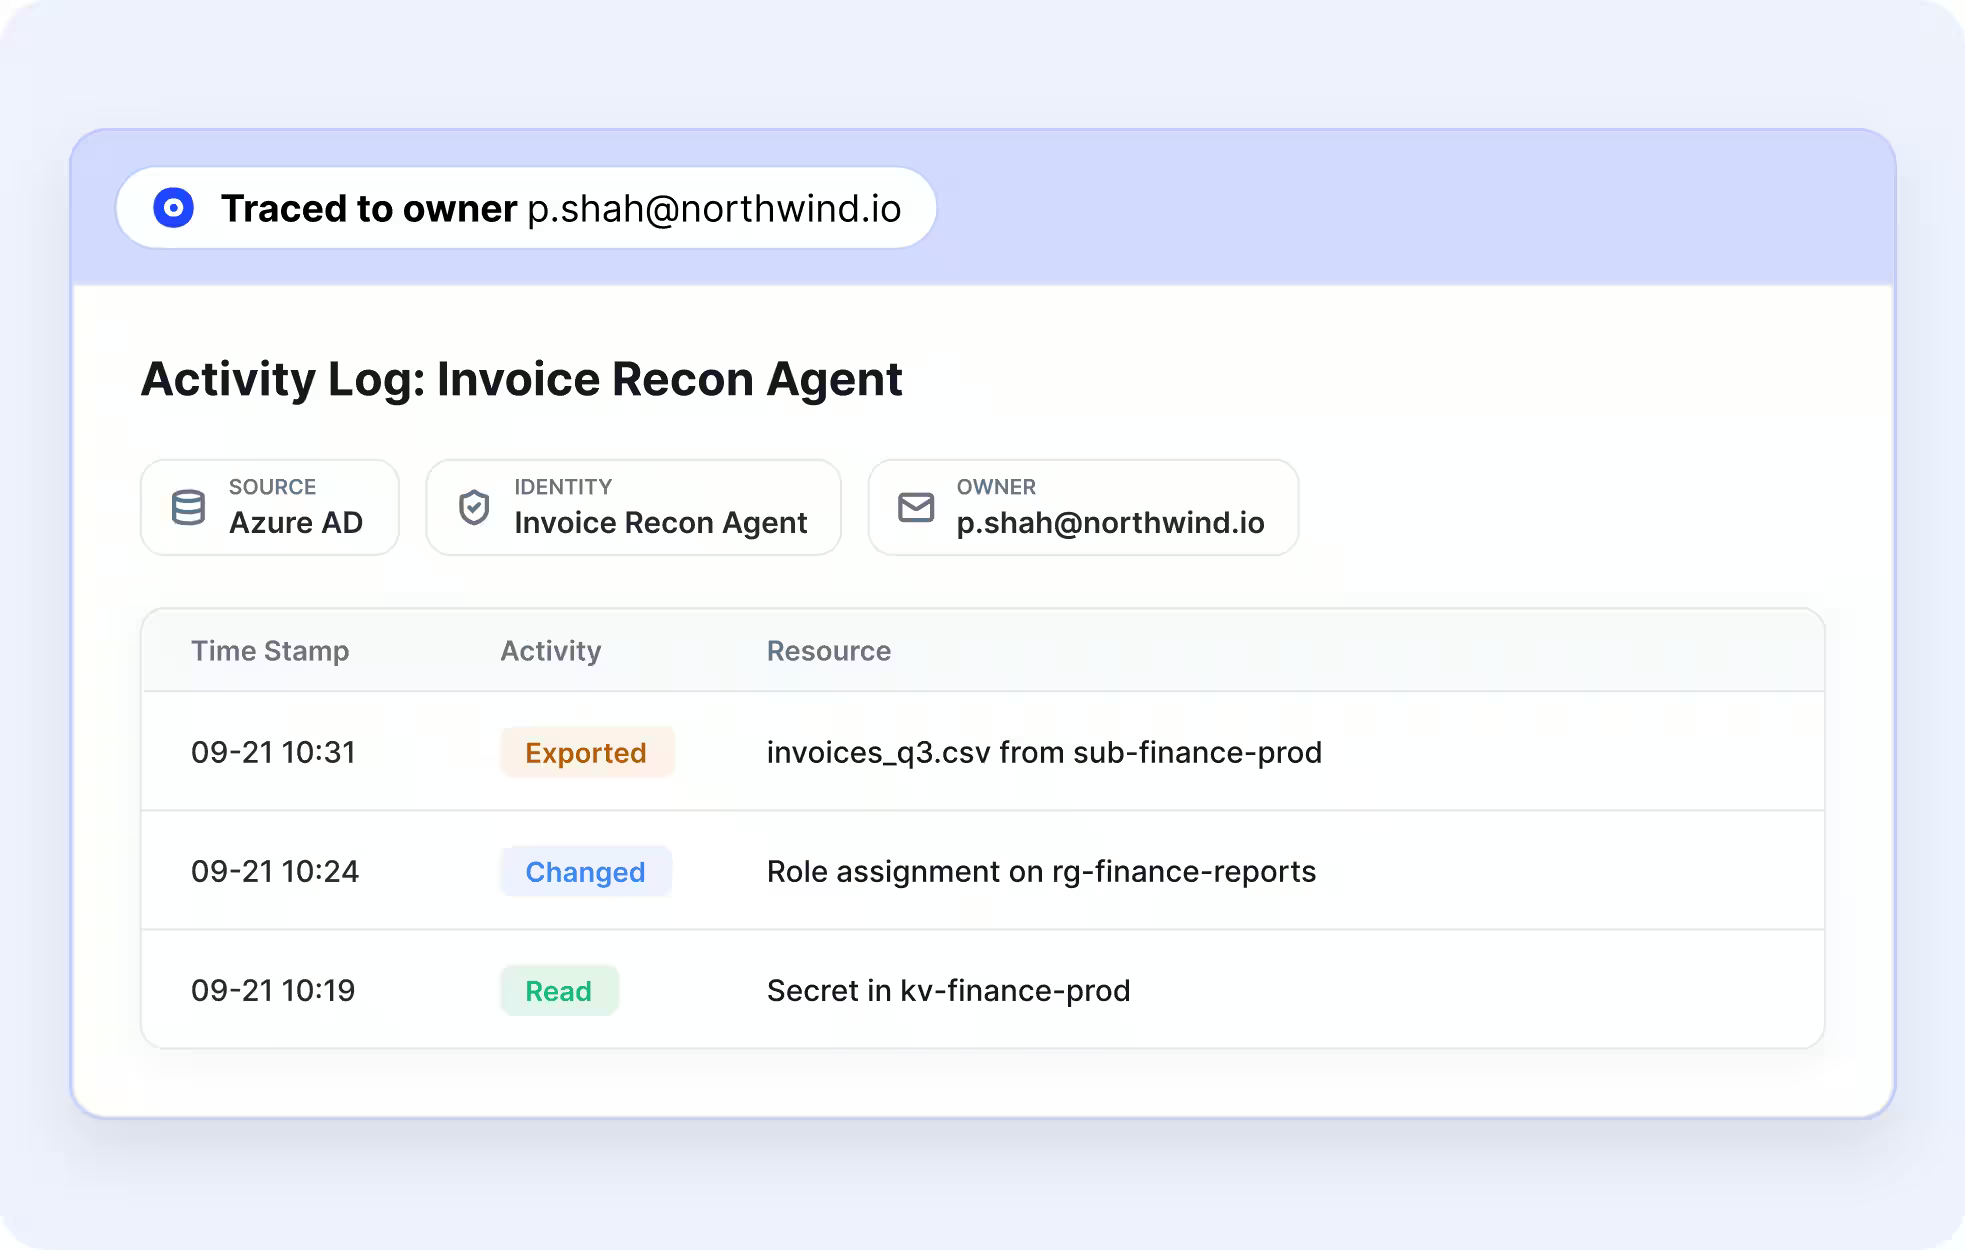
See What Your Agents Have Been Doing
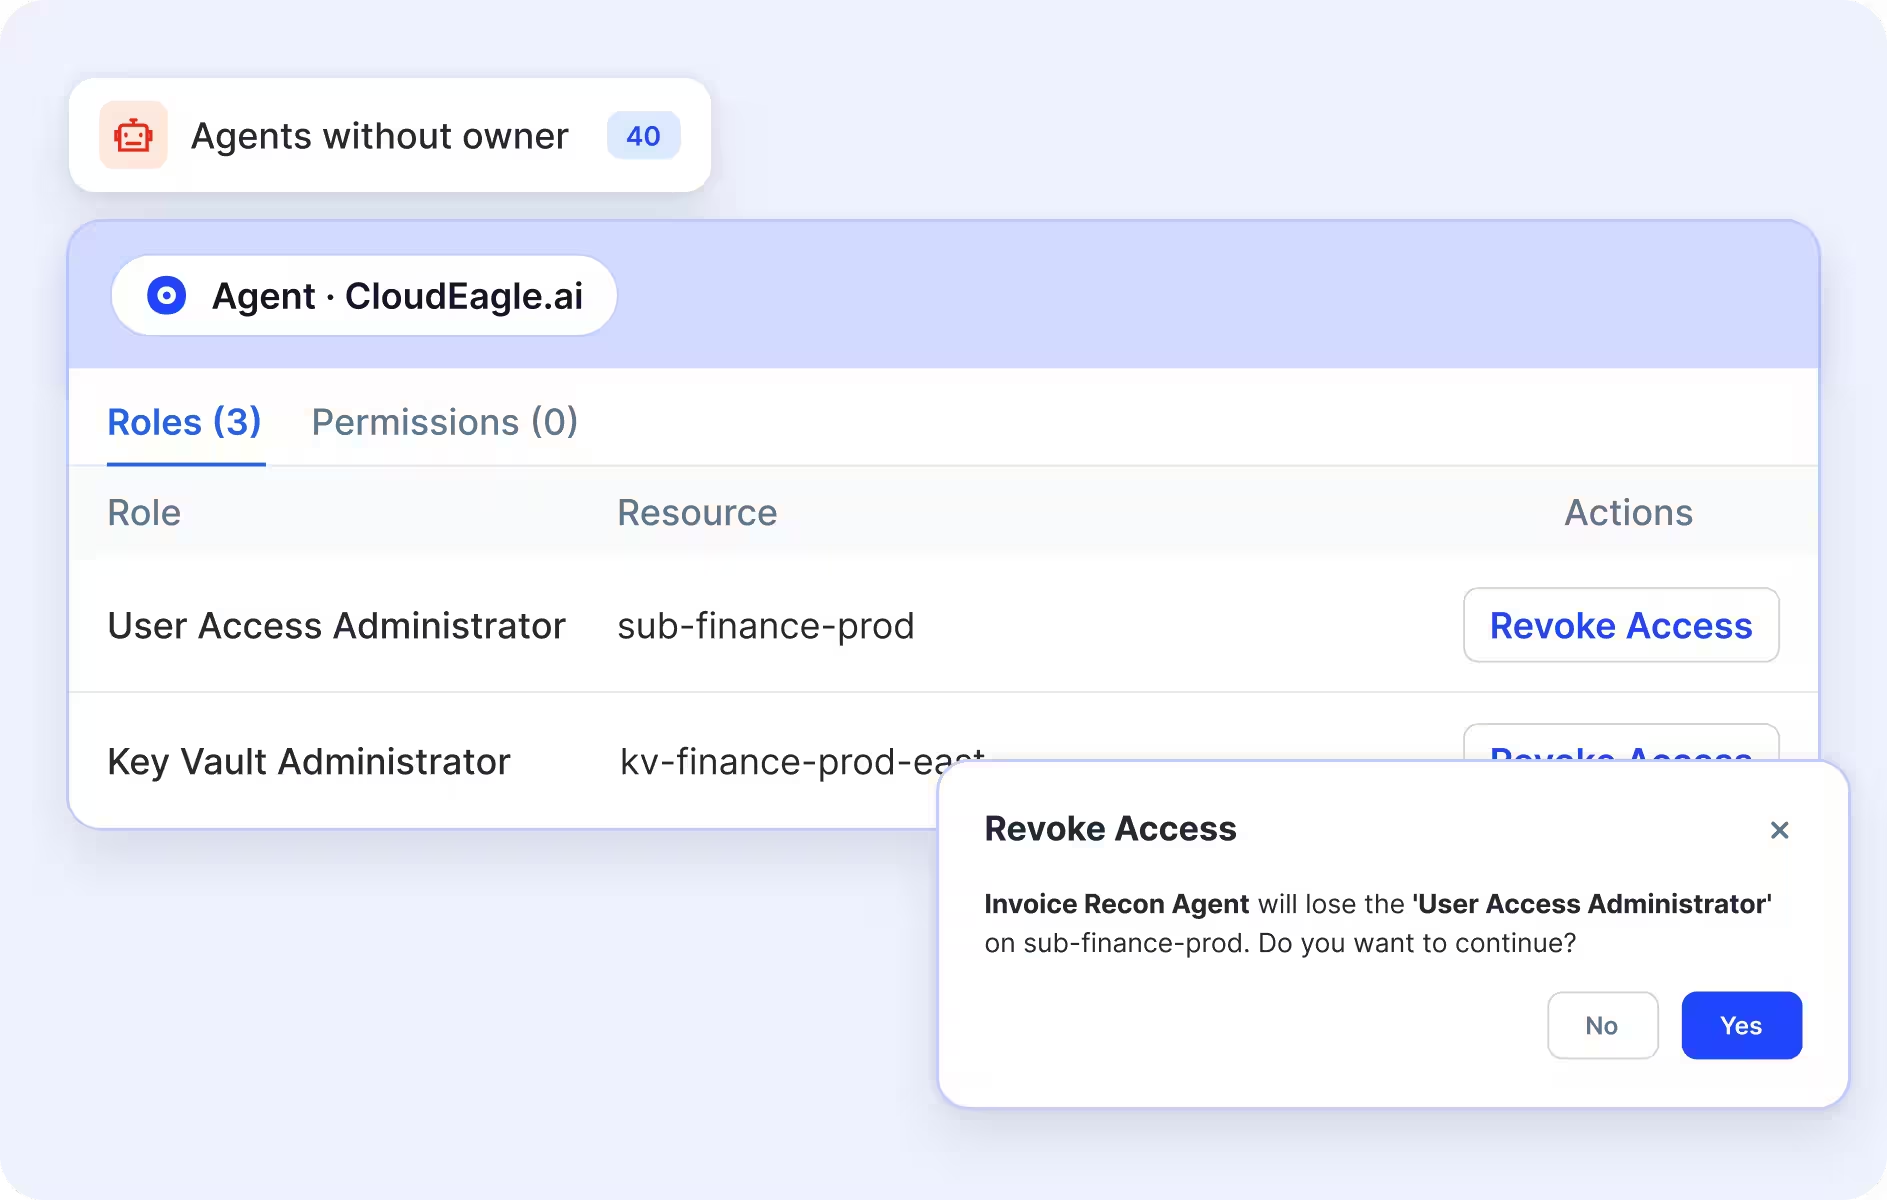
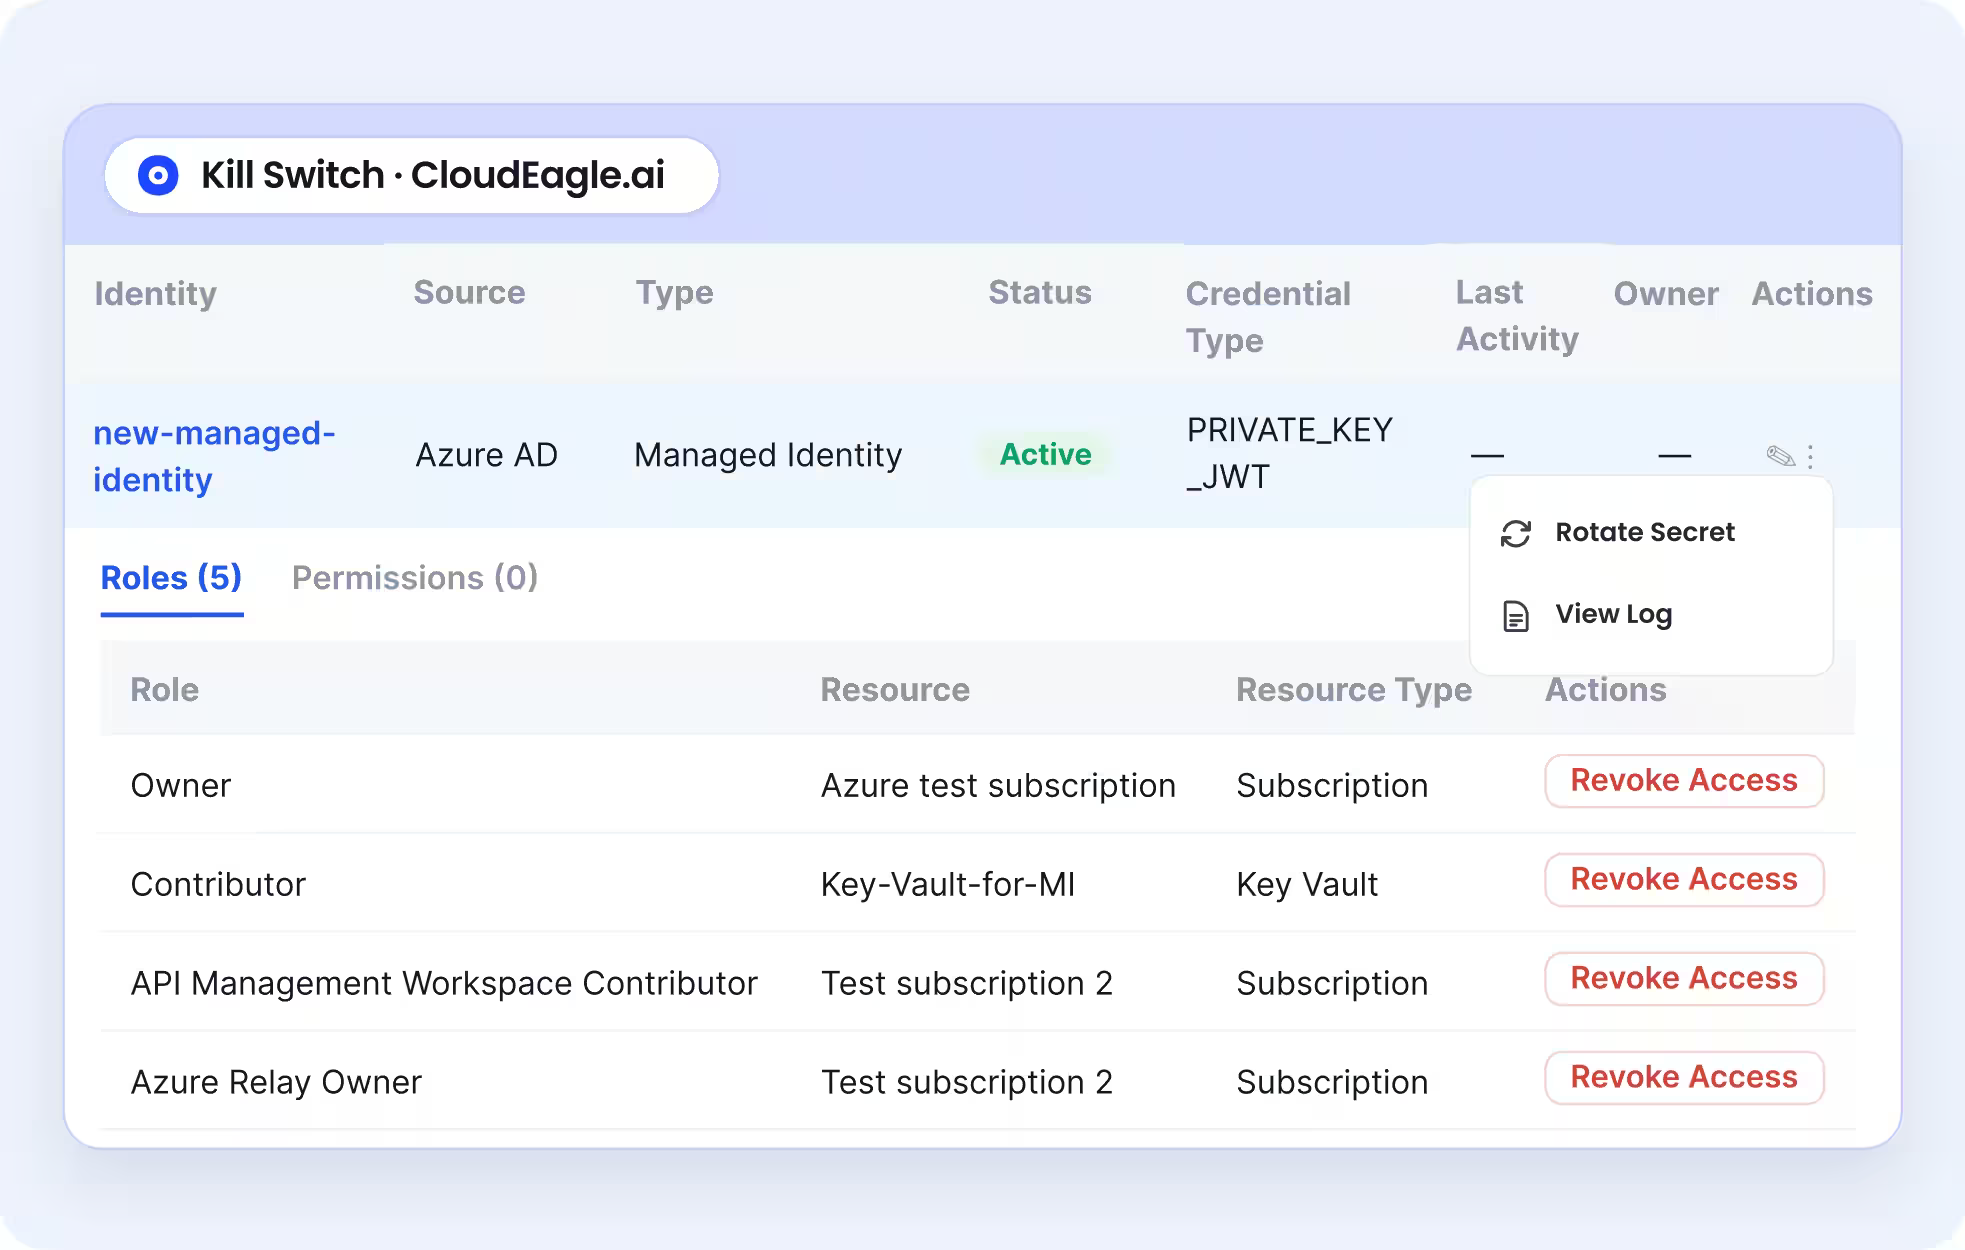
Stop a Risky Agent the Moment You Find It
How Teams Govern AI on CloudEagle.ai


Frequently Asked Questions
An AI agent security platform like CloudEagle.ai tells you where your AI agents are, what each one can access, and what permissions it holds, and gives you a kill switch to shut any agent down. CloudEagle.ai also logs what each agent did and every action your team takes.
AI agents run under machine identities. CloudEagle.ai reads those identities from your identity provider, like Microsoft Entra ID or Okta, and from your connected apps, so agents show up whether or not anyone registered them with IT.
Every agent is set up with an identity that holds roles, scopes, and app assignments. CloudEagle.ai reads those from your identity provider and app admin APIs and shows every role an agent holds, down to the resource, including access it hasn't used yet. It flags agents that are inactive, have no owner, or hold more access than their job needs.
It keeps running with the access it had. CloudEagle.ai flags agents whose owner has left, so you can assign a new owner or shut the agent down before its access to critical data becomes a way in.
It's one place to shut an agent down. In CloudEagle.ai, you can revoke any role an agent holds, down to a single resource, rotate its secret where the platform supports it, or deactivate its identity. Nothing happens automatically. Your admins decide, and CloudEagle.ai logs every action.
Yes. Pull up the activity log for any agent to see what it did, what it changed, and which resources it touched. CloudEagle.ai also logs every admin action, from revoking a role to rotating a secret.
No. CloudEagle.ai reads identity, permission, and activity data. Your agents keep running exactly as they do today until an admin decides to act.
Each platform's console shows only the agents built on that platform, and your teams build agents in more than one place. CloudEagle.ai gives you one inventory across Microsoft Entra ID, Okta, and your connected apps. For each agent, you see its owner, credentials, roles, permissions, and activity, with one way to shut it down.
Non-human identity management covers the credentials behind your integrations and automations, like service accounts, API tokens, and service principals. AI agent management focuses on the agents themselves: where they were built, what data they can reach, and who owns them. CloudEagle.ai covers both on the same identity data, so each agent stays tied to its credentials.
It's the account an agent uses to connect to apps and data, such as a service principal in Microsoft Entra ID. That identity holds the permissions that decide what the agent can reach, which is why an AI agents security platform like CloudEagle.ai governs the identity to control the agent.