HIPAA Compliance Checklist for 2025

Picture this: an employee logs in once in the morning and gains instant access to 25 business-critical SaaS apps. That's the power of Single Sign-On (SSO): fast and frictionless.
But here's the catch: if that single credential is compromised, attackers get the keys to your entire kingdom.
Credential abuse still shows up in 39% of breaches across the full attack chain, even after vulnerability exploitation overtook it as the top initial access vector, according to Verizon's 2026 DBIR. A single stolen SSO token can bypass multiple layers of security and put every connected app at risk.
Shadow IT adds to the problem. Apps connected to SSO without IT's knowledge operate outside your oversight until it's too late.
As enterprises scale their SaaS ecosystems, SSO security risks have become one of the most overlooked weaknesses in security programs. This guide breaks down the top SSO security risks and challenges, explains why they matter, and shares the best practices that protect your identity infrastructure.
1. What Is SSO Security?
SSO security is the set of strategies, protocols, and controls that protect a centralized authentication system. Instead of managing many passwords, users log in once and reach authorized applications through a trusted Identity Provider (IdP).
For IT, SSO centralizes identity management. It also creates a single point of failure: if an attacker compromises SSO, they can move laterally across your environment undetected.
Examples of SSO
- Corporate SSO through Okta, Microsoft Entra ID (formerly Azure AD), or Ping Identity.
- Google Workspace SSO for SaaS apps.
- Internal SSO portals for cloud apps and on-prem services.
2. Why Does SSO Security Matter for Modern Enterprises?
SSO delivers centralized control, better compliance, and operational efficiency. Left unsecured, it becomes the perfect breach vector.
Why SSO security matters
- Centralized Risk: One compromise exposes many systems.
- Regulatory Pressure: SOC 2, ISO 27001, and GDPR all expect strict access control.
- Hybrid Work: Remote employees reach dozens of apps daily, which widens the attack surface.
- Rising Attacks: Phishing and token theft increasingly target identity providers directly.
SSO security is no longer optional. It's foundational to enterprise cybersecurity.
3. What Are the Most Common SSO Security Risks?
Single Sign-On (SSO) simplifies authentication, but it can also create a single point of failure. If an attacker compromises an account or authentication token, they may gain access to multiple connected systems.
Weak Authentication Protocols
Outdated or password-only authentication leaves SSO open to credential stuffing and brute force attacks. Without MFA, one weak password can compromise dozens of apps.
- PCI DSS 4.0 requires MFA for all access into the cardholder data environment.
- HIPAA's current Security Rule doesn't explicitly require it, but HHS has proposed making MFA mandatory.
Overreliance on a Single Point of Failure
SSO centralizes access. If your IdP goes down, users get locked out, and if it's breached, attackers walk in.
Token Theft and Session Hijacking
Attackers steal SSO tokens through phishing, malicious browser extensions, or malware, and gain long-term access without ever needing a password. Session hijacking is notoriously hard to detect.
- In 2023, attackers pulled session tokens out of HAR files in Okta's support system and hijacked the sessions of five customers.
- A valid stolen token can let an attacker skip MFA entirely.
Poor Identity Federation Practices
Misconfigured SAML or OIDC connections let attackers impersonate users with forged authentication tokens. A SAML misconfiguration can allow unauthorized access and bypass your other controls.
- Federation issues are especially risky in multi-cloud environments, where inconsistent protocols create gaps.
Inadequate Role-Based Access Controls (RBAC)
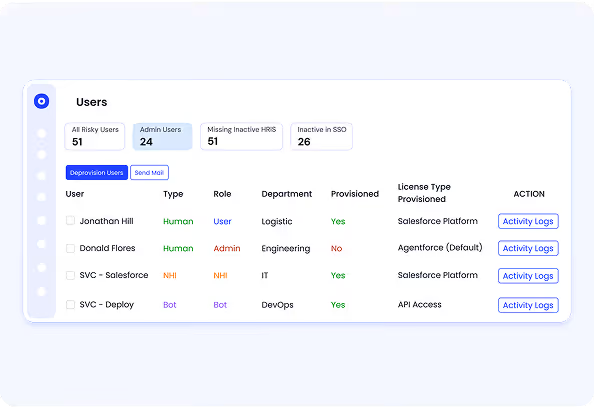
SSO doesn't enforce least privilege by default. When RBAC is too broad, users get access they don't need, which amplifies insider threat risk.
Shadow IT and Unauthorized App Access
Employees often connect unapproved SaaS apps to SSO without telling IT. Those unmanaged apps can lack MFA, monitoring, or encryption, which creates dangerous visibility gaps.
- CloudEagle.ai's own research found that 60% of SaaS and AI apps operate outside IT visibility.

4. What Challenges Make SSO Implementation Hard?
Implementing Single Sign-On (SSO) can be challenging because it involves complex authentication protocols, integration issues across different applications, and strict security requirements.
Legacy System Integration
Many legacy systems lack modern identity standards, so integrating them with SSO takes workarounds. Those workarounds, like outdated authentication protocols, can weaken the whole SSO setup.
Lack of User Training and Awareness
SSO is only as strong as the people using it. If users don't recognize phishing or still reuse passwords, even a well-built SSO deployment can be compromised.
- Make secure login practices part of your security culture.
- Run scenario-based training, not generic awareness decks.
Compatibility Across Cloud Environments
In multi-cloud environments, one provider may support SAML while another supports OIDC. Misconfigurations between protocols can cause access problems or leave gaps that expose sensitive data.
Limited Visibility Into User Behavior
Traditional SSO often lacks deep user behavior analytics. Without it, signals like impossible travel (logins from two distant locations at once) or odd login hours go unnoticed.
- Add behavioral analytics to your SSO monitoring.
- Treat anomalies as early warning of a breach.
5. What Are the Best Practices to Strengthen SSO Security?
To improve Single Sign-On (SSO) security and reduce the risk of a compromised login affecting multiple systems, follow these essential security best practices:
Enforce Multi-Factor Authentication (MFA)
MFA is a critical layer of defense for any SSO setup. Requiring a second factor, such as a code or biometric, sharply reduces the risk of account compromise.
- Prioritize high-value accounts and sensitive applications.
- Prefer phishing-resistant methods like FIDO2/WebAuthn where you can. CISA warns that push, SMS, and one-time codes can all be phished.
- If you're still on push notifications, turn on number matching as an interim step.
Regularly Audit SSO Logs and Access Patterns
Constant monitoring of SSO logs is how you spot suspicious activity.
- Look for failed logins, unusual access times, and unfamiliar devices or IP addresses.
- Audit access patterns on a schedule, not only after an incident.
- Keep the logs you need for compliance.
Configure Granular Access Policies
Conditional access policies keep sensitive apps behind the right conditions.
- Use IP restrictions, device compliance, and geolocation.
- Let only authorized users reach specific systems under predefined conditions.
Apply the Least Privilege Principle
Users should have only the access their job requires. Combine SSO with RBAC and periodic access reviews to prevent privilege creep, where people accumulate rights over time.
- Review and adjust access levels on a regular cycle.
- Remove permissions that no longer match the role.
Use Modern Identity Standards (SAML, OIDC, SCIM)
Modern standards give you stronger encryption, token management, and provisioning than older authentication methods.
- Retire outdated authentication systems.
- Use SCIM for automated provisioning and deprovisioning where apps support it.
Automate Offboarding for Departed Users
Accounts left active after an employee leaves are a serious security hole.
- Automate offboarding through SCIM or a SaaS management tool so accounts are deprovisioned promptly.
- Cover apps outside the IdP too, since those are the ones that get missed.
6. Which Tools Help Monitor and Mitigate SSO Security Risks?
Single Sign-On (SSO) security risks are managed through Identity Providers (IdPs), SIEM platforms, and specialized SaaS security tools that help detect suspicious activity, monitor authentication events, and identify access-related vulnerabilities.
Real-Time Threat Detection Platforms
Tools like Microsoft Defender for Identity and Okta ThreatInsight use AI to detect anomalies and stop suspicious logins in real time.
SaaS Management and Governance Platforms Like CloudEagle.ai
CloudEagle.ai adds governance and visibility on top of your SSO. It integrates with 500+ apps, discovers shadow IT, and automates access reviews and offboarding.
Identity and Access Governance Tools
IGA solutions like SailPoint and Saviynt add periodic reviews, separation-of-duties checks, and compliance workflows to strengthen your SSO security posture.
7. How Does CloudEagle.ai Strengthen SSO Security?
CloudEagle.ai is an AI-powered AI governance, SaaS management and SaaS security platform that gives enterprises one command center to discover, secure, govern, and manage their entire SaaS and AI stack.
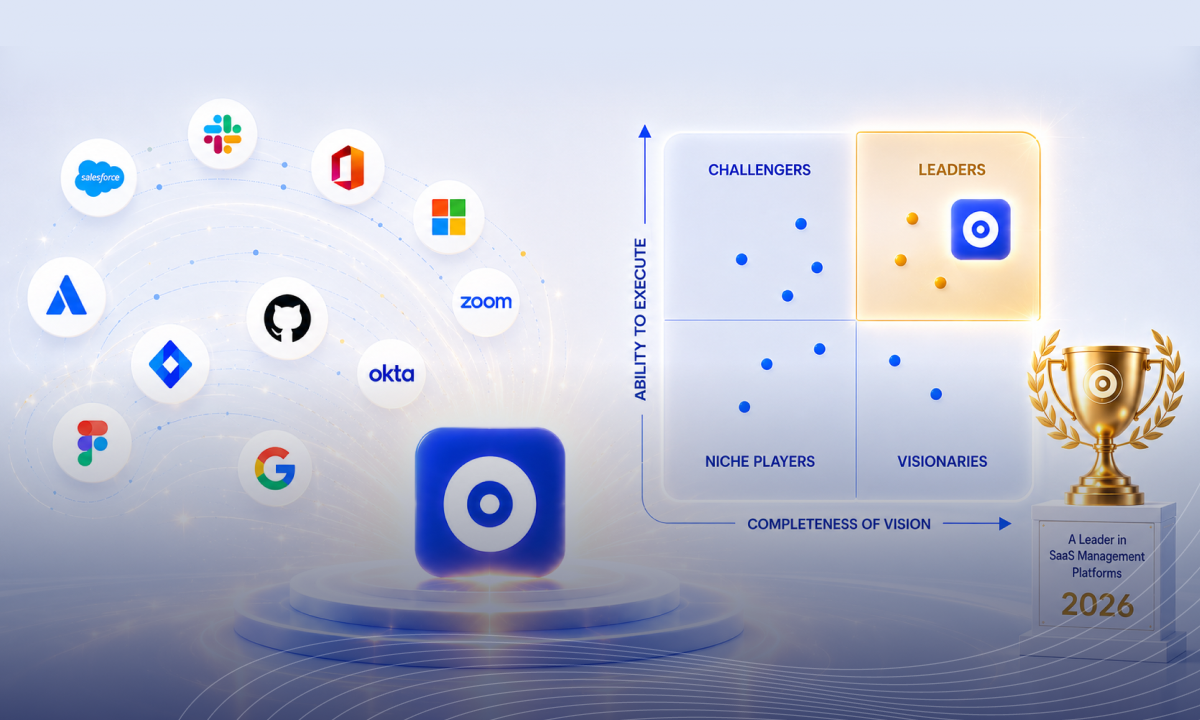
Many enterprises already run a strong IdP like Okta, Microsoft Entra ID, or Ping Identity. Your IdP handles authentication. It doesn't give your team visibility into every SaaS app, or governance over who keeps access.
We fill that gap. We don't replace your SSO or IdP stack. We add visibility and access governance on top of it, so SSO stops being a single point of risk.
Find Unauthorized and Orphaned Access
Your IT and Security teams get one view of who has access to what, across the SaaS and AI apps connected to SSO and the ones that aren't.
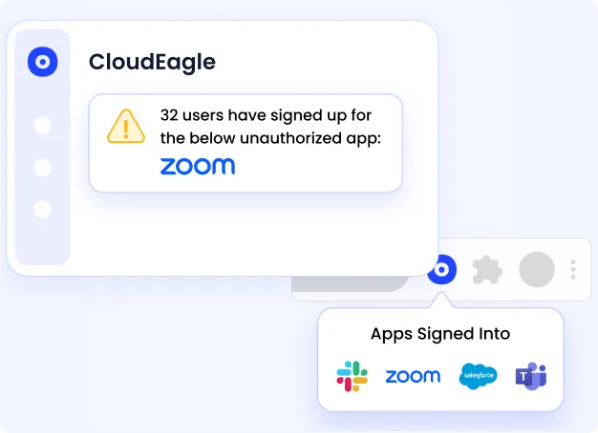
- Surface inactive, dormant, and orphaned accounts that still have access.
- Flag over-privileged and risky users so your team can fix them.
- Get alerts on risky access before it escalates into an incident.
Discover Shadow IT and Unused SaaS Accounts
Shadow IT bypasses controls like MFA and RBAC, which creates blind spots that lead to data theft and malware.
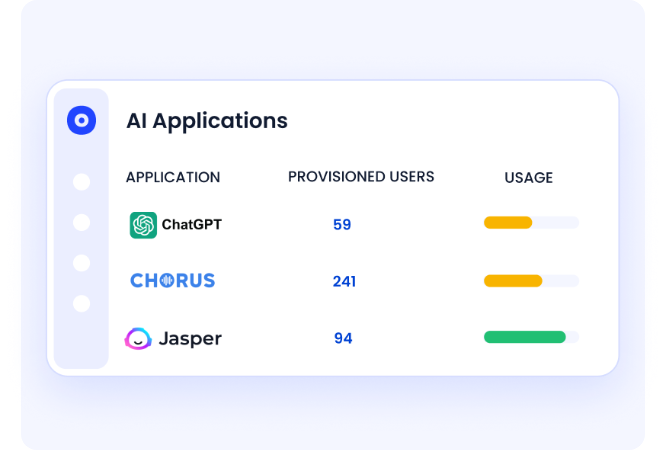
SSO logs only show the apps routed through your IdP. We detect shadow IT beyond SSO by combining signals like login activity, browser activity, and finance data, so your team can:
- Identify unmanaged apps, including shadow AI tools, that aren't part of your sanctioned stack.
- Detect dormant or unused licenses, which cuts waste and shrinks the attack surface.
- Map shadow IT back to departments or users for clean remediation.
Automate Access Reviews and Policy Enforcement
Periodic access reviews are central to SOC 2, ISO 27001, and GDPR. Manual reviews are slow, error-prone, and often skipped.
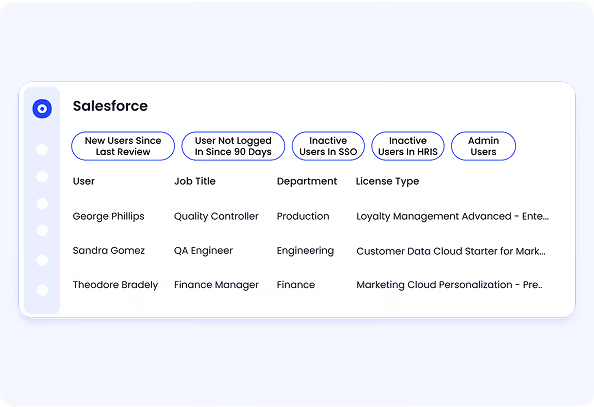
Our automated user access reviews let your team:
- Schedule audit-ready reviews for critical apps.
- Enforce least privilege across roles and departments.
- Notify app owners and managers to approve or revoke access.
- Generate centralized reports for auditors.
"We lacked confidence in our access certifications. Reviews were happening, but we couldn't clearly answer who had access, why it existed, or whether it was still valid. CloudEagle brought structure and accountability to user access reviews without reviewer fatigue."
~ Michal Lipinski, Director of IT & Security, ICEYE
ICEYE cut manual review work by 90% and saved more than 1,500 hours a year. Read the case study.
Automate Offboarding Across Your Whole Stack
Deactivating a user in the IdP doesn't remove their access to apps outside it. Our own research found that 48% of former employees still have access to company applications months after leaving.
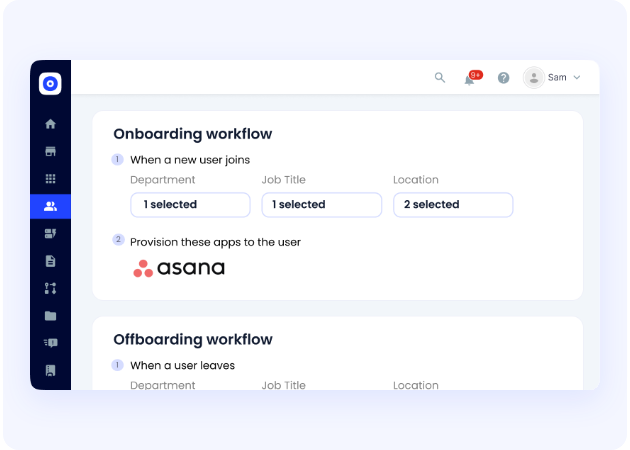
We automate onboarding and offboarding across SCIM and non-SCIM apps, and support just-in-time access so temporary access expires on its own.
Work With Your IdP and SSO Stack
Whether you use Okta, Microsoft Entra ID, Ping Identity, or another IdP, there's no rip and replace. Our 500+ direct SaaS integrations extend your IdP's reach to apps it doesn't manage.
- Apply consistent access governance across all connected SaaS apps, not just IdP-managed ones.
- Automate deprovisioning across complex environments.
- Get one place for SSO visibility, identity governance, and SaaS usage insight.
Your IdP Authenticates. Who Governs Everything Beyond It?


8. How Do You Secure SSO Without Creating a Single Point of Failure?
SSO isn't inherently risky. Poorly secured SSO is.
Implemented with phishing-resistant MFA, modern identity standards, and a governance layer, SSO improves both security and efficiency. Overlooked, it becomes a single point of catastrophic failure.
Your IdP authenticates. Your IT and Security teams still need to govern what authenticated users can reach, find the apps SSO never saw, and revoke access everywhere when people leave. That's the layer we add with CloudEagle.ai.
Ready to secure your SSO stack? Book a demo with CloudEagle.ai and see how your IT and Security teams can protect access at scale.
Frequently Asked Questions
- What Does SSO Mean in Security?
SSO lets users access multiple applications with one set of credentials through a trusted identity provider. - What Are the Biggest SSO Security Risks?
The biggest SSO security risks are weak authentication, token theft and session hijacking, misconfigured federation, overbroad RBAC, and shadow IT apps connected without IT's knowledge. - What Are the Disadvantages of SSO?
A single compromised SSO account can give attackers wide access, and IdP downtime can lock users out of every connected app at once. - What Are the Security Risks of Concurrent Logins?
Concurrent sessions make token theft easier to exploit and suspicious activity harder to spot. - What Is an SSO-Protected Resource?
An SSO-protected resource requires centralized authentication through the identity provider before it grants access. - What Is the Difference Between SSO and TLS?
SSO handles authentication. TLS (the successor to SSL) encrypts the connection between the user and the server.
Your IdP Authenticates. Who Governs Everything Beyond It?