Identity & Access Management

Top 7 Endpoint Security Risks You Must be Aware of in 2026

Share via:
Written by:
CloudEagle.ai Team
Reviewed by
Nidhi Jain
Last Updated:
May 19, 2025
blog-cms-banner-bg
Little-Known Negotiation Hacks to Get the Best Deal on Slack
cta-bg-blogDownload Your Copy

HIPAA Compliance Checklist for 2025

Download PDF

Your laptop isn't the only endpoint attackers can target. Phones, tablets, remote devices, IoT systems, and employee workstations can all become entry points into an enterprise network.

Endpoint Security Risks are vulnerabilities and threats targeting connected devices that can expose systems, credentials, applications, or sensitive data. 

These endpoint security threats go beyond malware and include phishing, unpatched software, stolen credentials, shadow IT, and insider activity.

The challenge is simple: every connected device expands the attack surface. Endpoint Security Risks can turn a single compromised device into a path toward sensitive systems and data. Here are seven risks security teams need to identify and control in 2026

‍

TL;DR

  • Sophisticated phishing emails mimic trusted sources to steal credentials and sidestep endpoint defenses, no malware needed.
  • Attackers actively scan for outdated systems. One missed update or legacy tool can open your network to exploitation.
  • One careless click and ransomware spreads across drives, cloud apps, and shared folders—endpoint security is often the weakest link.
  • Personal laptops and unsecured Wi-Fi give attackers new paths into your environment—especially without strict access policies or mobile device management.
  • CloudEagle.ai offers unified visibility, automates access control, enforces just-in-time permissions, and secures SaaS usage, strengthening endpoint security across the board.

‍

1. What Makes Endpoint Security So Critical in 2025?

The way you work has changed and attackers know it. Endpoints aren’t just devices anymore; they’re the frontline of your entire digital operation. From remote employees to contractors on personal laptops, the number of unsecured access points has exploded. And with it, so has the risk.

endpoint security risks have evolved from basic malware to sophisticated attacks like fileless intrusions, phishing payloads, and lateral movement techniques. Remote devices are attractive because they often sit outside the traditional network perimeter, making them easier to compromise and harder to monitor. 

Look at what happened to Colonial Pipeline in 2021. The breach started with a single compromised VPN account, tied to a remote endpoint without multi-factor authentication. That one device opened the door to a ransomware attack that disrupted fuel supplies across the Eastern U.S. Fast-forward to 2025. 

With hybrid work becoming the norm, you're juggling personal devices, cloud apps, unsecured Wi-Fi, and blurred network boundaries. Unless you lock down your endpoints, you're giving attackers exactly what they want: easy access, low resistance, and high reward.

‍

2. Top 7 Endpoint Security Risks That Expand Attack Surface 

The top endpoint security risks that expand an organization's attack surface include malware, phishing, unpatched software, poor access controls, insider threats, and compromised devices. 

Each endpoint creates a potential path into corporate systems, making endpoint visibility, protection, and continuous monitoring essential.

A. Phishing-Based Credential Theft

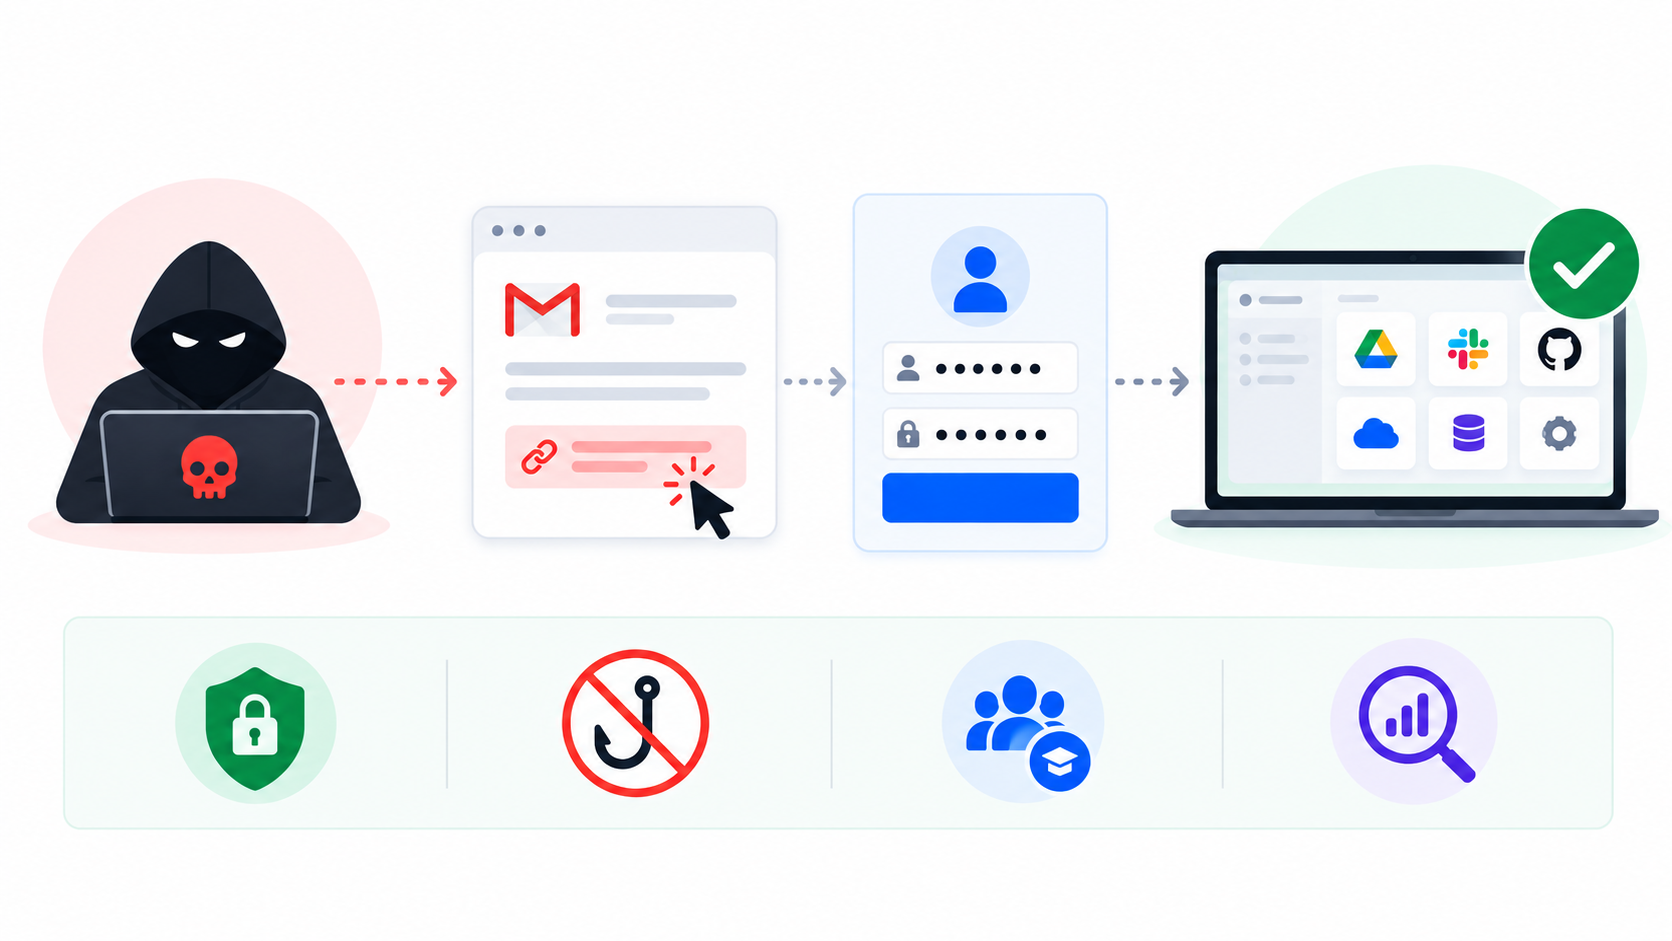
Phishing-based data breach occurs when attackers trick employees into revealing passwords, authentication codes, or other login credentials.
 

‍

Attackers may use fake password resets, vendor invoices, emails, or messaging platforms to make requests appear legitimate.

Once stolen credentials are used, attackers can access corporate systems as legitimate users and bypass many endpoint defenses. MFA, phishing-resistant authentication, security awareness training, and login monitoring can reduce this risk.

B. Unpatched Vulnerabilities

You probably know you should keep systems updated, but even with automated patching tools, gaps still happen. Another example of endpoint security issues.

Unpatched vulnerabilities occur when endpoints run outdated operating systems, applications, or software with known security flaws. 

Attackers can exploit these weaknesses to gain unauthorized access, execute malicious code, or compromise sensitive data.

Legacy systems and devices that no longer receive security updates create additional exposure. Organizations should maintain accurate endpoint inventories, prioritize critical patches, and isolate systems that cannot be updated.

C. Ransomware Targeting Endpoints

Endpoint ransomware infects devices and encrypts or steals data, potentially allowing attackers to spread across connected systems. 

Common entry points include malicious email attachments, compromised websites, exploited vulnerabilities, and exposed remote services.

A compromised endpoint can expose local files, credentials, network shares, and connected cloud resources. Endpoint detection and response (EDR), application controls, backups, and network segmentation can limit ransomware impact.

D. Insecure BYOD and Remote Devices

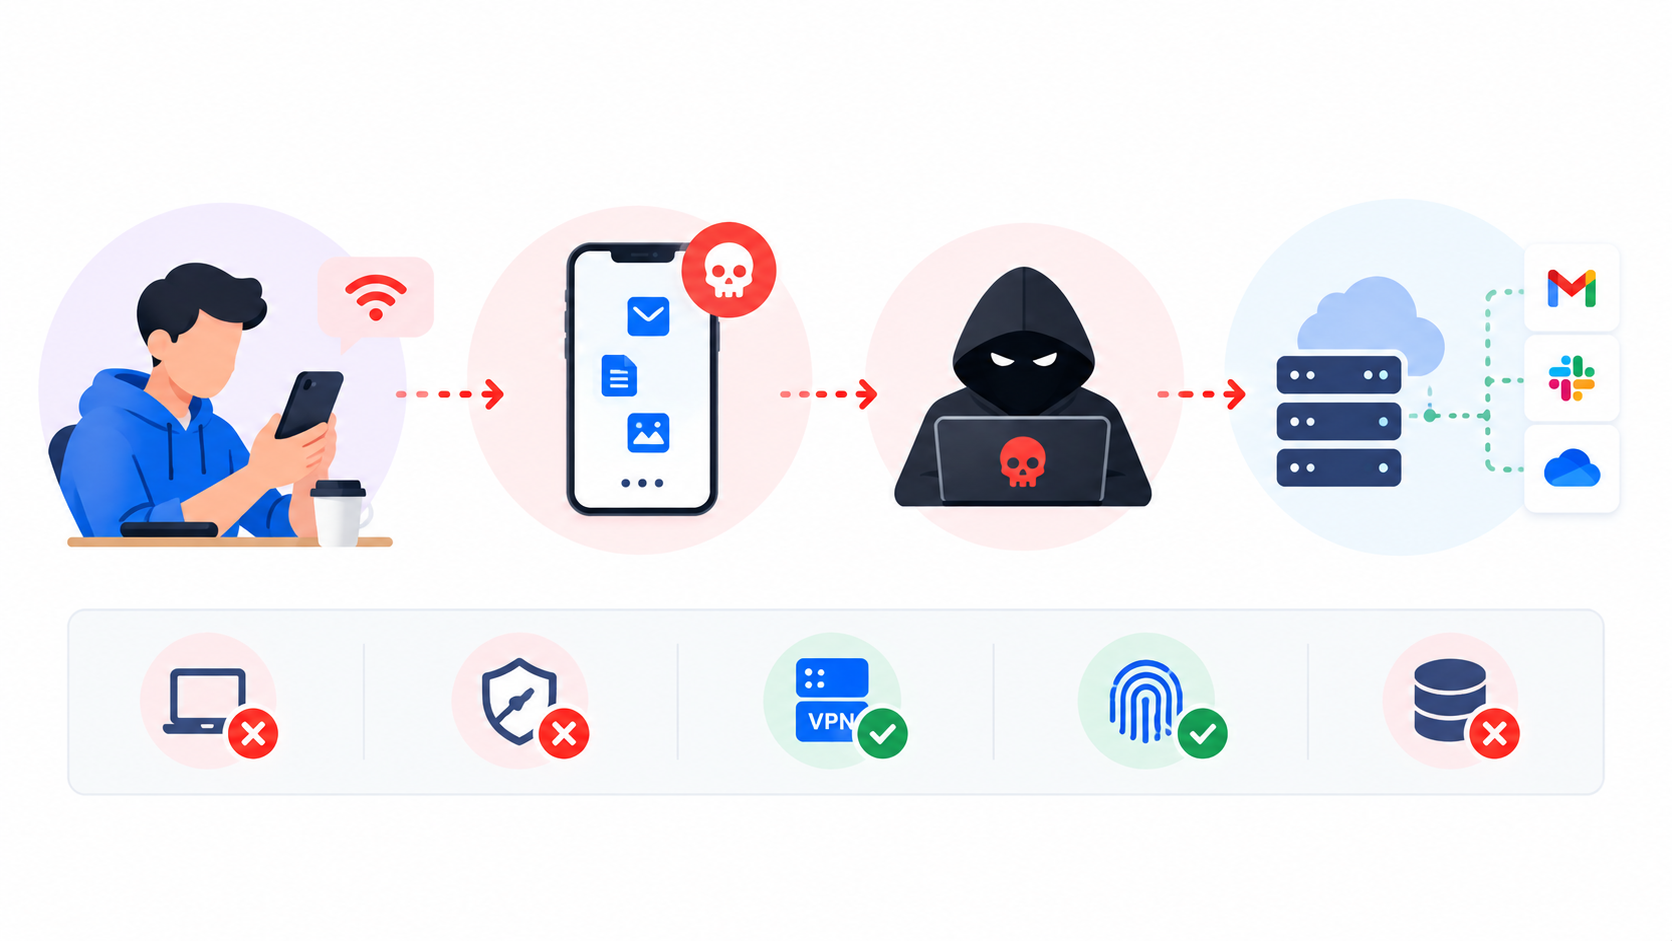
BYOD (Bring Your Own Device) policies make life easier for employees, especially in remote and hybrid environments. 

But without strict access controls, these same devices can quietly bypass your perimeter defenses. An employee logging in from an unsecured phone over public Wi-Fi can easily become the entry point for malware or data exfiltration.
‍

‍

One of the biggest oversights? Lack of mobile device management (MDM) or endpoint detection on personal devices. 

IT teams often assume VPNs or multi-factor authentication are enough, but those tools don’t protect the data stored locally or stop a compromised device from syncing with corporate systems.

E. Insider Threats (Intentional and Accidental)

Insider threats occur when employees, contractors, or other authorized users intentionally or accidentally expose systems or sensitive data. 

Examples include sending confidential files to personal accounts, uploading data to unauthorized applications, or misusing privileged access.

Endpoint monitoring, least-privilege access, data loss prevention, and user activity monitoring can help detect and limit insider threats. 

Security teams should also distinguish between malicious activity and accidental mistakes when investigating incidents.

F. Lack of Endpoint Encryption

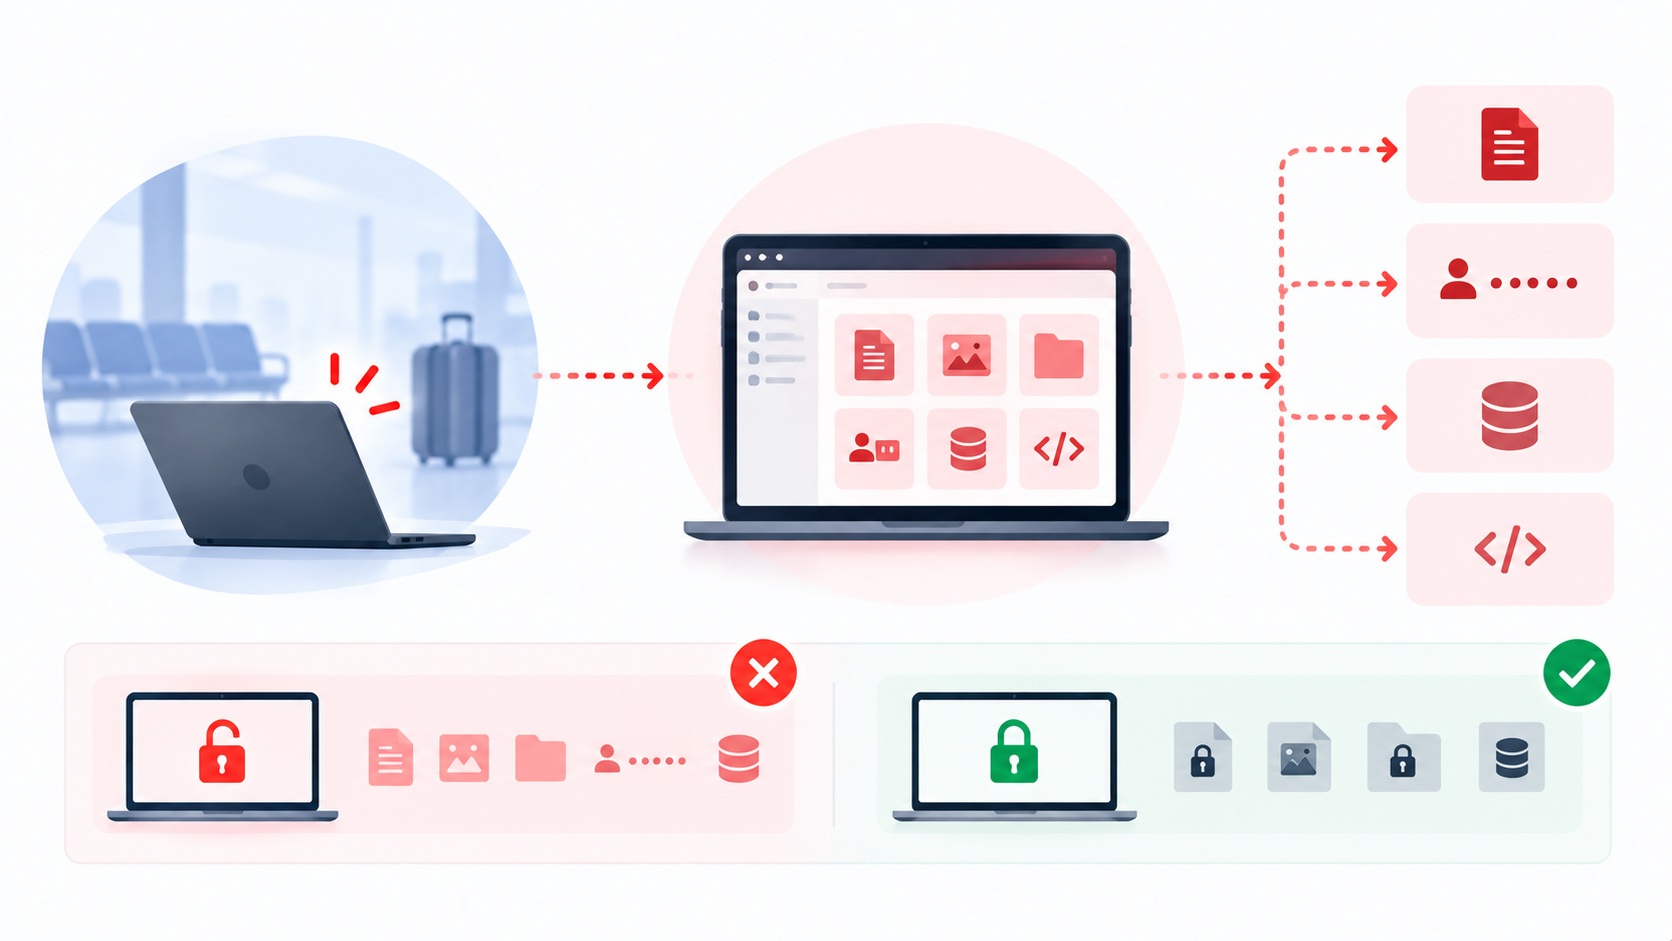
A lost or stolen laptop shouldn’t make headline news, but it still does because full-disk encryption isn’t consistently enforced. Many companies assume that strong passwords or biometric locks are enough. But once a device is in the wrong hands, without encryption, everything on it is fair game.
‍

‍

Unencrypted endpoint security risks often contain sensitive files, cached credentials, or access to internal systems. If attackers get physical access to that device, they don’t need to “hack” anything. They can simply extract the data offline.

Security expert Bruce Schneier once said, 

“If you think technology can solve your security problems, then you don’t understand the problems and you don’t understand the technology.”

Without encryption, you're leaving your data defenseless the moment a device slips out of your control.

G. Poor Endpoint Visibility and Monitoring

Poor endpoint visibility makes it difficult for security teams to identify unmanaged devices, suspicious activity, outdated software, or unauthorized applications. 

This creates blind spots across remote, hybrid, and distributed environments.

Effective monitoring requires a current endpoint inventory, centralized security telemetry, and continuous detection of unusual activity. 

Security teams should be able to identify which devices are connected, who uses them, what software they run, and whether they show signs of compromise

‍

3. What are the Different Types of Endpoint Security Risks?

Endpoint security risks can be grouped into several categories based on how attackers gain access, exploit devices, or misuse legitimate access. The main types include:

  • Malware Risks: Viruses, ransomware, spyware, and other malicious software can compromise endpoint devices.
  • Credential-Based Risks: Phishing, credential theft, and password endpoint attacks can give attackers access through legitimate accounts.
  • Vulnerability Risks: Unpatched operating systems, applications, and known software vulnerabilities can provide exploitable entry points.
  • Access and Configuration Risks: Weak permissions, insecure settings, and excessive privileges can expose sensitive systems and data.
  • Shadow IT Risks: Unauthorized applications, personal devices, and unmanaged endpoints can bypass established security controls.
  • Insider Risks: Employees or contractors can accidentally or intentionally misuse legitimate access.
  • Device and Network Risks: Lost devices, unsecured remote endpoints, and compromised network connections can expose corporate resources.

Together, these endpoint security risks can expand an organization's attack surface and create pathways to sensitive systems, credentials, and data.

‍

4. How to Mitigate Endpoint Security Risks?

Organizations can mitigate endpoint security risks by securing devices, controlling access, patching vulnerabilities, monitoring activity, and responding quickly to threats. 

A layered approach reduces the chance that a compromised endpoint becomes an entry point into corporate systems.

  • Maintain Endpoint Visibility: Discover and inventory laptops, smartphones, servers, IoT devices, and other connected endpoints.
  • Patch Vulnerabilities: Keep operating systems, applications, and security tools updated to close known vulnerabilities.
  • Enforce Access Controls: Apply least-privilege access, MFA, and device-based access policies to limit unauthorized access.
  • Deploy Endpoint Protection: Use EDR or endpoint security software to detect malware, suspicious behavior, and active threats.
  • Control Shadow IT: Identify and manage unauthorized applications, personal devices, and unmanaged endpoints.
  • Monitor Endpoint Activity: Continuously track unusual logins, processes, downloads, and other suspicious behavior.
  • Prepare for Incidents: Define response procedures to isolate compromised devices, investigate activity, and restore secure operations.

Effective endpoint security combines prevention, continuous monitoring, access control, and rapid response rather than relying on a single security tool.

‍4. Conclusion

From phishing attacks and ransomware to insider threats and unpatched software, you can’t overlook the endpoint security risks of an unmanaged endpoint. 

If you're serious about protecting your data, start by locking down every device that touches your network. Enforce zero-trust access, automate patches, encrypt everything, and monitor continuously.

And if you need help safeguarding your company’s security aspects, you can consider CloudEagle.ai. The platform will make sure you take necessary steps to protect app access. So, contact CloudEagle.ai and let the experts help you understand how the platform works. 

‍

6.Frequently Asked Questions

1. What are the three main types of endpoint security?

The main types are antivirus/anti-malware protection, endpoint detection and response (EDR), and data loss prevention (DLP). Together, they help block threats, detect malicious activity, and protect sensitive data.

2. What is an endpoint threat?

An endpoint threat is any cyber risk targeting user devices such as laptops, phones, or tablets. These threats often involve malware, phishing, or unauthorized access that exploit device vulnerabilities.

3. What is an endpoint in risk assessment?

An endpoint is any device connected to a network that can serve as a potential entry point for attackers. In risk assessments, endpoints are evaluated for vulnerabilities and exposure to cyber threats.

4. What is AAA in cyber security?

AAA stands for Authentication, Authorization, and Accounting. It defines how users are verified, what resources they can access, and how their actions are logged for auditing.

5. What is endpoint DLP?

Endpoint Data Loss Prevention (DLP) safeguards data stored or used on devices. It helps prevent leaks by monitoring activity and enforcing rules around data transfers, sharing, or storage.

‍

Advertisement for a SaaS Subscription Tracking Template with a call-to-action button to download and a partial graphic of a tablet showing charts.Banner promoting a SaaS Agreement Checklist to streamline SaaS management and avoid budget waste with a call-to-action button labeled Download checklist.Blue banner with text 'The Ultimate Employee Offboarding Checklist!' and a black button labeled 'Download checklist' alongside partial views of checklist documents from cloudeagle.ai.Digital ad for download checklist titled 'The Ultimate Checklist for IT Leaders to Optimize SaaS Operations' by cloudeagle.ai, showing checklist pages.Slack Buyer's Guide offer with text 'Unlock insider insights to get the best deal on Slack!' and a button labeled 'Get Your Copy', accompanied by a preview of the guide featuring Slack's logo.Monday Pricing Guide by cloudeagle.ai offering exclusive pricing secrets to maximize investment with a call-to-action button labeled Get Your Copy and an image of the guide's cover.Blue banner for Canva Pricing Guide by cloudeagle.ai offering a guide to Canva costs, features, and alternatives with a call-to-action button saying Get Your Copy.Blue banner with white text reading 'Little-Known Negotiation Hacks to Get the Best Deal on Slack' and a white button labeled 'Get Your Copy'.Blue banner with text 'Little-Known Negotiation Hacks to Get the Best Deal on Monday.com' and a white button labeled 'Get Your Copy'.Blue banner with text 'Little-Known Negotiation Hacks to Get the Best Deal on Canva' and a white button labeled 'Get Your Copy'.Banner with text 'Slack Buyer's Guide' and a 'Download Now' button next to images of a guide titled 'Slack Buyer’s Guide: Features, Pricing & Best Practices'.Digital cover of Monday Pricing Guide with a button labeled Get Your Copy on a blue background.Canva Pricing Guide cover with a button labeled Get Your Copy on a blue gradient background.

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.
License Count
Benchmark
Per User/Per Year

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.
License Count
Benchmark
Per User/Per Year

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.
Notion Plus
License Count
Benchmark
Per User/Per Year
100-500
$67.20 - $78.72
500-1000
$59.52 - $72.00
1000+
$51.84 - $57.60
Canva Pro
License Count
Benchmark
Per User/Per Year
100-500
$74.33-$88.71
500-1000
$64.74-$80.32
1000+
$55.14-$62.34

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.
Zoom Business
License Count
Benchmark
Per User/Per Year
100-500
$216.00 - $264.00
500-1000
$180.00 - $216.00
1000+
$156.00 - $180.00

Enter your email to
unlock the report

Oops! Something went wrong while submitting the form.

Get the Right Security Platform To Secure Your Cloud Infrastructure

Please enter a business email
Thank you!
The 2023 SaaS report has been sent to your email. Check your promotional or spam folder.
Oops! Something went wrong while submitting the form.

Access full report

Please enter a business email
Thank you!
The 2023 SaaS report has been sent to your email. Check your promotional or spam folder.
Oops! Something went wrong while submitting the form.
  • Sophisticated phishing emails mimic trusted sources to steal credentials and sidestep endpoint defenses, no malware needed.
  • Attackers actively scan for outdated systems. One missed update or legacy tool can open your network to exploitation.
  • One careless click and ransomware spreads across drives, cloud apps, and shared folders, endpoint security is often the weakest link.
  • Personal laptops and unsecured Wi-Fi give attackers new paths into your environment, especially without strict access policies or mobile device management.
  • CloudEagle.ai offers unified visibility, automates access control, enforces just-in-time permissions, and secures SaaS usage, strengthening endpoint security across the board.

‍

Your laptop isn't the only endpoint attackers can target. Phones, tablets, remote devices, IoT systems, and employee workstations can all become entry points into an enterprise network.

Endpoint Security Risks are vulnerabilities and threats targeting connected devices that can expose systems, credentials, applications, or sensitive data. 

These endpoint security threats go beyond malware and include phishing, unpatched software, stolen credentials, shadow IT, and insider activity.

The challenge is simple: every connected device expands the attack surface. Endpoint Security Risks can turn a single compromised device into a path toward sensitive systems and data. Here are seven risks security teams need to identify and control in 2026

‍

TL;DR

  • Sophisticated phishing emails mimic trusted sources to steal credentials and sidestep endpoint defenses, no malware needed.
  • Attackers actively scan for outdated systems. One missed update or legacy tool can open your network to exploitation.
  • One careless click and ransomware spreads across drives, cloud apps, and shared folders—endpoint security is often the weakest link.
  • Personal laptops and unsecured Wi-Fi give attackers new paths into your environment—especially without strict access policies or mobile device management.
  • CloudEagle.ai offers unified visibility, automates access control, enforces just-in-time permissions, and secures SaaS usage, strengthening endpoint security across the board.

‍

1. What Makes Endpoint Security So Critical in 2025?

The way you work has changed and attackers know it. Endpoints aren’t just devices anymore; they’re the frontline of your entire digital operation. From remote employees to contractors on personal laptops, the number of unsecured access points has exploded. And with it, so has the risk.

endpoint security risks have evolved from basic malware to sophisticated attacks like fileless intrusions, phishing payloads, and lateral movement techniques. Remote devices are attractive because they often sit outside the traditional network perimeter, making them easier to compromise and harder to monitor. 

Look at what happened to Colonial Pipeline in 2021. The breach started with a single compromised VPN account, tied to a remote endpoint without multi-factor authentication. That one device opened the door to a ransomware attack that disrupted fuel supplies across the Eastern U.S. Fast-forward to 2025. 

With hybrid work becoming the norm, you're juggling personal devices, cloud apps, unsecured Wi-Fi, and blurred network boundaries. Unless you lock down your endpoints, you're giving attackers exactly what they want: easy access, low resistance, and high reward.

‍

2. Top 7 Endpoint Security Risks That Expand Attack Surface 

The top endpoint security risks that expand an organization's attack surface include malware, phishing, unpatched software, poor access controls, insider threats, and compromised devices. 

Each endpoint creates a potential path into corporate systems, making endpoint visibility, protection, and continuous monitoring essential.

A. Phishing-Based Credential Theft

Phishing-based data breach occurs when attackers trick employees into revealing passwords, authentication codes, or other login credentials.


‍

Attackers may use fake password resets, vendor invoices, emails, or messaging platforms to make requests appear legitimate.

Once stolen credentials are used, attackers can access corporate systems as legitimate users and bypass many endpoint defenses. MFA, phishing-resistant authentication, security awareness training, and login monitoring can reduce this risk.

B. Unpatched Vulnerabilities

You probably know you should keep systems updated, but even with automated patching tools, gaps still happen. Another example of endpoint security issues.

Unpatched vulnerabilities occur when endpoints run outdated operating systems, applications, or software with known security flaws. 

Attackers can exploit these weaknesses to gain unauthorized access, execute malicious code, or compromise sensitive data.

Legacy systems and devices that no longer receive security updates create additional exposure. Organizations should maintain accurate endpoint inventories, prioritize critical patches, and isolate systems that cannot be updated.

C. Ransomware Targeting Endpoints

Endpoint ransomware infects devices and encrypts or steals data, potentially allowing attackers to spread across connected systems. 

Common entry points include malicious email attachments, compromised websites, exploited vulnerabilities, and exposed remote services.

A compromised endpoint can expose local files, credentials, network shares, and connected cloud resources. Endpoint detection and response (EDR), application controls, backups, and network segmentation can limit ransomware impact.

D. Insecure BYOD and Remote Devices

BYOD (Bring Your Own Device) policies make life easier for employees, especially in remote and hybrid environments. 

But without strict access controls, these same devices can quietly bypass your perimeter defenses. An employee logging in from an unsecured phone over public Wi-Fi can easily become the entry point for malware or data exfiltration.

‍

‍

One of the biggest oversights? Lack of mobile device management (MDM) or endpoint detection on personal devices. 

IT teams often assume VPNs or multi-factor authentication are enough, but those tools don’t protect the data stored locally or stop a compromised device from syncing with corporate systems.

E. Insider Threats (Intentional and Accidental)

Insider threats occur when employees, contractors, or other authorized users intentionally or accidentally expose systems or sensitive data. 

Examples include sending confidential files to personal accounts, uploading data to unauthorized applications, or misusing privileged access.

Endpoint monitoring, least-privilege access, data loss prevention, and user activity monitoring can help detect and limit insider threats. 

Security teams should also distinguish between malicious activity and accidental mistakes when investigating incidents.

F. Lack of Endpoint Encryption

A lost or stolen laptop shouldn’t make headline news, but it still does because full-disk encryption isn’t consistently enforced. Many companies assume that strong passwords or biometric locks are enough. But once a device is in the wrong hands, without encryption, everything on it is fair game.

‍

‍

Unencrypted endpoint security risks often contain sensitive files, cached credentials, or access to internal systems. If attackers get physical access to that device, they don’t need to “hack” anything. They can simply extract the data offline.

Security expert Bruce Schneier once said, 

“If you think technology can solve your security problems, then you don’t understand the problems and you don’t understand the technology.”

Without encryption, you're leaving your data defenseless the moment a device slips out of your control.

G. Poor Endpoint Visibility and Monitoring

Poor endpoint visibility makes it difficult for security teams to identify unmanaged devices, suspicious activity, outdated software, or unauthorized applications. 

This creates blind spots across remote, hybrid, and distributed environments.

Effective monitoring requires a current endpoint inventory, centralized security telemetry, and continuous detection of unusual activity. 

Security teams should be able to identify which devices are connected, who uses them, what software they run, and whether they show signs of compromise

‍

3. What are the Different Types of Endpoint Security Risks?

Endpoint security risks can be grouped into several categories based on how attackers gain access, exploit devices, or misuse legitimate access. The main types include:

  • Malware Risks: Viruses, ransomware, spyware, and other malicious software can compromise endpoint devices.
  • Credential-Based Risks: Phishing, credential theft, and password endpoint attacks can give attackers access through legitimate accounts.
  • Vulnerability Risks: Unpatched operating systems, applications, and known software vulnerabilities can provide exploitable entry points.
  • Access and Configuration Risks: Weak permissions, insecure settings, and excessive privileges can expose sensitive systems and data.
  • Shadow IT Risks: Unauthorized applications, personal devices, and unmanaged endpoints can bypass established security controls.
  • Insider Risks: Employees or contractors can accidentally or intentionally misuse legitimate access.
  • Device and Network Risks: Lost devices, unsecured remote endpoints, and compromised network connections can expose corporate resources.

Together, these endpoint security risks can expand an organization's attack surface and create pathways to sensitive systems, credentials, and data.

‍

4. How to Mitigate Endpoint Security Risks?

Organizations can mitigate endpoint security risks by securing devices, controlling access, patching vulnerabilities, monitoring activity, and responding quickly to threats. 

A layered approach reduces the chance that a compromised endpoint becomes an entry point into corporate systems.

  • Maintain Endpoint Visibility: Discover and inventory laptops, smartphones, servers, IoT devices, and other connected endpoints.
  • Patch Vulnerabilities: Keep operating systems, applications, and security tools updated to close known vulnerabilities.
  • Enforce Access Controls: Apply least-privilege access, MFA, and device-based access policies to limit unauthorized access.
  • Deploy Endpoint Protection: Use EDR or endpoint security software to detect malware, suspicious behavior, and active threats.
  • Control Shadow IT: Identify and manage unauthorized applications, personal devices, and unmanaged endpoints.
  • Monitor Endpoint Activity: Continuously track unusual logins, processes, downloads, and other suspicious behavior.
  • Prepare for Incidents: Define response procedures to isolate compromised devices, investigate activity, and restore secure operations.

Effective endpoint security combines prevention, continuous monitoring, access control, and rapid response rather than relying on a single security tool.

‍4. Conclusion

From phishing attacks and ransomware to insider threats and unpatched software, you can’t overlook the endpoint security risks of an unmanaged endpoint. 

If you're serious about protecting your data, start by locking down every device that touches your network. Enforce zero-trust access, automate patches, encrypt everything, and monitor continuously.

And if you need help safeguarding your company’s security aspects, you can consider CloudEagle.ai. The platform will make sure you take necessary steps to protect app access. So, contact CloudEagle.ai and let the experts help you understand how the platform works. 

‍

6.Frequently Asked Questions

1. What are the three main types of endpoint security?

The main types are antivirus/anti-malware protection, endpoint detection and response (EDR), and data loss prevention (DLP). Together, they help block threats, detect malicious activity, and protect sensitive data.

2. What is an endpoint threat?

An endpoint threat is any cyber risk targeting user devices such as laptops, phones, or tablets. These threats often involve malware, phishing, or unauthorized access that exploit device vulnerabilities.

3. What is an endpoint in risk assessment?

An endpoint is any device connected to a network that can serve as a potential entry point for attackers. In risk assessments, endpoints are evaluated for vulnerabilities and exposure to cyber threats.

4. What is AAA in cyber security?

AAA stands for Authentication, Authorization, and Accounting. It defines how users are verified, what resources they can access, and how their actions are logged for auditing.

5. What is endpoint DLP?

Endpoint Data Loss Prevention (DLP) safeguards data stored or used on devices. It helps prevent leaks by monitoring activity and enforcing rules around data transfers, sharing, or storage.

‍

CloudEagle.ai recognized in the 2025 Gartner® Magic Quadrant™ for SaaS Management Platforms
Download now
gartner chart
5x
Faster employee
onboarding
80%
Reduction in time for
user access reviews
30k
Workflows
automated
$15Bn
Analyzed in
contract spend
$2Bn
Saved in
SaaS spend

Streamline SaaS governance and save 10-30%

Book a Demo with Expert
CTA image