HIPAA Compliance Checklist for 2025

Can you truly deliver quality care without securing the devices that power your healthcare system?
A record 772 large healthcare data breaches were reported to HHS in 2025, and hacking and other IT incidents drove more than 80% of them (HIPAA Journal). Many start with a single unsecured endpoint: a clinician's tablet, a nurse's workstation, or a connected medical device.
Healthcare is no longer bound to four walls. Clinicians reach patient records from home, on mobile devices, and through third-party platforms.
That access improves care, and it opens real risk. This guide covers endpoint management for healthcare: what it is, why it matters, how to overcome the common challenges, and the strategies that balance security with usability.
1. What Is Endpoint Management for Healthcare?
Endpoint management for healthcare is the centralized monitoring, control, and protection of every device that connects to your hospital or healthcare network.
That includes desktops at nurses' stations, phones used by doctors, tablets in telehealth, and IoT-enabled medical devices like insulin pumps and portable ECG monitors. Each one is an endpoint, and each one is a potential entry point for threats.
Your team manages endpoints with software that deploys updates, controls access, enforces policy, and watches device activity in real time. Those tools make sure only authorized users and devices reach sensitive systems like your electronic health record (EHR).
Picture a hospital where hundreds of devices connect every day. Without endpoint management, nobody knows which ones are vulnerable, outdated, or compromised, and one outdated operating system can let ransomware into the whole network.
Managing endpoints well keeps your digital defenses strong so clinicians can do their jobs.
2. Why Does Healthcare Endpoint Management Need to Balance Security and Accessibility?
The question facing healthcare IT is simple: can you protect sensitive data without slowing down care?
Imagine a nurse updating patient vitals on a tablet during rounds. The device logs out every 60 seconds and demands multiple authentication steps. Now multiply that frustration across every care provider in the hospital.
The cost of getting it wrong is steep. IBM's 2026 Cost of a Data Breach report puts the average healthcare breach at $6.64 million, the highest of any industry again, even after a drop from $7.42 million in 2025 (IBM).
It is also a patient safety issue when systems are compromised or unavailable in an emergency. That is why endpoint management is a patient care enabler, not just IT hygiene.
Effective endpoint management ensures:
- Security measures don't interrupt clinical workflows.
- Access is granted by user role, device type, and context.
- Smartphones, tablets, and laptops are consistently monitored and updated.
Done well, it works quietly in the background. Clinicians get what they need, and endpoints stay closed to ransomware and unauthorized access.
3. What Are the Key Challenges in Healthcare Endpoint Management?
Handling endpoints in healthcare is complicated. You protect sensitive information, life-critical processes, and a wide mix of users and devices at the same time.
Device Diversity and Volume
Healthcare runs a multi-device environment: Windows desktops at nursing stations, iPads in exam rooms, Android tablets for home care, and legacy medical equipment with outdated firmware.
- These devices run different operating systems with different security capabilities.
- Without centralized visibility, securing each one is a constant struggle.
- An unpatched vulnerability on one system can become the entry point for a larger breach.
Compliance With Healthcare Regulations
Your team has to meet HIPAA, HITECH, and often local or international privacy laws. Those require:
- Secure access controls.
- Continuous auditing and activity logging.
- Regular patch management.
- Incident response planning.
One unauthorized access or outdated endpoint can mean fines, lost patient trust, and reputational damage.
The bar is also moving. HHS has proposed a HIPAA Security Rule update that would make MFA and encryption mandatory and require an annual technology asset inventory. Final action has slipped to July 2027, and the current Security Rule stays fully enforceable in the meantime.
Shadow IT and Personal Device Usage
In fast-paced clinical settings, staff use their own phones and tablets to check schedules, open the EHR, and message peers.
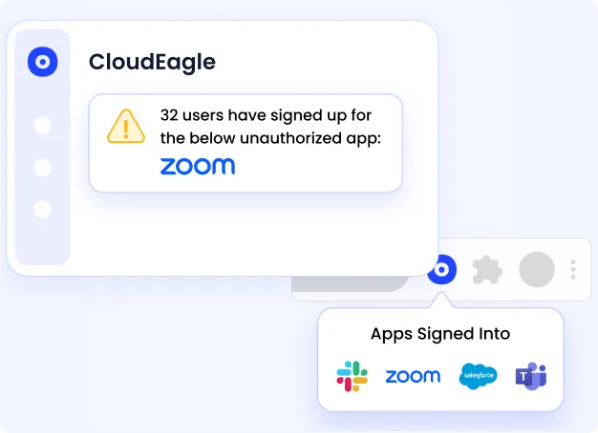
- Productivity goes up, and so do unmanaged endpoints on your network.
- These devices often lack encryption, mobile device management, or current updates.
- Personal devices without strict access policies put protected health information (PHI) at significant risk.
Limited IT Resources
Many healthcare IT teams are small and stretched across thousands of endpoints in multiple facilities. Pressure leads to overlooked details, and overlooked details lead to breaches.
Without automation, that produces:
- Delays in patch deployment.
- Slow incident response.
- Gaps in endpoint visibility.
High Stakes and Zero Tolerance for Downtime
Healthcare has no room for downtime. An endpoint that goes offline during surgery prep or emergency response can have critical consequences.
Endpoints must be:
- Continuously monitored for health and performance.
- Equipped with real-time threat detection.
- Easy to recover after a compromise.
A locked or infected device can delay a diagnosis, interrupt treatment, or block access to critical patient data.
4. How Does Endpoint Management for Hospitals Work?
Endpoint management for hospitals adds constraints that a typical enterprise rollout never faces: shared devices, clinical equipment, and 24/7 operations.
Shared Workstations and Rounding Devices
- Workstations on wheels, kiosks, and nursing-station PCs are used by many staff across a shift.
- Badge-tap sign-on and fast user switching keep clinicians moving without weakening authentication.
- Short idle timeouts with quick resume protect PHI without forcing a full password re-entry every time.
Medical Devices That Can't Run Agents
- Infusion pumps, imaging systems, and monitors often can't run endpoint agents or accept patches on a normal schedule.
- Your team protects them through accurate inventory, network segmentation, and passive monitoring.
- Patch timing for these devices is coordinated with clinical engineering, not pushed automatically.
Round-the-Clock Patching
- There is no quiet overnight window for every unit.
- Stagger patch rings by department, start with a small pilot group, and keep a rollback plan.
Mixed Ownership
- Hospital-owned, clinician-owned, and vendor-managed devices all touch the same network.
- Give vendors time-bound access for remote support, and revoke it when the work ends.
EHR Access Tied to Device Posture
- The EHR is your most sensitive system, so gate it on device condition, not just a valid login.
- A device that fails its health check should lose EHR access until it is fixed.
5. What Are the Essential Components of Healthcare Endpoint Security and Management?
Before you balance security with accessibility, you need a solid foundation. Healthcare endpoint security has to account for complex patient workflows, remote users, compliance needs, and high-value data without interrupting care.
Centralized Endpoint Visibility
You can't secure what you don't know exists. Healthcare environments run thousands of endpoints across departments, from imaging rooms to mobile nursing stations.
- A unified dashboard shows every connected device, online or idle.
- Tools like ManageEngine or Microsoft Intune let your team locate, tag, and monitor endpoints by department, user, or risk level.
- Visibility exposes unauthorized devices on patient networks, supports segmentation by role or location, and removes blind spots attackers exploit.
Automated Patch Management
Missing patches are a major cause of breaches. In a Ponemon Institute study for ServiceNow, 60% of breach victims across industries said the breach came through a known vulnerability where a patch was available but not applied.
- Automation schedules and applies updates without manual input.
- Define patching windows that avoid disrupting patient care, such as night shifts or after-hours operations.
- Fewer human errors, higher uptime for EHRs and imaging tools, and current software for compliance.
With so many devices and so little IT bandwidth, automation is the only scalable way to stay patched.
Role-Based Access Control (RBAC)
A radiologist doesn't need billing data, and an admin assistant shouldn't open medical records. RBAC ties access to roles like doctor, nurse, and admin instead of individuals.
- Users get only what they need to do their jobs.
- Onboarding and offboarding get simpler because permissions follow the role.
- It supports HIPAA's minimum necessary standard and cuts insider risk and accidental exposure.
Encryption and Remote Wipe
Mobile devices in hospitals get misplaced. A lost, unencrypted tablet can expose thousands of patient records and trigger HIPAA breach notification.
- Full-disk encryption makes data unreadable without credentials, on laptops and mobile devices alike.
- Remote wipe lets IT erase a lost or stolen device and can fire automatically on suspicious behavior.
- Together they protect data even outside your network perimeter.
Compliance and Audit Reporting
Regulators expect detailed records of how data is accessed, transmitted, and secured. Without logging, proving HIPAA compliance gets painful fast.
- Modern tools log device actions automatically: logins, patch updates, data transfers, and policy violations.
- Logs export for internal review or external audits.
- Reporting speeds up audits, increases transparency, and flags misconfigurations before they become breaches.
Endpoint Detection and Response (EDR)
Even with tight defenses, zero-day threats and phishing can succeed. EDR catches suspicious behavior and reacts in real time.
- EDR monitors endpoint activity continuously and can isolate a device the moment it behaves abnormally.
- It stops ransomware before it spreads laterally and provides forensics for root-cause analysis.
- Recovery is faster, with less widespread downtime.
A strong strategy pairs centralized visibility for oversight, automated patching for consistency, and RBAC for precise access control.

6. What Is Endpoint Health, and How Do You Monitor It?
Endpoint health is the current security and operational condition of a device measured against your policy. A healthy endpoint is patched, encrypted, protected, and reporting in.
What to Track
- Operating system and patch level.
- Encryption status.
- Whether the EDR or management agent is running and reporting.
- Last check-in time.
- Compliance with configuration policy.
- Known unresolved vulnerabilities.
- Jailbroken or rooted status on mobile devices.
How to Monitor It
- Set compliance policies in your UEM tool, such as Microsoft Intune, and score each device against them.
- Alert on drift: a device that misses patches or stops checking in.
- Quarantine non-compliant devices from the EHR until they are remediated.
Why It Matters in Healthcare
- Health signals feed context-aware access, so risky devices lose access before they cause harm.
- They give early warning on failing carts and kiosks before they go down mid-shift.
- They produce the evidence auditors ask for.
7. Which Strategies Balance Security and Accessibility in Healthcare Endpoint Management?
Securing healthcare endpoints isn't only about restricting access. Clinicians, nurses, and staff also need quick, easy access to systems and data to provide care.
Unified Endpoint Management (UEM)
UEM platforms manage desktops, mobiles, and tablets from a single console.
- Less management overhead.
- Consistent security policy across devices.
- Faster troubleshooting.
Context-Aware Access
This approach checks user behavior, device health, and location before granting access. A doctor on a trusted hospital device gets in faster than one on an unknown laptop.
- Dynamic security without added delay.
- Unusual access flagged in real time.
- Routine tasks stay unblocked.
Multi-Factor Authentication (MFA)
MFA requires more than a password, like a mobile code or biometric scan, which blocks many common attacks, especially phishing.
- Secures remote and mobile access.
- Supports HIPAA's access control requirements, and the proposed Security Rule update would make MFA mandatory.
- Minimal impact on clinical workflow when paired with badge or biometric sign-on.
Just-In-Time (JIT) Access
Instead of permanent access, just-in-time access grants temporary permissions that expire automatically.
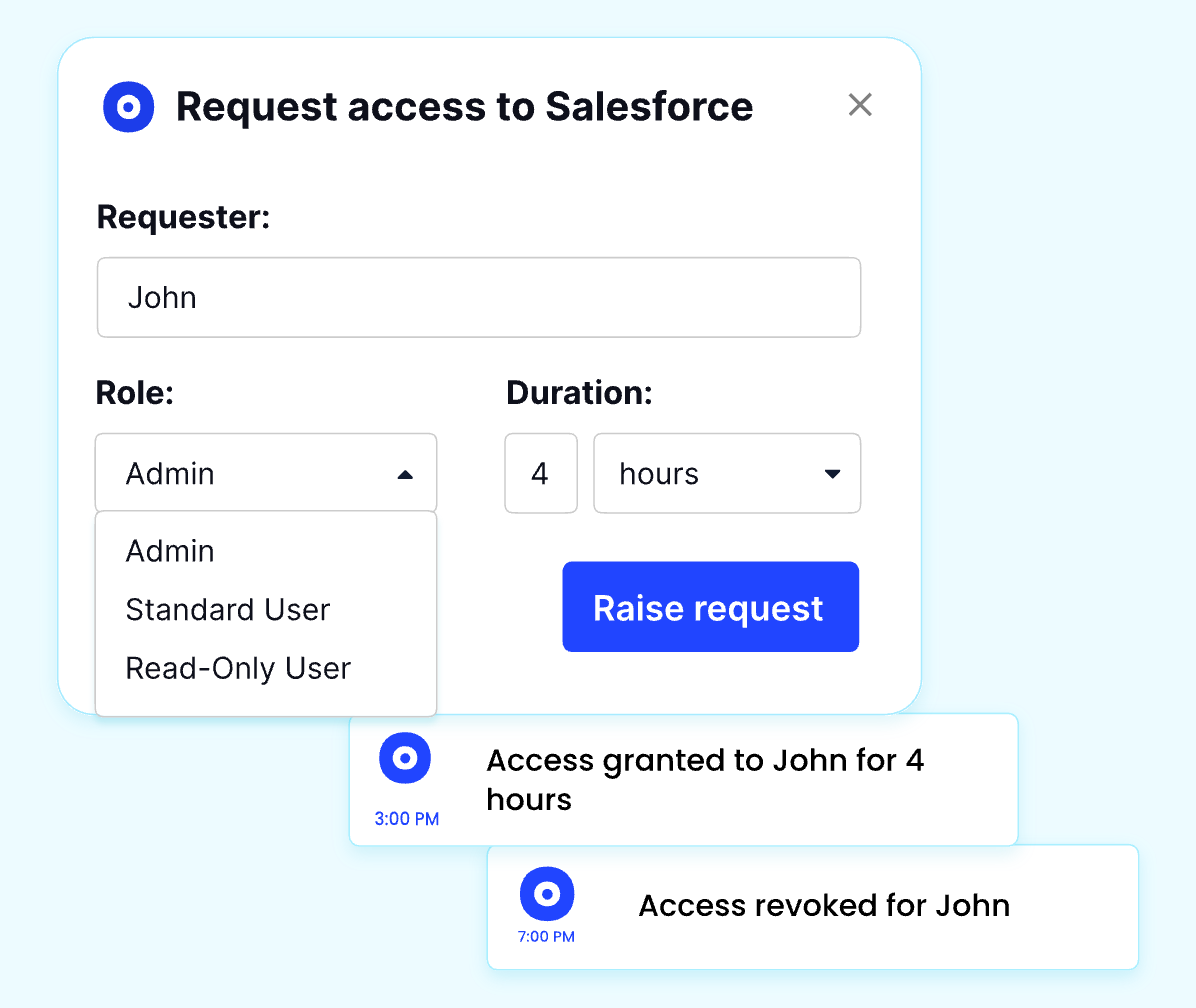
- Removes standing access risk.
- Produces audit-friendly access logs.
- Keeps least privilege intact.
Zero Trust Framework
Zero Trust verifies identity, device health, and location before every access, which suits environments where users move across many systems.
- Blocks lateral movement of threats.
- Applies strict verification at every step.
- Protects you even when perimeter defenses fail.
8. What Common Pitfalls Undermine Healthcare Endpoint Management?
Even with the right tools, endpoint management in healthcare fails when these mistakes slip through.
Overlooking BYOD Risks
Healthcare workers use their own phones and tablets for patient data, schedules, and team chat. Without proper onboarding into a secure MDM system, those devices become high-risk entry points.
- Require every BYOD device to be registered and enrolled in MDM.
- Enforce encryption, password protection, and remote wipe.
- Restrict access until compliance is confirmed.
One-Size-Fits-All Policies
Identical restrictions for a surgeon and front-desk staff disrupt workflows and breed workarounds.
- Build role-based access profiles.
- Tailor device restrictions to department needs.
- Test usability with real users.
Ignoring the Endpoint Lifecycle
Old laptops, idle kiosks, and unused mobile carts stay on the network if nobody decommissions them, often with outdated software and stored credentials.
- Track devices from onboarding to retirement.
- Remove unused devices from the network.
- Wipe and securely dispose of retired hardware.
Lack of Real-Time Monitoring
Monthly or quarterly audits won't catch live threats. A device can be compromised in hours, sometimes minutes, and go unnoticed.
- Use real-time EDR tools.
- Set automated alerts for suspicious behavior.
- Review access logs and device health metrics regularly.
9. How Do You Get Healthcare Endpoint Management Right?
Effective endpoint management is crucial in healthcare because it balances security with accessibility. Centralize visibility, automate patching, enforce role-based access, and avoid pitfalls like BYOD blind spots and missing real-time monitoring.
CloudEagle.ai is an AI-powered AI governance, SaaS management and SaaS security platform that gives enterprises one command center to discover, secure, govern, and manage their entire SaaS and AI stack.
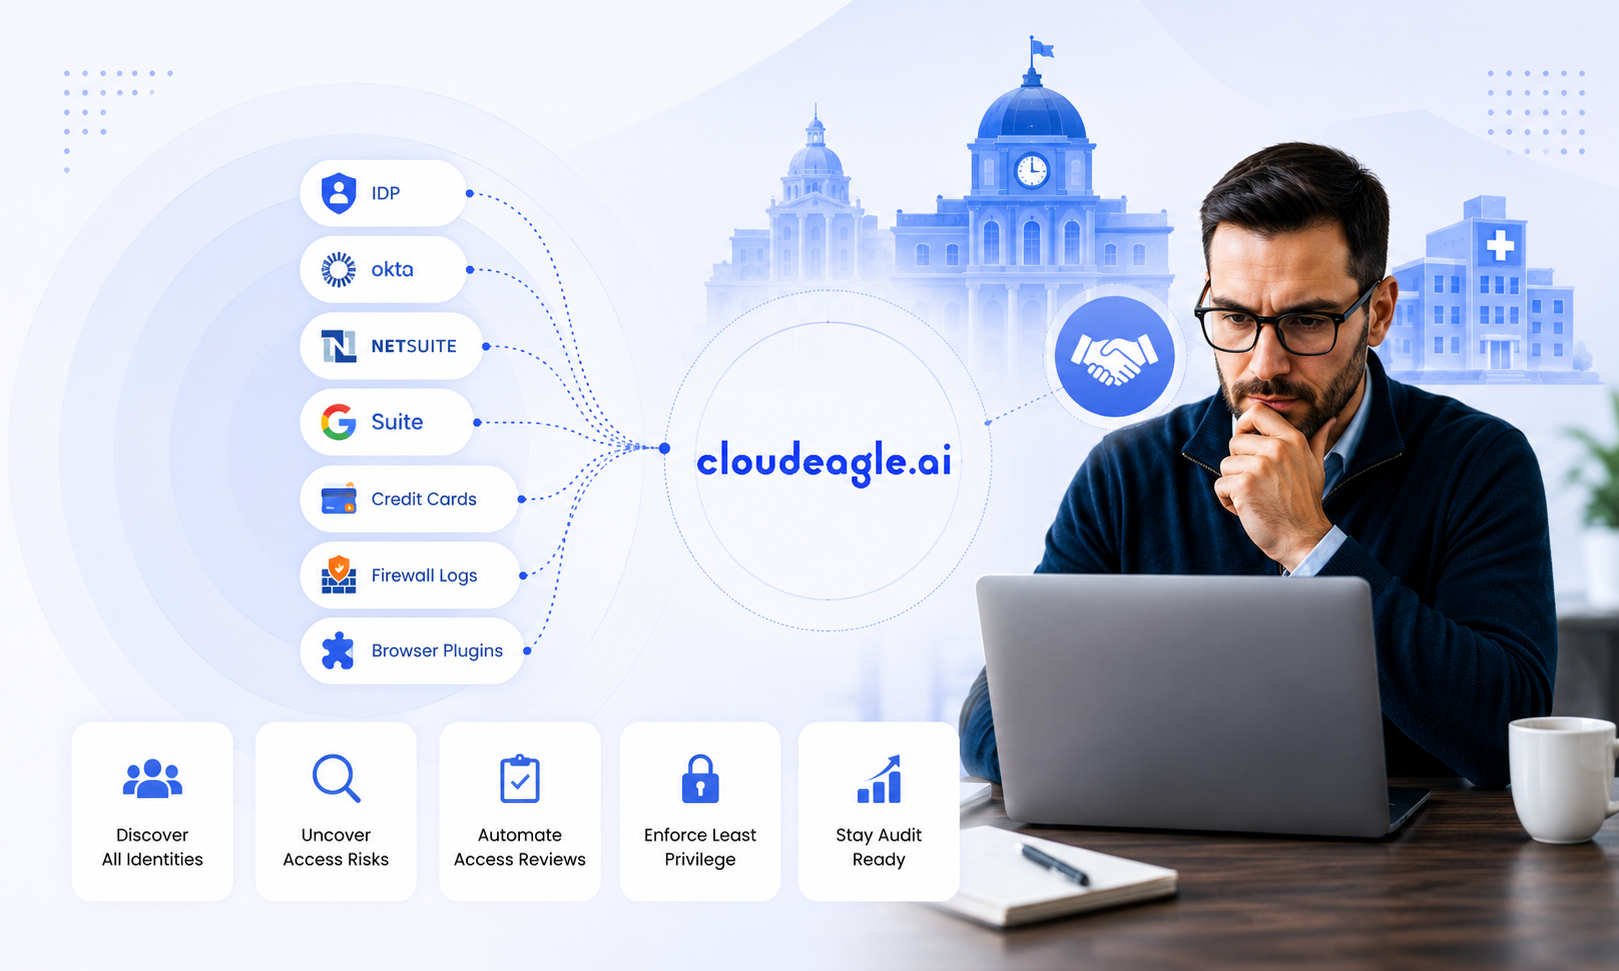
Your UEM, MDM, and EDR tools manage the device. We help your IT and security team govern what that device can reach in your clinical and administrative apps:
- Automated onboarding and offboarding so access follows the role and ends when the role does.
- Time-bound access for vendors, contractors, and temporary staff.
- Continuous user access reviews with HIPAA-ready audit trails for PHI access.
- Shadow IT and shadow AI discovery for the unapproved apps clinicians adopt on their own.
Want to see how that fits your environment? Book a demo with CloudEagle.ai.
Secure the Device. Govern What It Can Access.


Frequently Asked Questions
- What Is an Endpoint in Healthcare?
An endpoint in healthcare is any device, such as a laptop, tablet, or piece of medical equipment, that connects to a network and handles patient data or clinical applications. - What Is Endpoint Management for Healthcare?
Endpoint management for healthcare means monitoring, securing, and updating all devices on a network to protect sensitive patient data and keep clinical operations running smoothly. - What Is Endpoint Health?
Endpoint health is how closely a device matches your security and configuration policy: patched, encrypted, protected, and reporting in. Monitoring it lets you restrict access from risky devices before they cause harm. - What Is the Difference Between Endpoint Management and MDM?
Endpoint management covers all device types and functions. MDM (Mobile Device Management) focuses specifically on smartphones and tablets in mobile environments. - What Is the Difference Between Healthcare Endpoint Security and Endpoint Management?
Healthcare endpoint security focuses on detecting and stopping threats, with tools like EDR. Endpoint management is broader and covers device control, patching, configuration, and inventory. - Does HIPAA Require MFA and Encryption on Healthcare Endpoints?
Today's HIPAA Security Rule treats encryption as an addressable safeguard and doesn't explicitly require MFA, though both support its access and transmission requirements. HHS has proposed making both mandatory, and the current rule remains enforceable until a final rule replaces it.
Secure the Device. Govern What It Can Access.