HIPAA Compliance Checklist for 2025

TL;DR
- Lacework is a solid cloud security platform, but its pricing, learning curve, and limited SaaS visibility lead many teams to look at Lacework competitors.
- Top Lacework alternatives include CloudEagle.ai, Prisma Cloud, Orca Security, Sysdig Secure, Qualys Cloud Platform, Threat Stack, and Wiz Security.
- These alternatives stand out for agentless deployment, full-stack and SaaS security, automated compliance, and more flexible pricing models.
- CloudEagle.ai stands out for SaaS visibility and spend optimization, while Wiz and Orca offer agentless cloud protection with strong risk prioritization.
- Choosing the right tool depends on your priority: compliance, cost efficiency, DevSecOps integration, or holistic SaaS management.
As organizations scale their cloud infrastructure, securing workloads, identities, and data becomes a growing concern.
With rising cloud complexity and evolving compliance demands, businesses are exploring Lacework alternatives that offer stronger features, better pricing, or more direct integrations.
In this blog, we'll cover the top 7 Lacework alternatives and what makes each one stand out, so you can pick the best fit for your cloud security needs.
1. What Is Lacework, and How Does Its Cloud Security Platform Work?
Lacework is a cloud security posture management platform built to provide security and compliance coverage for cloud environments.
It offers automated vulnerability detection, threat identification, and cloud compliance across platforms like AWS, Google Cloud, and Azure, as well as Kubernetes configurations.
Lacework's approach is cloud-native and delivered as-a-service, automating security tasks so organizations can move fast without cutting corners on safety. With deep visibility into AWS, Azure, and GCP, it helps organizations detect anomalies, misconfigurations, and vulnerabilities using a data-driven behavioral approach.
Key Features of Lacework
- Cloud workload protection (CWPP).
- Container and Kubernetes security.
- Compliance assessments, including SOC 2 and PCI-DSS.
- Runtime threat detection.
- Risk-based prioritization.
Despite its capabilities, many organizations find Lacework's pricing model restrictive, or want more flexibility and usability, which is what leads them to explore alternatives.
2. What Are the Limitations of Lacework?
While Lacework remains a solid solution, it does present certain drawbacks:
- Pricing complexity: Lacework's pricing isn't transparent and can run steep for growing teams or SMBs.
- Steep learning curve: The platform can be overwhelming for security teams new to behavioral analytics or agent-based solutions.
- Limited SaaS visibility: Lacework focuses heavily on cloud infrastructure but offers minimal SaaS-specific visibility or license management.
These gaps are exactly what open the door for Lacework competitors that offer more holistic SaaS security, FinOps visibility, and a more tailored user experience.
3. What Are the Best Lacework Alternatives for Cloud Security in 2026?
Some businesses find Lacework's pricing steep, or want tools with better SaaS visibility, easier deployment, or deeper DevOps integrations. Here are the top 7 Lacework alternatives worth evaluating.
1. CloudEagle.ai
CloudEagle.ai takes a SaaS-focused approach to security, governance, and access management. While Lacework focuses primarily on cloud infrastructure security,
It helps organizations discover, govern, and secure SaaS and AI applications across the enterprise, including applications outside traditional SSO and IT visibility.
Discover Shadow IT and Shadow AI, and Uncover Hidden Risks
CloudEagle.ai takes a SaaS-focused approach to security, governance, and access management.
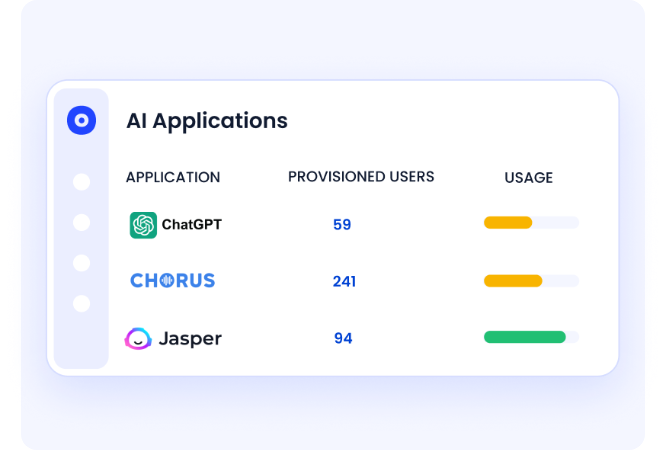
While Lacework focuses primarily on cloud infrastructure security, CloudEagle.ai helps organizations discover, govern, and secure SaaS and AI applications across the enterprise, including applications outside traditional SSO and IT visibility.
Identity and Access Management, Reinvented
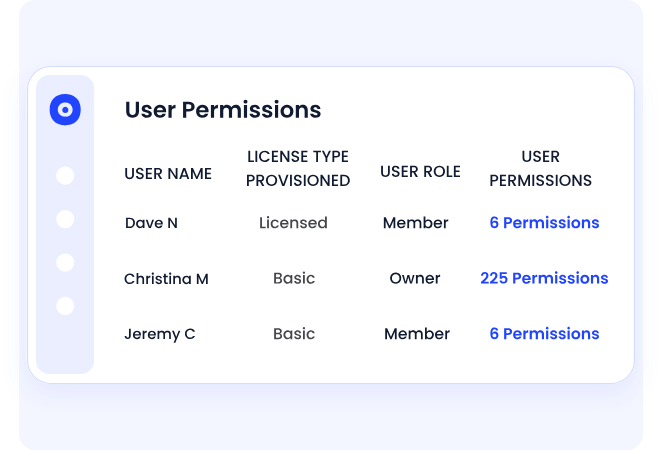
CloudEagle.ai extends access governance across SaaS and AI applications, including applications that may not be connected to the organization's primary identity provider.
- Zero-touch provisioning: Assign applications based on factors such as role and department to reduce manual access requests.
- Automated offboarding: Revoke application access when employees leave, including access to applications outside the IDP.
- Audit-ready access reviews: Run scheduled or on-demand reviews with access records and governance workflows.
Our research found that 48% of former employees still retain access to business-critical tools. See the report.
Just-in-Time and Privileged Access Management
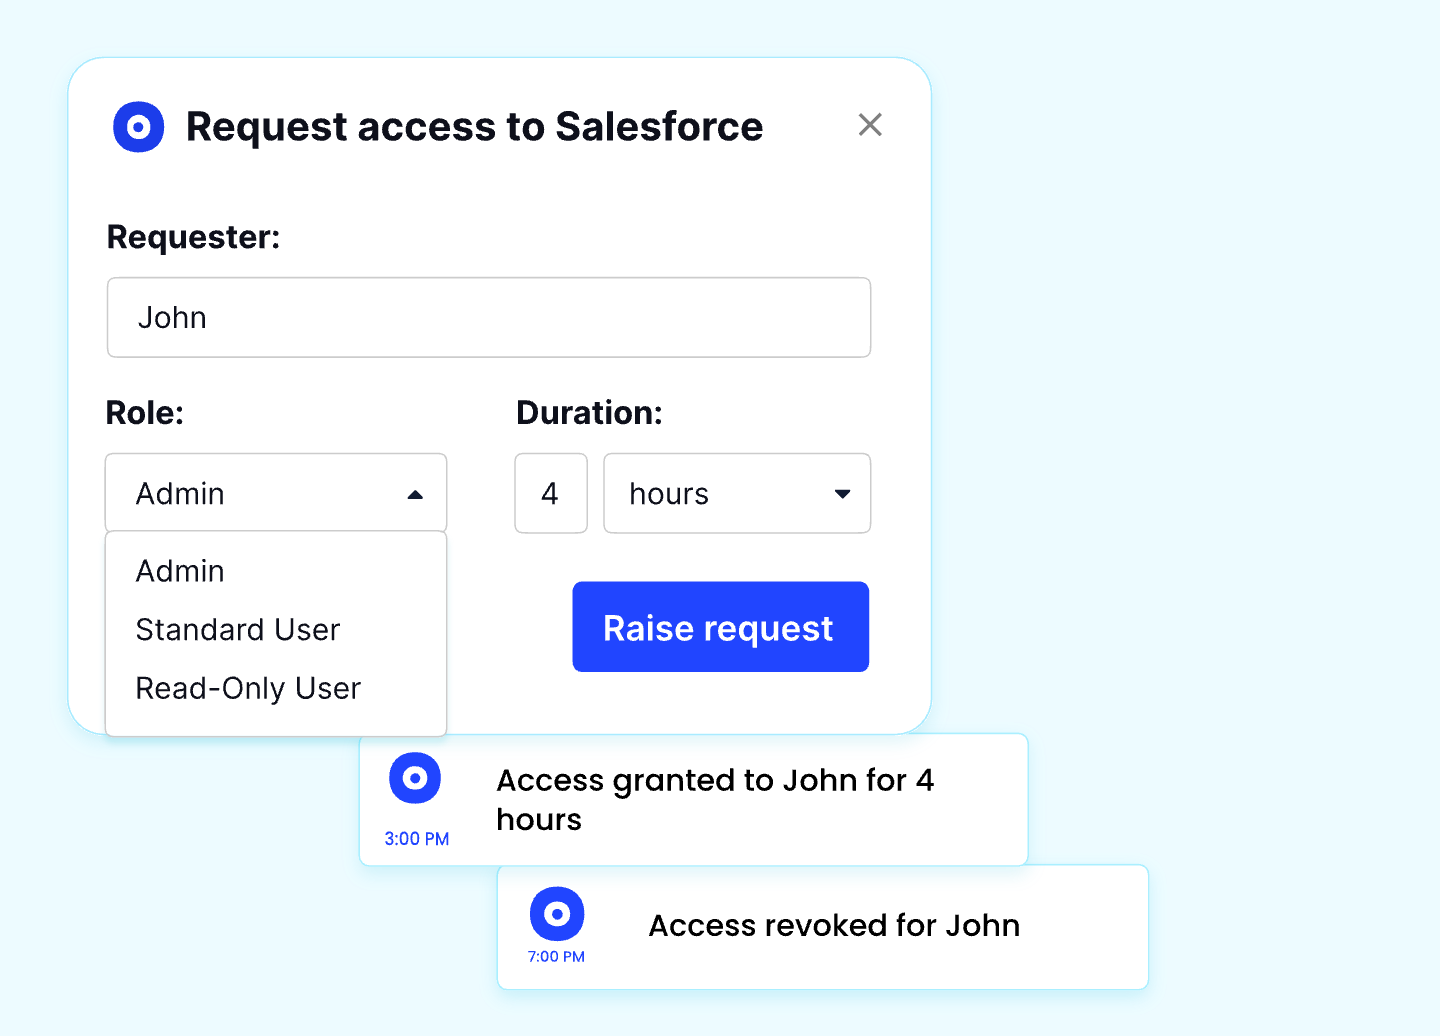
CloudEagle.ai helps organizations apply least-privilege principles to SaaS access by identifying unnecessary privileges and supporting time-bound access for contractors and temporary users.
- Time-based, self-expiring access: Limit access for temporary users and high-risk roles to the period when it is required.
- Privileged access visibility: Identify excessive administrative permissions and unusual access patterns.
- Audit trails: Maintain records of provisioning and access changes to support security and compliance reviews.
"We had contractors finishing engagements and their accounts staying active for months. Nobody was tracking it. CloudEagle.ai showed us contractor accounts with no activity in 90 days. We cleaned it up in days, automated the offboarding process, and cut the tickets our IT team."
~ Lisa Chamberlain, VP, Assistant Controller, Coherus Oncology
AI-Powered Access Reviews and Security Compliance
Modern security takes more than quarterly audits. We run continuous, AI-driven access reviews that detect stale permissions, flag overprivileged users, and automate deprovisioning, including coverage for AI tools like ChatGPT, DeepSeek, and beyond.
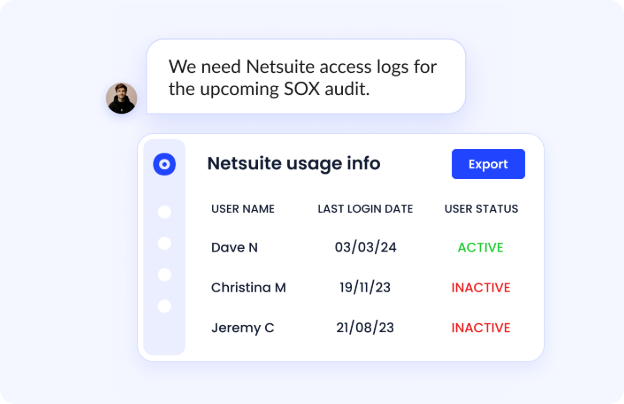
- Risk scoring: Assess user access and application usage to identify higher-risk accounts and permissions.
- Workflow automation: Route access issues for remediation and support automated deprovisioning where appropriate.
"We lacked confidence in our access certifications. Reviews were happening, but we couldn't clearly answer who had access, why it existed, or whether it was still valid. CloudEagle brought structure and accountability to user access reviews without reviewer fatigue."
~ Michal Lipinski, Director of IT & Security, ICEYE
Reclaim Unused Licenses and Eliminate Wasteful Spend
We track feature-level usage, not just logins, so your IT and finance teams can right-size license allocations and remove idle accounts.
- License harvesting workflows: Identify unused seats and reclaim licenses through defined workflows.
- Application rationalization: Identify overlapping tools and opportunities to consolidate or adjust subscriptions before renewal.
- License reallocation: Reassign available licenses based on current usage rather than purchasing additional seats unnecessarily.
Contract Intelligence and Renewal Management
Never miss a renewal or overpay again. Our AI-powered contract repository centralizes vendor agreements, extracts key metadata, and builds a proactive renewal calendar.
- Auto-detects renewal dates, license counts, SKUs, and opt-out windows.
- Sends renewal alerts and automates Slack and Jira approval workflows.
- Benchmarks pricing to help you renegotiate smarter.
Our Procurement Intelligence and price benchmarking engine gives buyers vendor-specific insight, pre-negotiated discounts, and cost benchmarks by license tier, so your procurement team can negotiate renewals and new purchases with real usage data instead of guesswork.
CloudEagle.ai also connects SaaS security and governance with broader compliance requirements, including SOC 2, HIPAA, and ISO 27001, while providing visibility into application security posture, certifications, and other risk signals.
Pricing: Module-based pricing; confirm current figures before publishing, as pricing and packaging may change.
What Happens When SaaS Security Becomes Part of the Stack?
2. Prisma Cloud by Palo Alto Networks
Prisma Cloud is Palo Alto's flagship cloud-native security platform, offering full-stack protection from code to cloud. It's widely adopted by large enterprises for its depth of coverage and unified approach.
Features
Prisma Cloud supports CSPM, CWPP, CIEM, and container security, making it a fit for hybrid and multi-cloud environments. It secures infrastructure as code, provides real-time monitoring, and enforces policy across CI/CD pipelines, with compliance coverage for standards like PCI-DSS, NIST, and GDPR.
Pros
- Covers the full software lifecycle, from code development through production deployment.
- Integrates closely with popular CI/CD tools, cloud providers, and DevOps pipelines, enabling continuous monitoring and automated remediation.
- Strong compliance management, with built-in policy automation, audit-readiness tools, and support for SOC 2, HIPAA, and ISO 27001.
Cons
- Can be complex to set up and configure, especially for smaller teams without a dedicated DevSecOps function.
- Premium pricing that may be a stretch for startups, with a learning curve given the platform's breadth of features.
Pricing: Typically starts at $1,000/month or more, depending on cloud accounts, integrations, and compliance modules. Custom enterprise pricing available.
3. Orca Security
Orca Security is a cloud security platform known for its agentless architecture and fast deployment, delivering prioritized, contextual alerts without disrupting workloads.
Features
It scans the entire cloud environment without deploying agents, identifying misconfigurations, malware, and exposed secrets. Orca provides asset inventory, risk prioritization, and lateral movement detection through context-aware analysis, with attack-path analysis to help teams focus on the most critical risks.
Pros
- Agentless scanning means fast, efficient assessments with no heavy load on system performance and no invasive installs.
- Fast time-to-value through contextual insight across cloud assets.
- Strong alert prioritization that cuts noise and false positives so teams focus on high-impact threats.
Cons
- Doesn't offer full runtime protection, which can leave gaps in monitoring live, in-production environments.
- May need third-party tools to reach complete compliance coverage or advanced governance.
Pricing: Generally $500-$1,500/month, depending on environment size and assets scanned. Enterprise pricing available for larger deployments.
4. Sysdig Secure
Sysdig Secure is built for containerized environments and DevOps teams securing Kubernetes clusters and cloud-native workloads, with an emphasis on runtime security and observability.
Features
Sysdig delivers real-time threat detection using syscall-level data and behavioral profiling of container activity, plus Kubernetes posture management and compliance enforcement. It integrates with CI/CD pipelines to shift security left in the development lifecycle.
Pros
- Purpose-built for containerized and microservices architectures on platforms like Kubernetes and Docker.
- Strong runtime visibility and threat detection, so teams can watch container activity live and respond quickly to anomalies.
- DevSecOps-friendly, with automation built for CI/CD pipelines so security doesn't slow development down.
Cons
- Focused primarily on container security, which limits its usefulness outside Kubernetes environments.
- Depth and complexity can mean real training and onboarding time, especially in complex multi-cloud or hybrid setups.
Pricing: Typically $2,000-$3,000/month based on nodes or containers monitored. Enterprise pricing and custom packages available.
5. Qualys Cloud Platform
Qualys is a pioneer in vulnerability management, and its Cloud Platform extends that into hybrid and cloud-native environments, combining security, compliance, and asset management in one place.
Features
Qualys scans your infrastructure for vulnerabilities, configuration issues, and unauthorized changes, with continuous visibility across devices, VMs, containers, and apps, plus real-time threat indicators and patch management.
Pros
- An established, trusted name with mature vulnerability management and compliance capabilities.
- Scales well for large enterprises with complex, global infrastructure.
- Continuous, automated scanning that helps maintain strong security hygiene.
Cons
- The interface feels dated next to newer platforms, which can hurt usability for first-time or non-technical users.
- Reporting is powerful but often needs real customization to produce executive-ready dashboards.
Pricing: Typically starts at $2,000/month or more, depending on assets, scanning frequency, and modules. Volume discounts and enterprise packages available.
6. Threat Stack (Acquired by F5)
Threat Stack offers cloud-native intrusion detection and workload security, and is popular in regulated industries like healthcare, finance, and SaaS, where runtime monitoring and compliance matter most.
Features
It monitors users, processes, and network behavior in real time to detect threats, with built-in compliance reporting for HIPAA, SOC 2, and PCI-DSS, and lightweight agents across Linux and Windows environments for deep observability.
Pros
- A strong choice for compliance-driven organizations, with built-in support for PCI DSS, HIPAA, and SOC 2, plus detailed audit and reporting tools.
- Lightweight agents deliver real runtime protection without a heavy performance hit.
- Strong behavioral monitoring that flags anomalies and suspicious activity based on real-time user and system behavior.
Cons
- Focused mainly on detection rather than proactive prevention, which may mean pairing it with other tools to close the loop.
- Narrower cloud coverage and multi-environment support than broader Cloud-Native Application Protection Platforms (CNAPPs).
Pricing: Starts around $1,500-$3,000/month, varying by workloads, cloud accounts, and compliance modules. Enterprise pricing available.
7. Wiz Security
Wiz has emerged as a fast-growing Lacework competitor, offering agentless cloud security with full-stack visibility into your cloud environment. It's widely used for its simplicity, speed, and risk correlation.
Features
Wiz scans across VMs, containers, databases, identities, and workloads with no agents required, using a graph-based analysis engine to detect toxic combinations and exposure paths that could lead to breaches. It integrates directly into cloud-native DevOps workflows.
Pros
- Easy to deploy thanks to its agentless architecture, with fast onboarding and minimal disruption to existing cloud operations.
- A strong risk-prioritization engine that pulls context from workloads, configurations, and identities to surface the most critical threats first.
- Broad support for all major cloud providers, including AWS, Azure, and Google Cloud, from a single dashboard.
Cons
- Positioned as a premium enterprise solution, which may not suit smaller or budget-constrained teams.
- Limited in deep historical trend analysis or advanced reporting out of the box.
Pricing: Generally starts at $3,000/month or higher, depending on cloud footprint, resources, and features required. Enterprise licensing and volume discounts typically available.
4. Which Lacework Alternative Offers the Strongest Threat Detection?
Lacework's core strength is behavioral, data-driven threat detection, so if that's specifically what you're replacing, three alternatives are worth a closer look.
Sysdig Secure gets closest to Lacework's own approach, with syscall-level behavioral profiling built for runtime detection inside containers and Kubernetes.
Threat Stack pairs lightweight agents with real-time behavioral monitoring of users, processes, and network activity, and leans harder into compliance reporting than Sysdig does.
Wiz takes a different route entirely: agentless, graph-based detection that correlates identities, configurations, and workloads to surface toxic combinations rather than relying on runtime agents at all.
None of these map onto CloudEagle.ai, since our detection surface is SaaS access and identity risk rather than cloud workload behavior. If workload-level detection is the gap you're closing, Sysdig, Threat Stack, or Wiz are the three to shortlist.
5. Which Lacework Alternative Is Right for You?
Lacework continues to be a solid player in cloud security, but it isn't a one-size-fits-all solution.
Whether you need stronger SaaS oversight, better cost efficiency, or a more developer-friendly toolset, the Lacework alternatives above cover most of the gap. From deep container insight with Sysdig to holistic SaaS security with CloudEagle.ai, there's a fit for most cloud security challenges.
If your stack is becoming SaaS-heavy and you're aiming for centralized security and cost governance, we're the modern layer Lacework doesn't fully cover.
Frequently Asked Questions
- Is Wiz Better Than Lacework?
Wiz offers a faster, agentless approach with deep risk context and prioritization. It can be a better fit for teams that want agility and full cloud-stack visibility without deploying agents. - What Are the Top Lacework Alternatives for Cloud Security?
The leading Lacework alternatives include CloudEagle.ai, Prisma Cloud, Orca Security, Sysdig Secure, Qualys Cloud Platform, Threat Stack, and Wiz Security, each with its own edge in agentless security, SaaS visibility, compliance coverage, or cost governance. - What Key Features Set Lacework Competitors Apart?
Lacework competitors tend to offer more transparent pricing, faster deployment through agentless or API-driven architectures, stronger SaaS discovery, automated compliance workflows, and a single dashboard for security, spend, and access. - Is Lacework Pricing Suitable for Small Businesses?
Lacework's pricing generally targets mid-market and enterprise customers. The lack of transparent, simple pricing can make it less accessible for small businesses, who might do better with alternatives like Orca Security or CloudEagle.ai that offer more scalable or tailored pricing. - What Are the Main Limitations of Lacework?
The main drawbacks are complex pricing, a steep learning curve, and limited SaaS application visibility. Organizations that need broader SaaS coverage or easier usability often look at other cloud security tools to complement or replace Lacework.
What Happens When SaaS Security Becomes Part of the Stack?